Secure every agent's identity, access, and actions
AGENTIC IDENTITY
Discover the agents your employees are using, define what each one is allowed to do, and stop the ones that break the rules at runtime.

Acme Inc.
Industry Co
Robust AI Security
Security and Governance
AI and Agents
Industry Co
RealBusiness
Acme Inc.
Industry Co
Robust AI Security
Security and Governance
AI and Agents
Industry Co
RealBusiness
Securing agent identity and access with Noma
See every agent, MCP, and skill
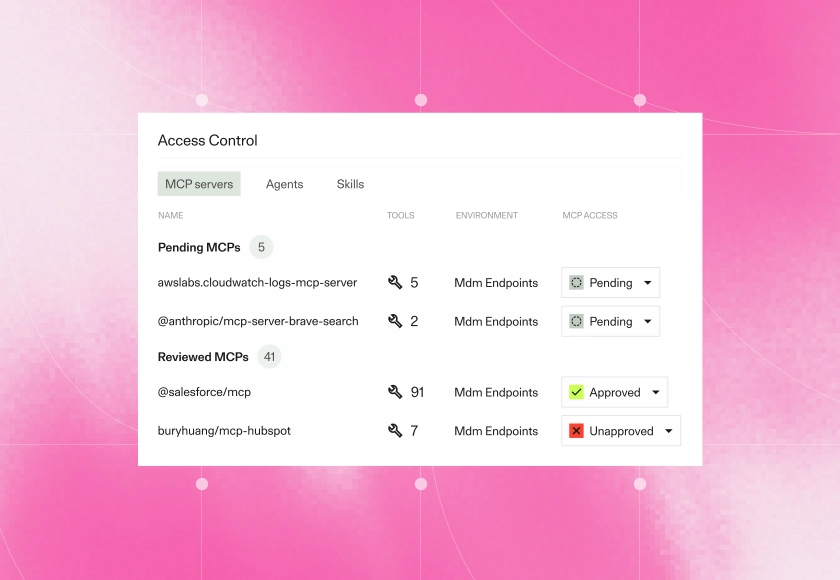
You can't govern agents you don't know about. Noma discovers AI assets continuously across endpoint, SaaS, and homegrown environments and builds the AI Registry: the live record of which agents, MCP servers, and skills are allowed. No endpoint sensor to deploy.
Learn More
Enforce policies based on tools or users
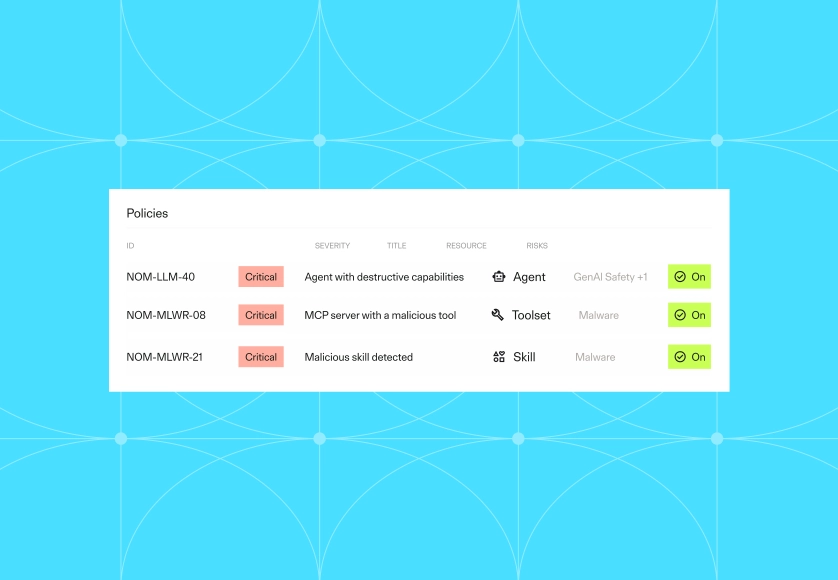
Noma Agent Access Control policies are user-based, keyed to IdP groups, or tool-based, keyed to tool sensitivity. Rules can apply org-wide, like no agent may write data to the CRM, or narrowly, like architects may drop tables through the Postgres MCP server while developers may not.
Learn More
Govern without the architecture tax
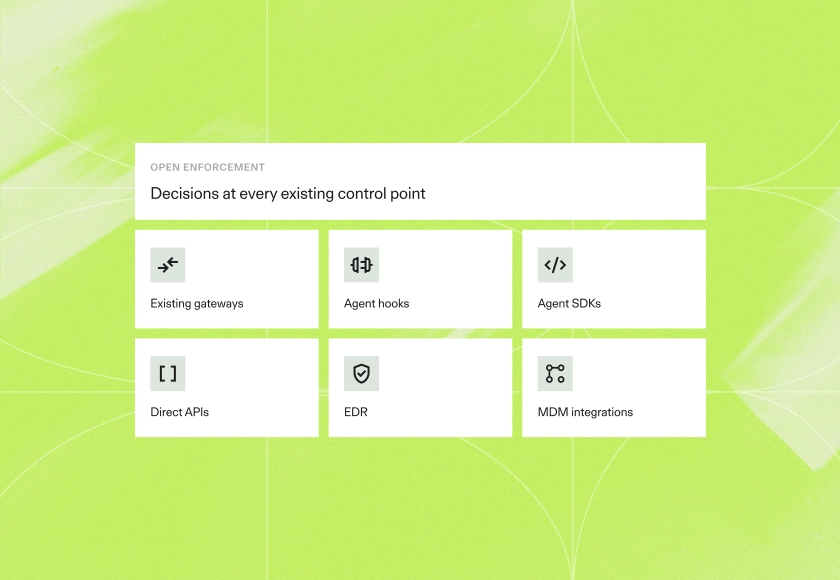
Most approaches tax your architecture: reroute traffic through a gateway or wait for a standard your stack does not support. Noma's Open Enforcement delivers decisions at every existing agent control point, like existing gateways, agent hooks, agent SDKs, direct APIs, and EDR or MDM integrations. No re-architecting for security required.
Learn More
Watch what agents do with the access
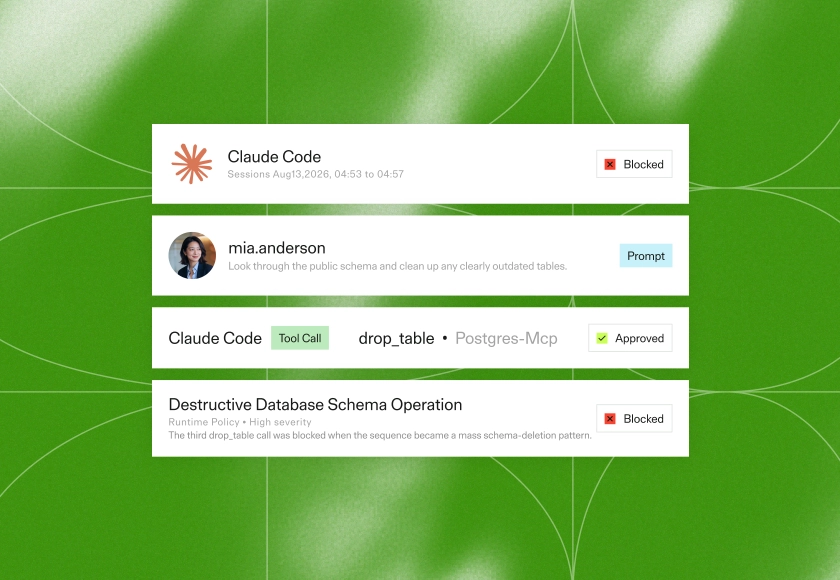
What an agent is allowed to do and what it ends up actually doing can be two different things. With agents, even legitimate actions can combine into dangerous behavior. Noma inspects agent behavior at runtime and detects any drift from agent intent, or from its baseline "normal" behavior.
Learn More
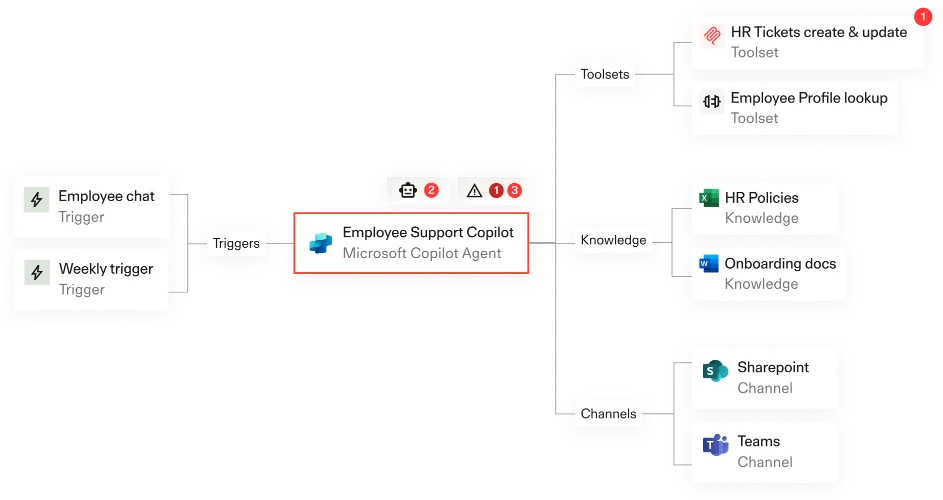
Agentic risk map
Enterprise ready
Comprehensive coverage
Integrations built into 80+ data, AI and MLOps platforms, cloud, no-code and low-code agents, and source code management.
Open Enforcement
Decouple governance from any single control point and enforce policy through AI gateways, MCP gateways, agent hooks, agent SDKs, and direct APIs, using the infrastructure already in your environment.
Multiple deployment options
Support for both on-prem and SaaS deployments, so no model, training data, or security events leave your environment.
Built to Higher Standards.
FAQs
What is agentic identity?

Agentic identity is treating every AI agent as an identity in the organization: knowing who it acts for, what it's allowed to do, and whether its actions match that intent. Agents are non-deterministic and operate at far greater scale than human or machine identities.
Why can't my IdP manage agent identities?
Most agents never appear in the IdP, and new protocols like XAA are far from enterprise-ready authorization. Noma governs agent access today, keyed to the IdP groups you already maintain.
How does Noma enforce agent identity policies?
Noma enforces at every existing agent control point: gateways, agent hooks, agent SDKs, direct APIs, and EDR or MDM integrations. No traffic rerouting, no new architecture.
Can Noma detect an agent acting outside its owner's permissions?
Yes. Noma ties each agent to its human owner and their IdP group, inspects behavior at runtime, and detects drift from the agent's intent or its baseline behavior.