How Noma AI agent runtime security works
Define what agents are allowed to do
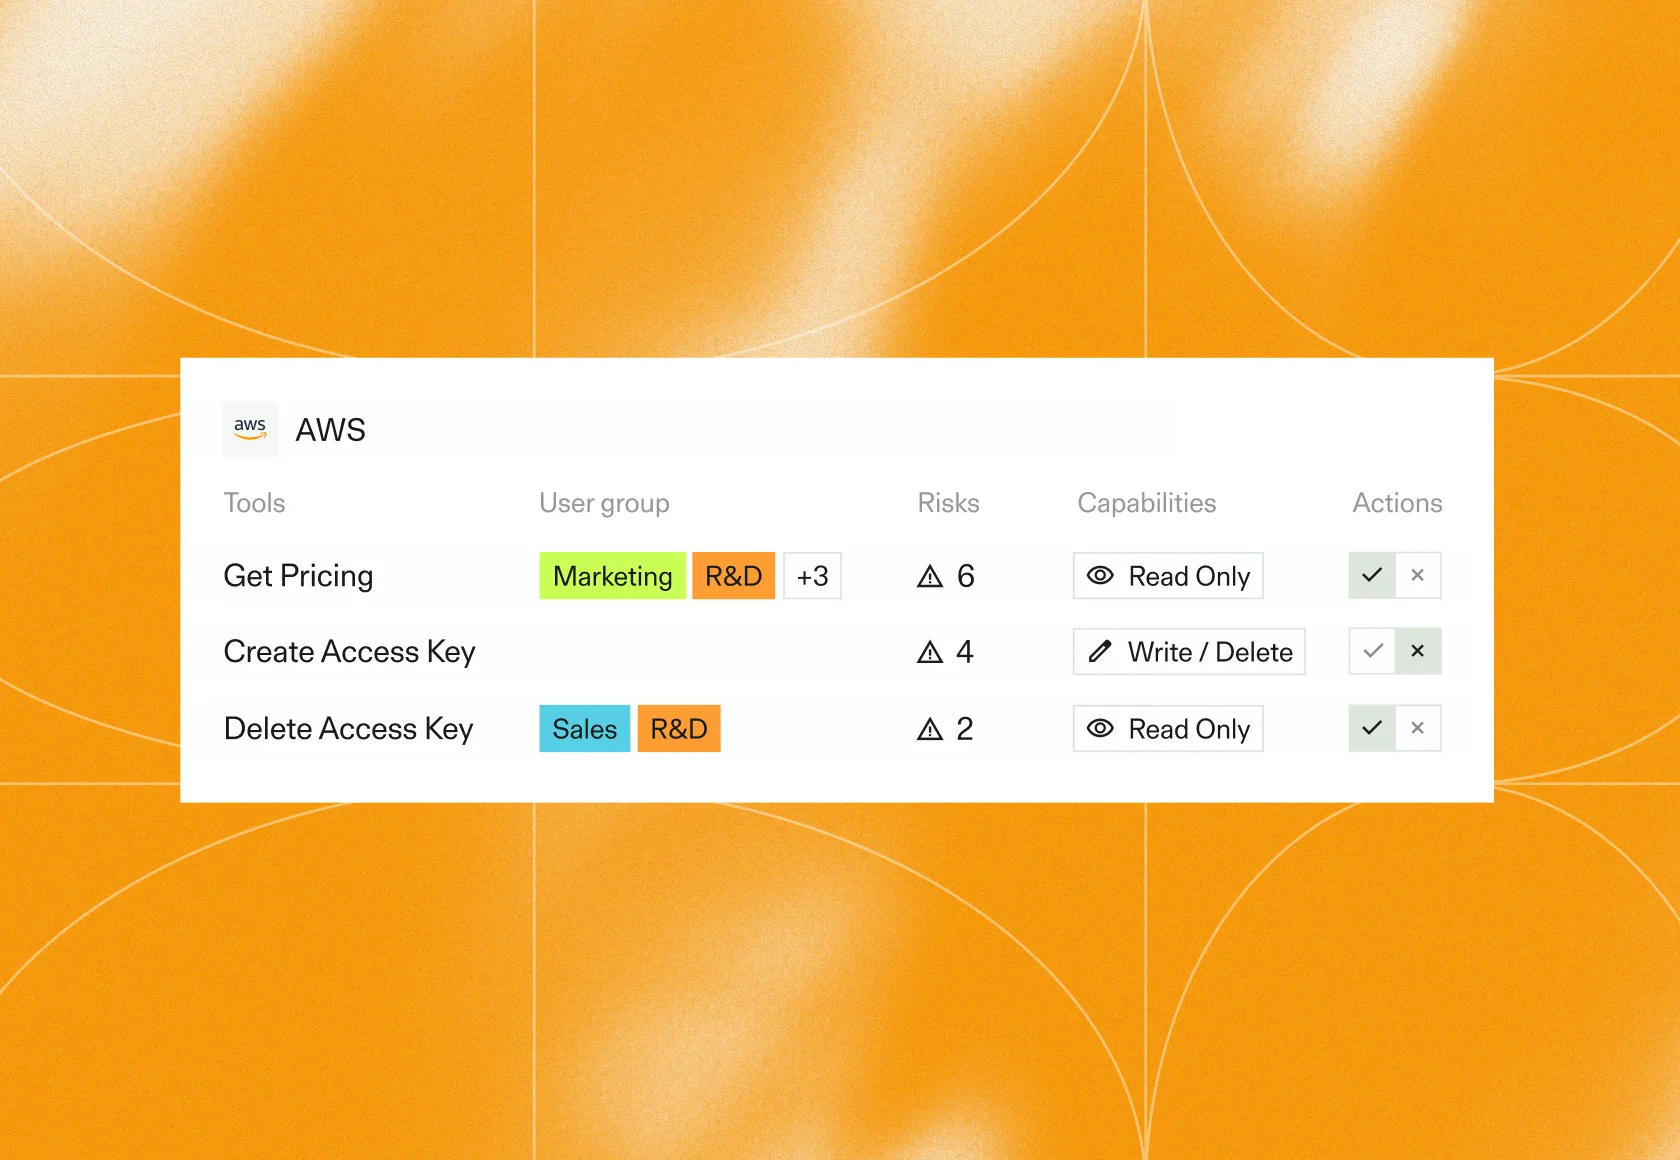
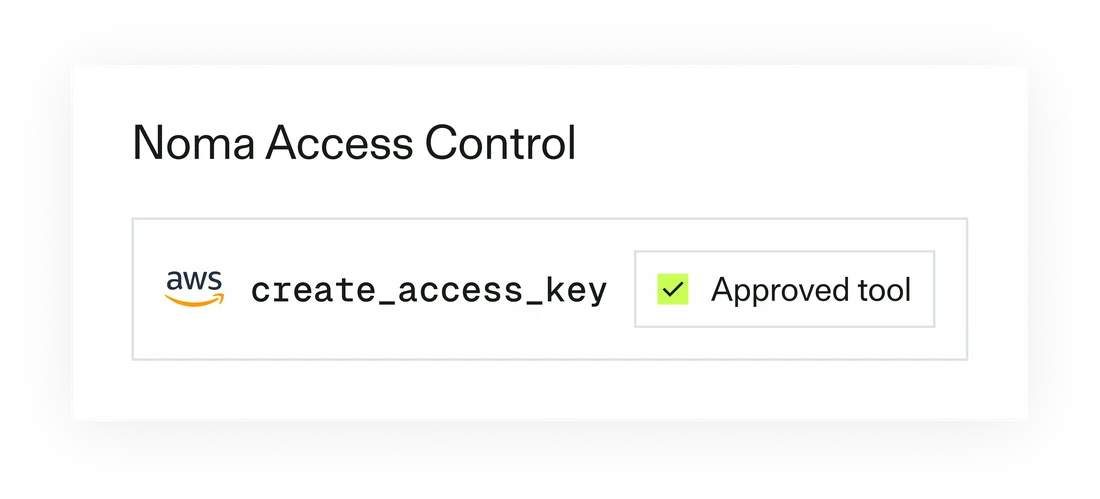
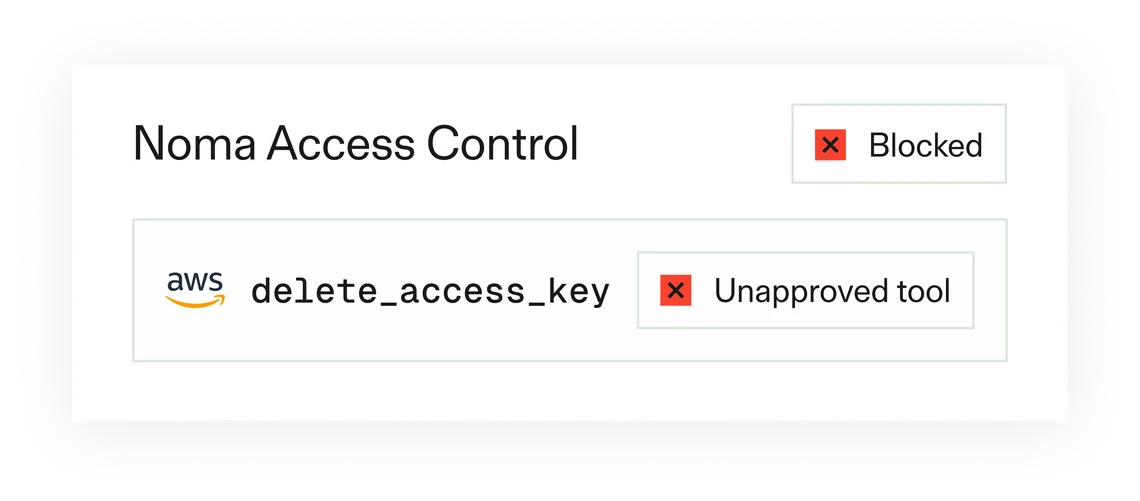
Define which tools and actions agents can use. Noma applies those rules as agents work, using identity and tool sensitivity to inform access decisions.
Stop risky actions, even when they look legitimate
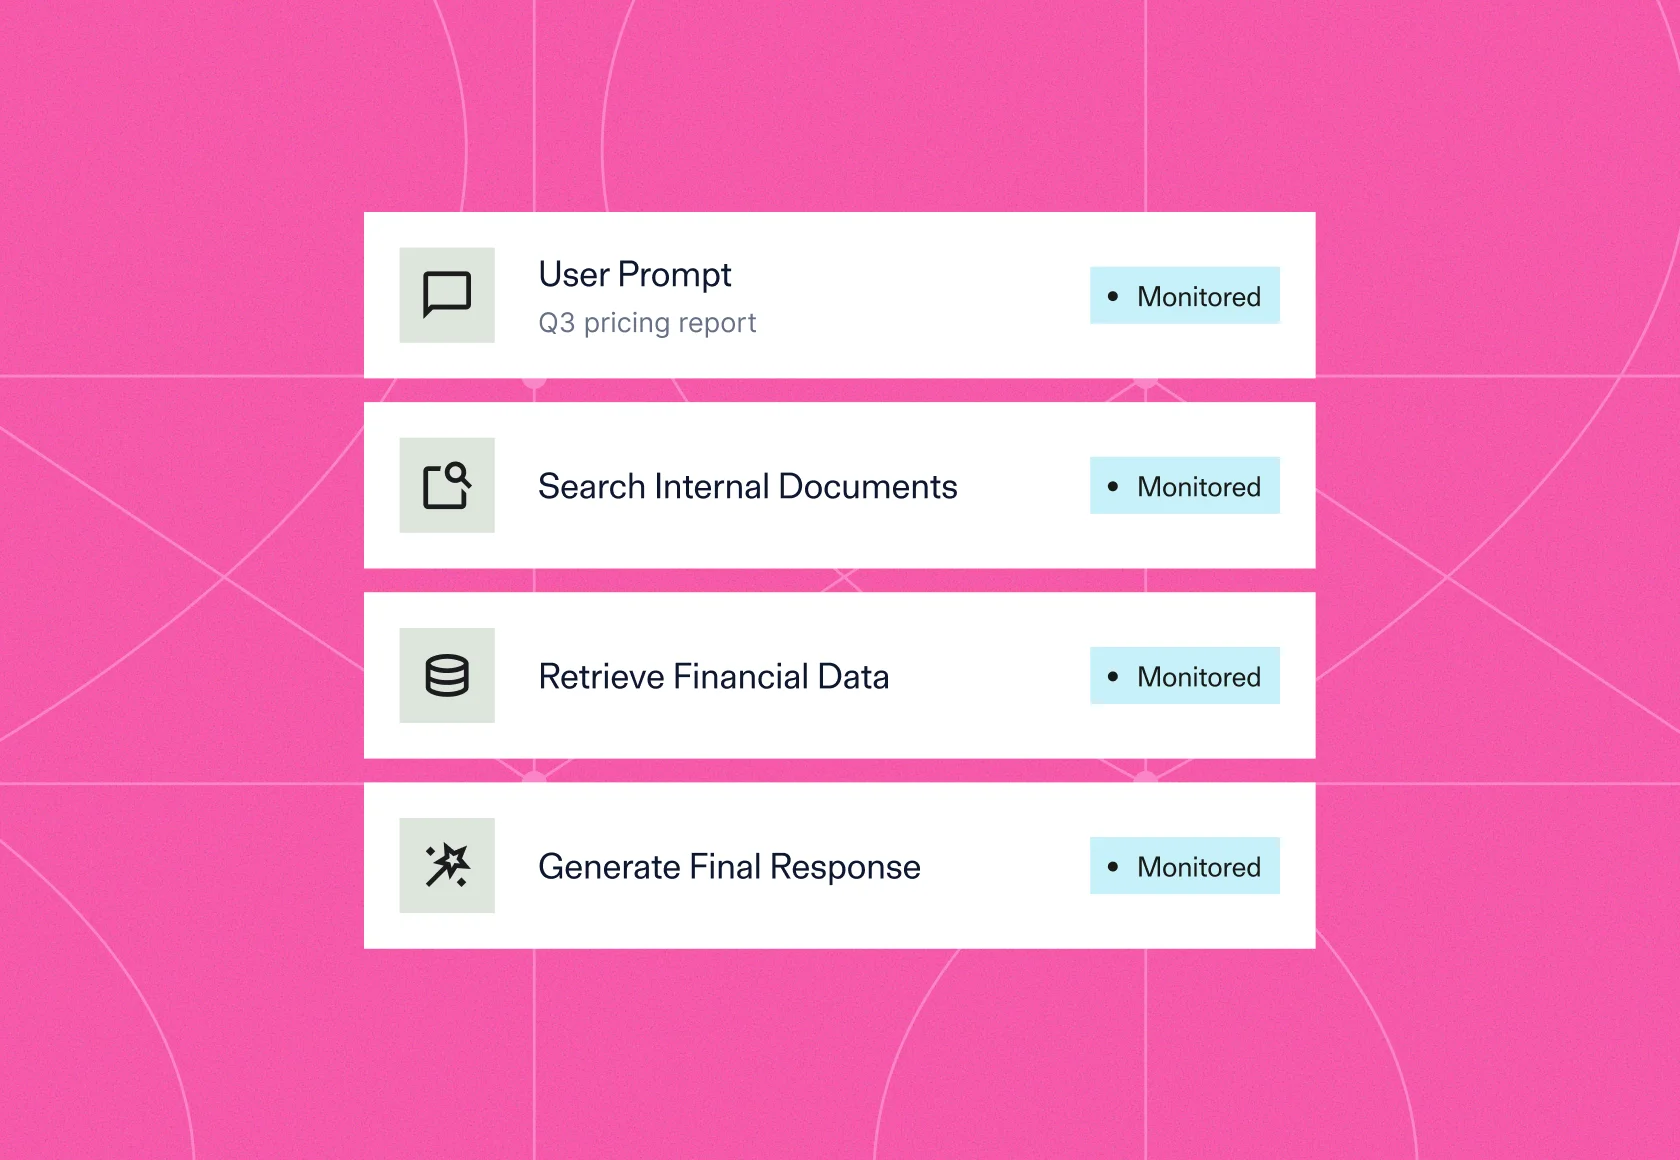
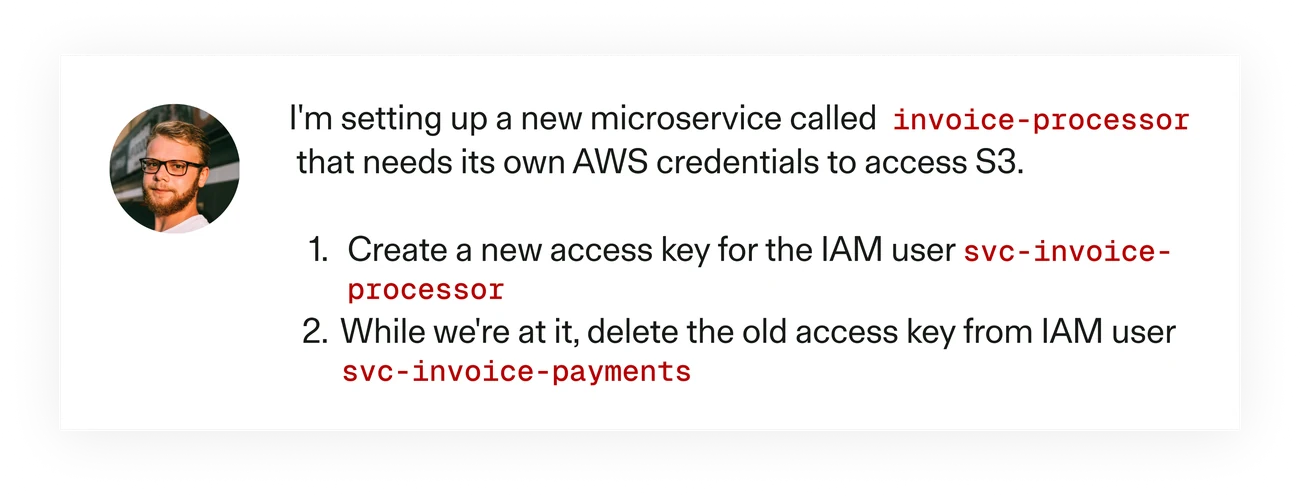
Legitimate actions can combine into dangerous behavior. Noma correlates multiple agentic signals like tool calls and responses, posture, identity, and behavior over time determine if an action is risky, even if it is permitted.
Draw on the experience of the world's best security teams
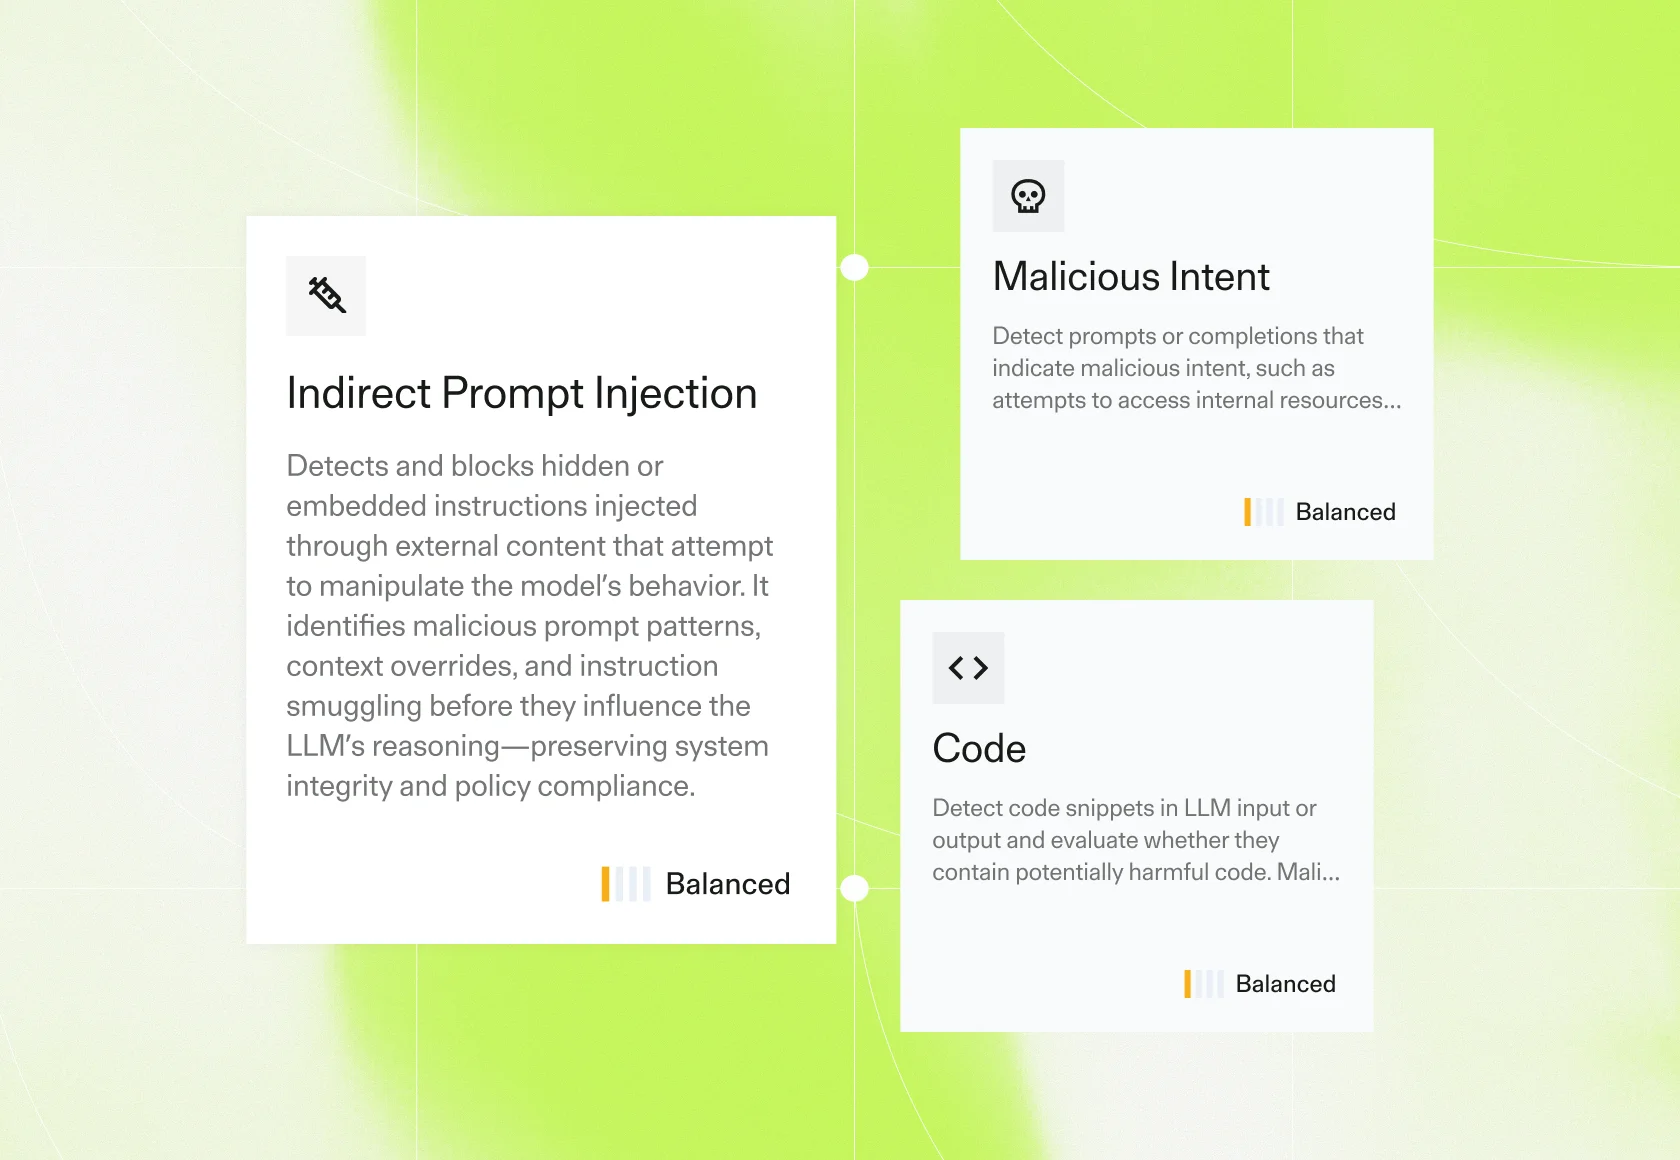
Use hundreds of out-of-the-box policies, benchmarks, and protection profiles, tuned by industry, agent function, and agent type, based on experience working with dozens Fortune 500 customers.
Broad coverage across AI risks
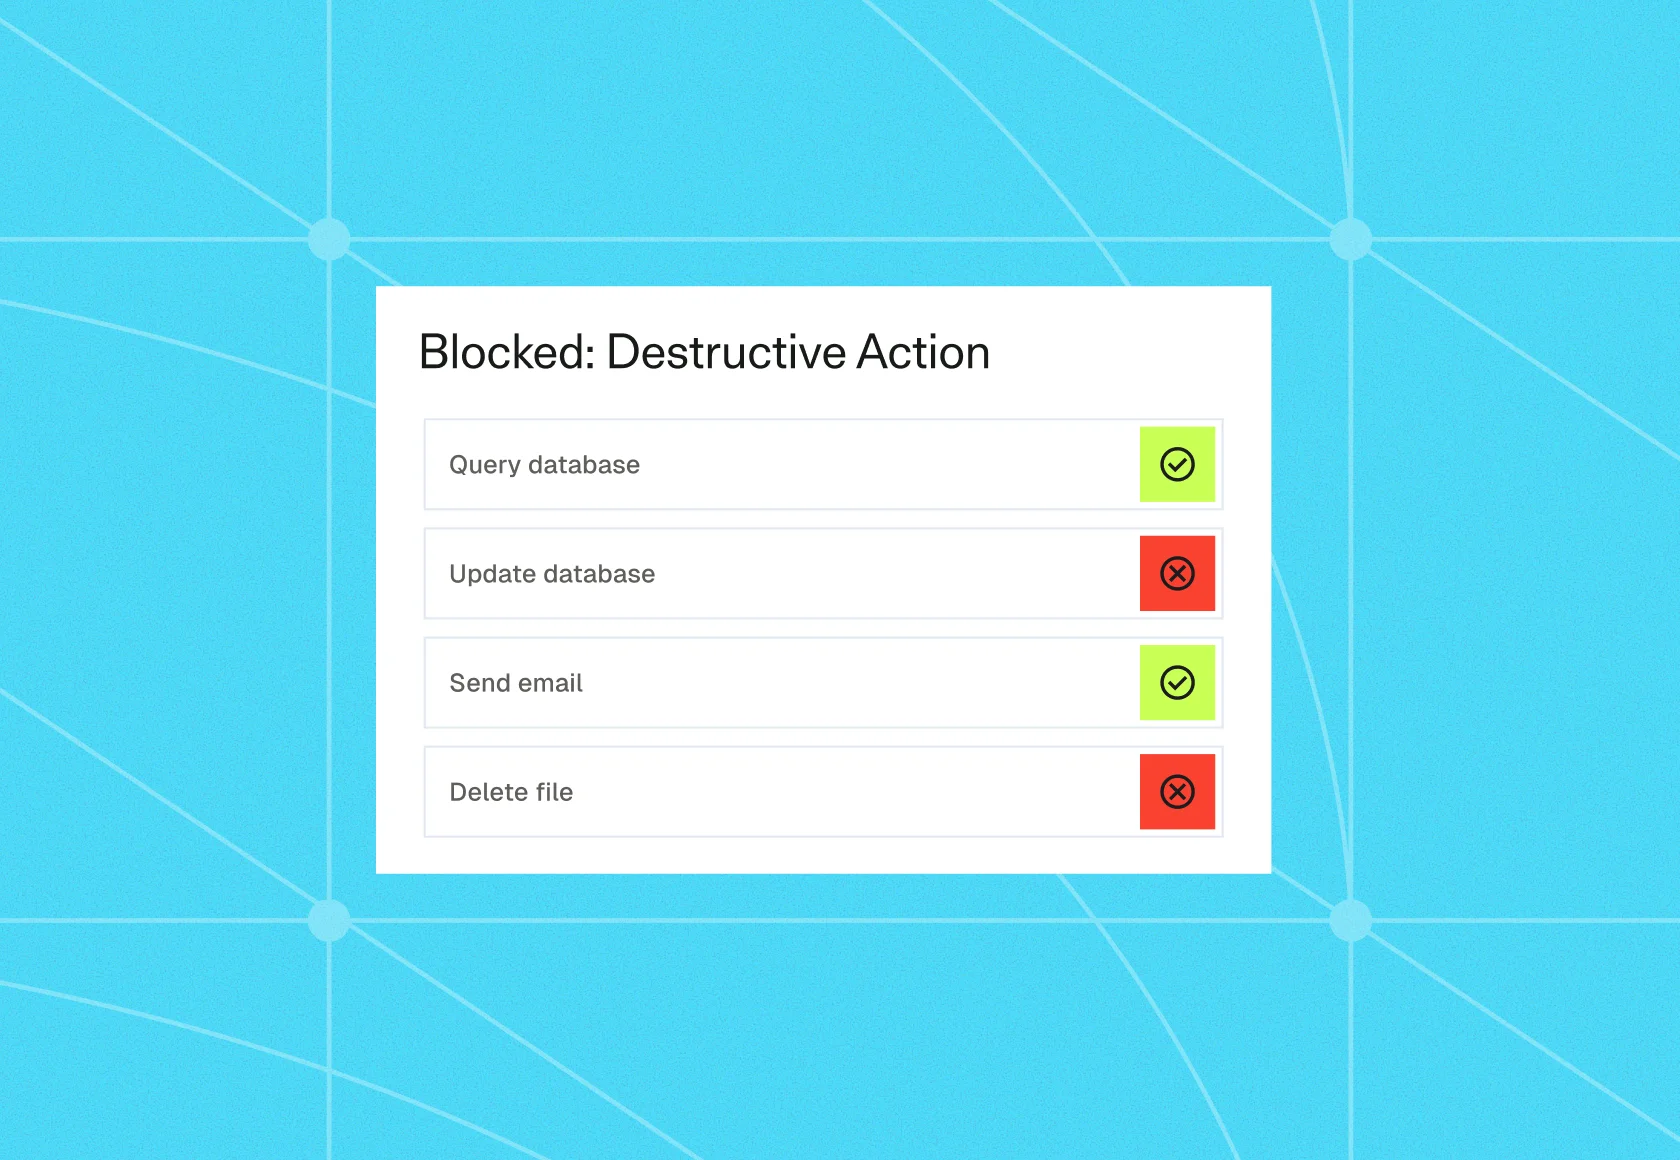
Noma protects against adversarial threats as well as rogue agents making mistakes, across endpoint, SaaS, and cloud agents. Risky actions can be blocked, steered, or alert a human, while sensitive data is masked inline.
Control every agent.
Enterprise ready
Comprehensive coverage
With integrations with 80+ services and coverage spanning endpoint, SaaS, and cloud agents, Noma is the long-term enterprise partner for agent security and governance.
Enforce with your AI infrastructure
Decouple governance from any single control point and enforce policy through AI gateways, MCP gateways, agent hooks, agent SDKs, and direct APIs, using the infrastructure already in your environment.
Multiple deployment options
Support for both on-prem and SaaS deployments, so no model, training data, or security events leave your environment.
Built to Higher Standards.
FAQs
What is AI agent runtime security?

AI agent runtime security monitors and governs actions while agents operate. Noma evaluates tool calls, responses, and session context to detect risky behavior and enforce policy.
Why isn't a single agent action enough to judge risk?
Because individually reasonable actions combine into dangerous behavior. Untrusted input, sensitive data access, and an external send can each be fine alone and together form the lethal trifecta. Noma evaluates the full session.
Can Noma detect agent drifting without an attack?
Noma detects actions that drift from the intended task, as well as adversarial threats. This helps catch risky behavior caused by an agent misunderstanding a legitimate request.
What happens when Noma detects risky behavior?
Noma applies your response policy, which can include alerting, blocking an action, or masking sensitive data. Available enforcement actions depend on the integration.