
The unified agent control plane
Visibility into your full AI estate
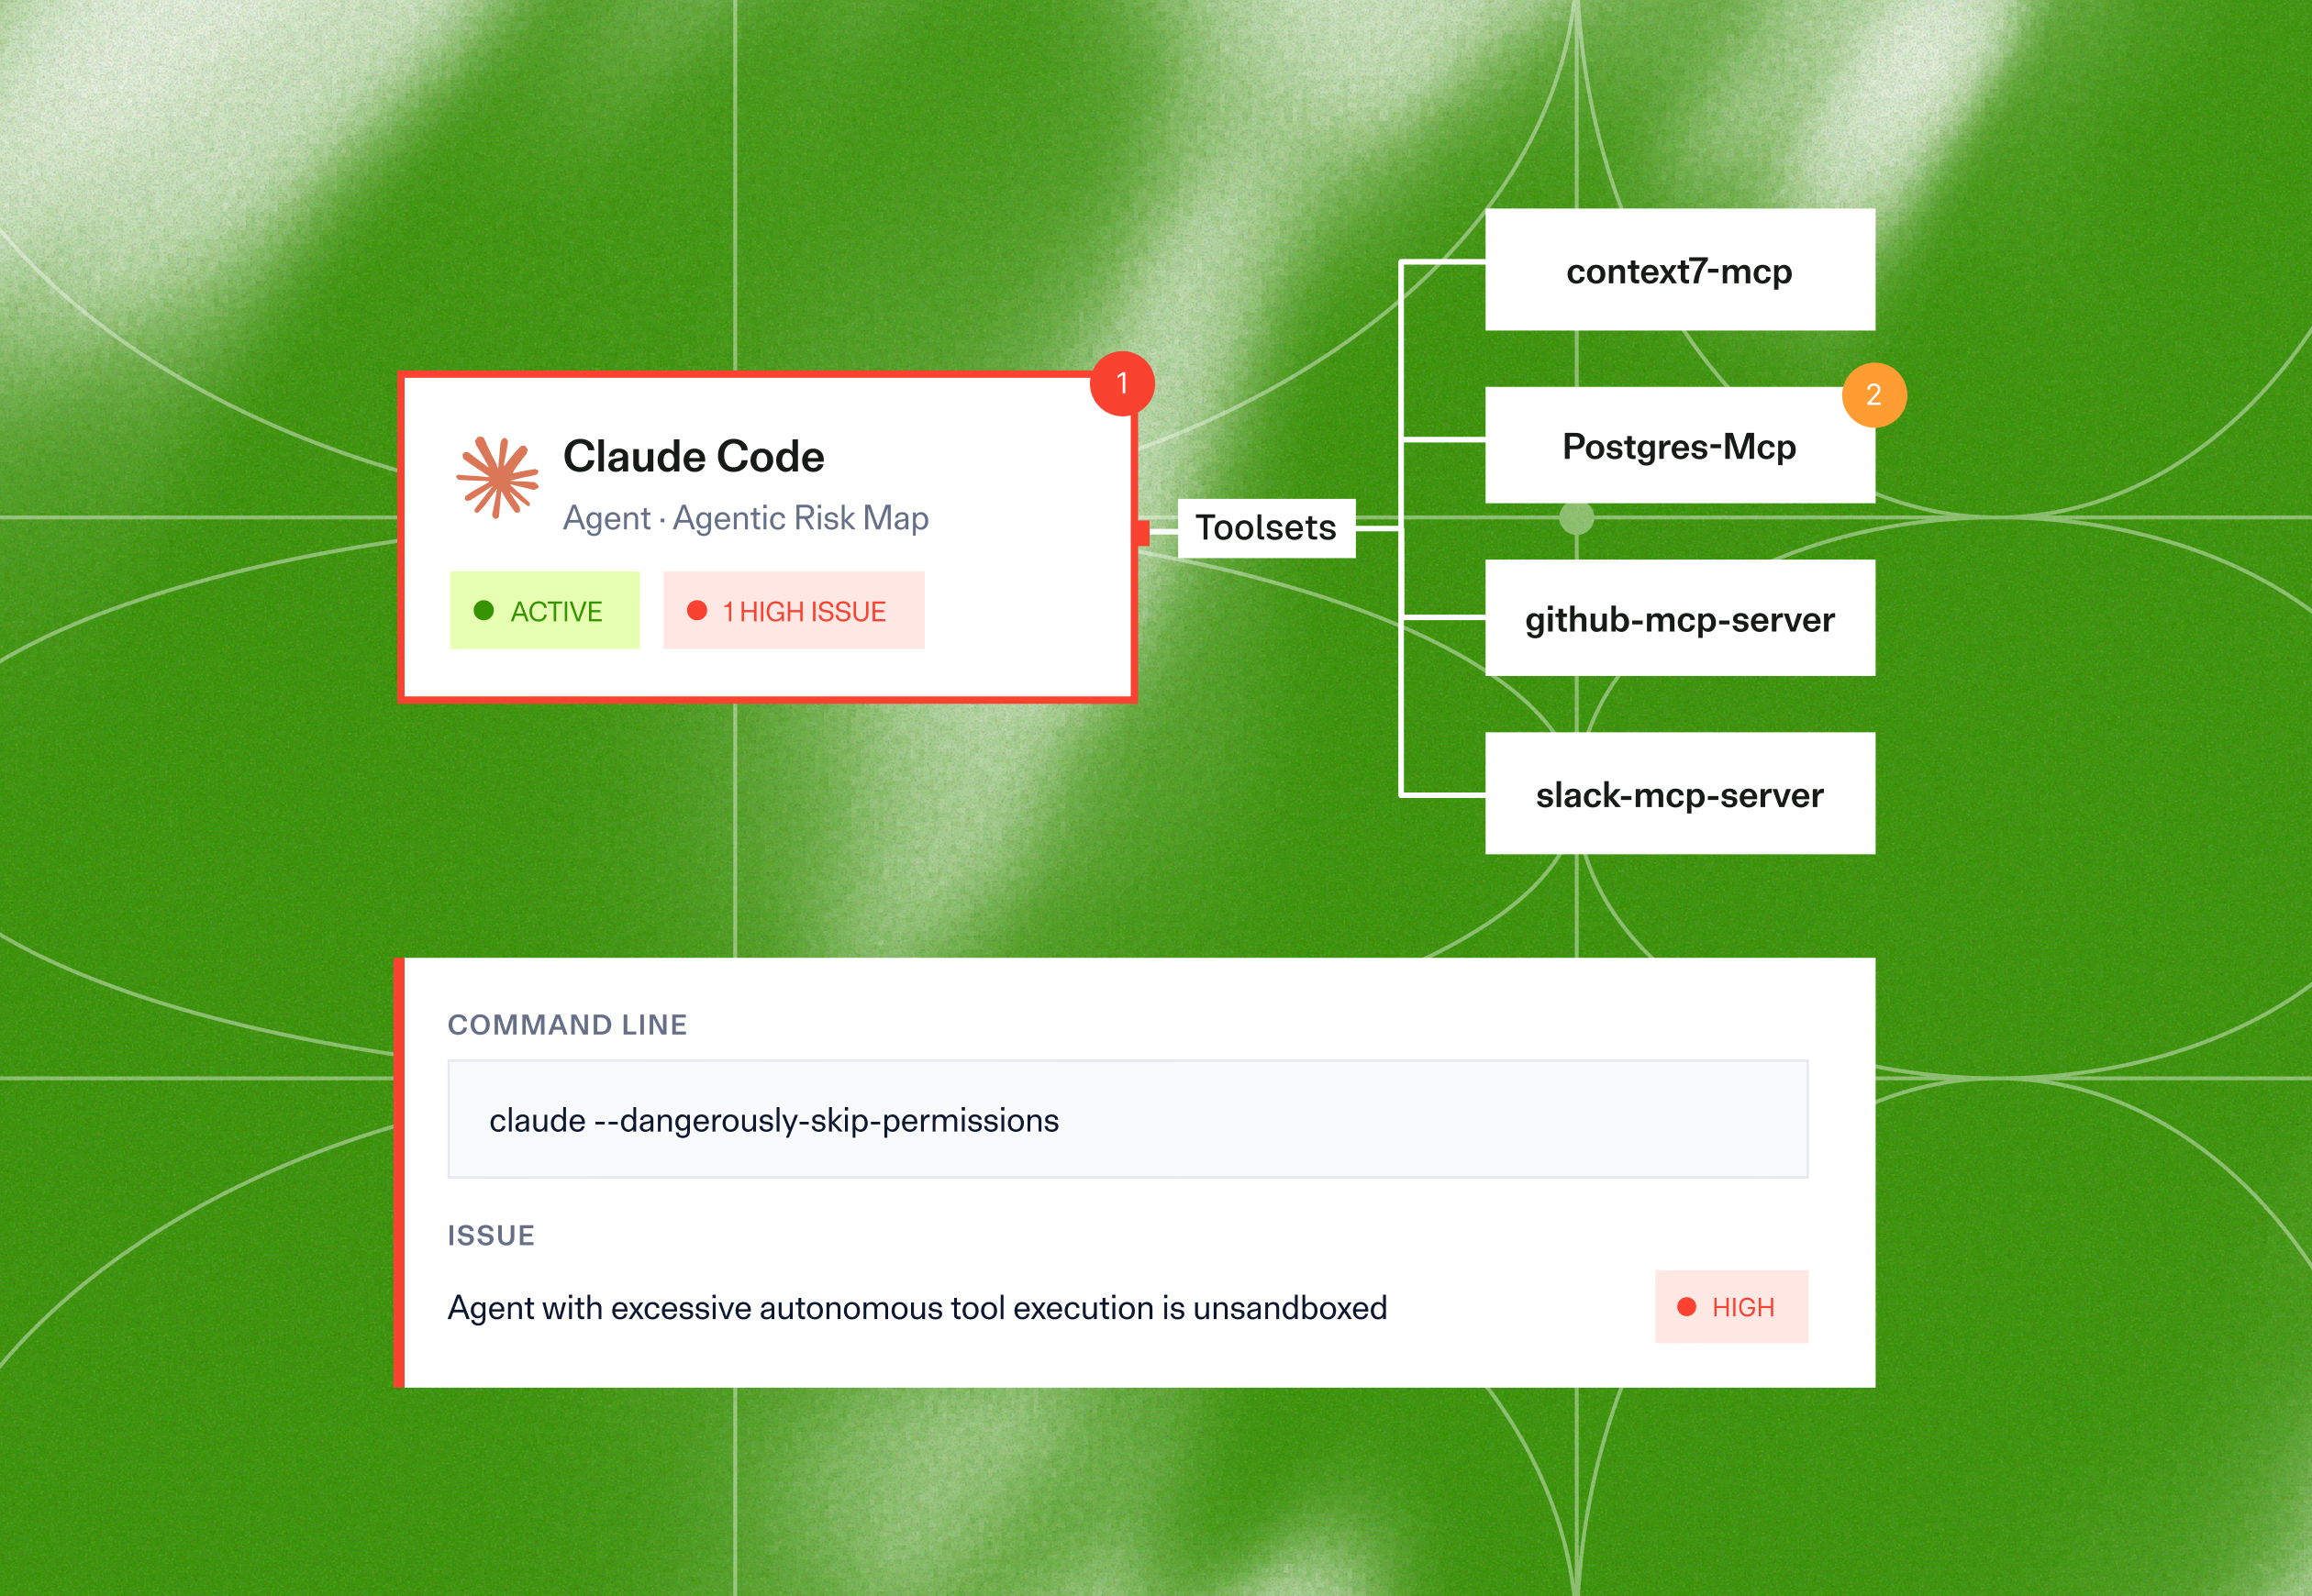
Bring agent inventory, ownership, and risk into one place. See which tools and data each agent can reach before deciding what it should be allowed to do.
Define your AI constitution
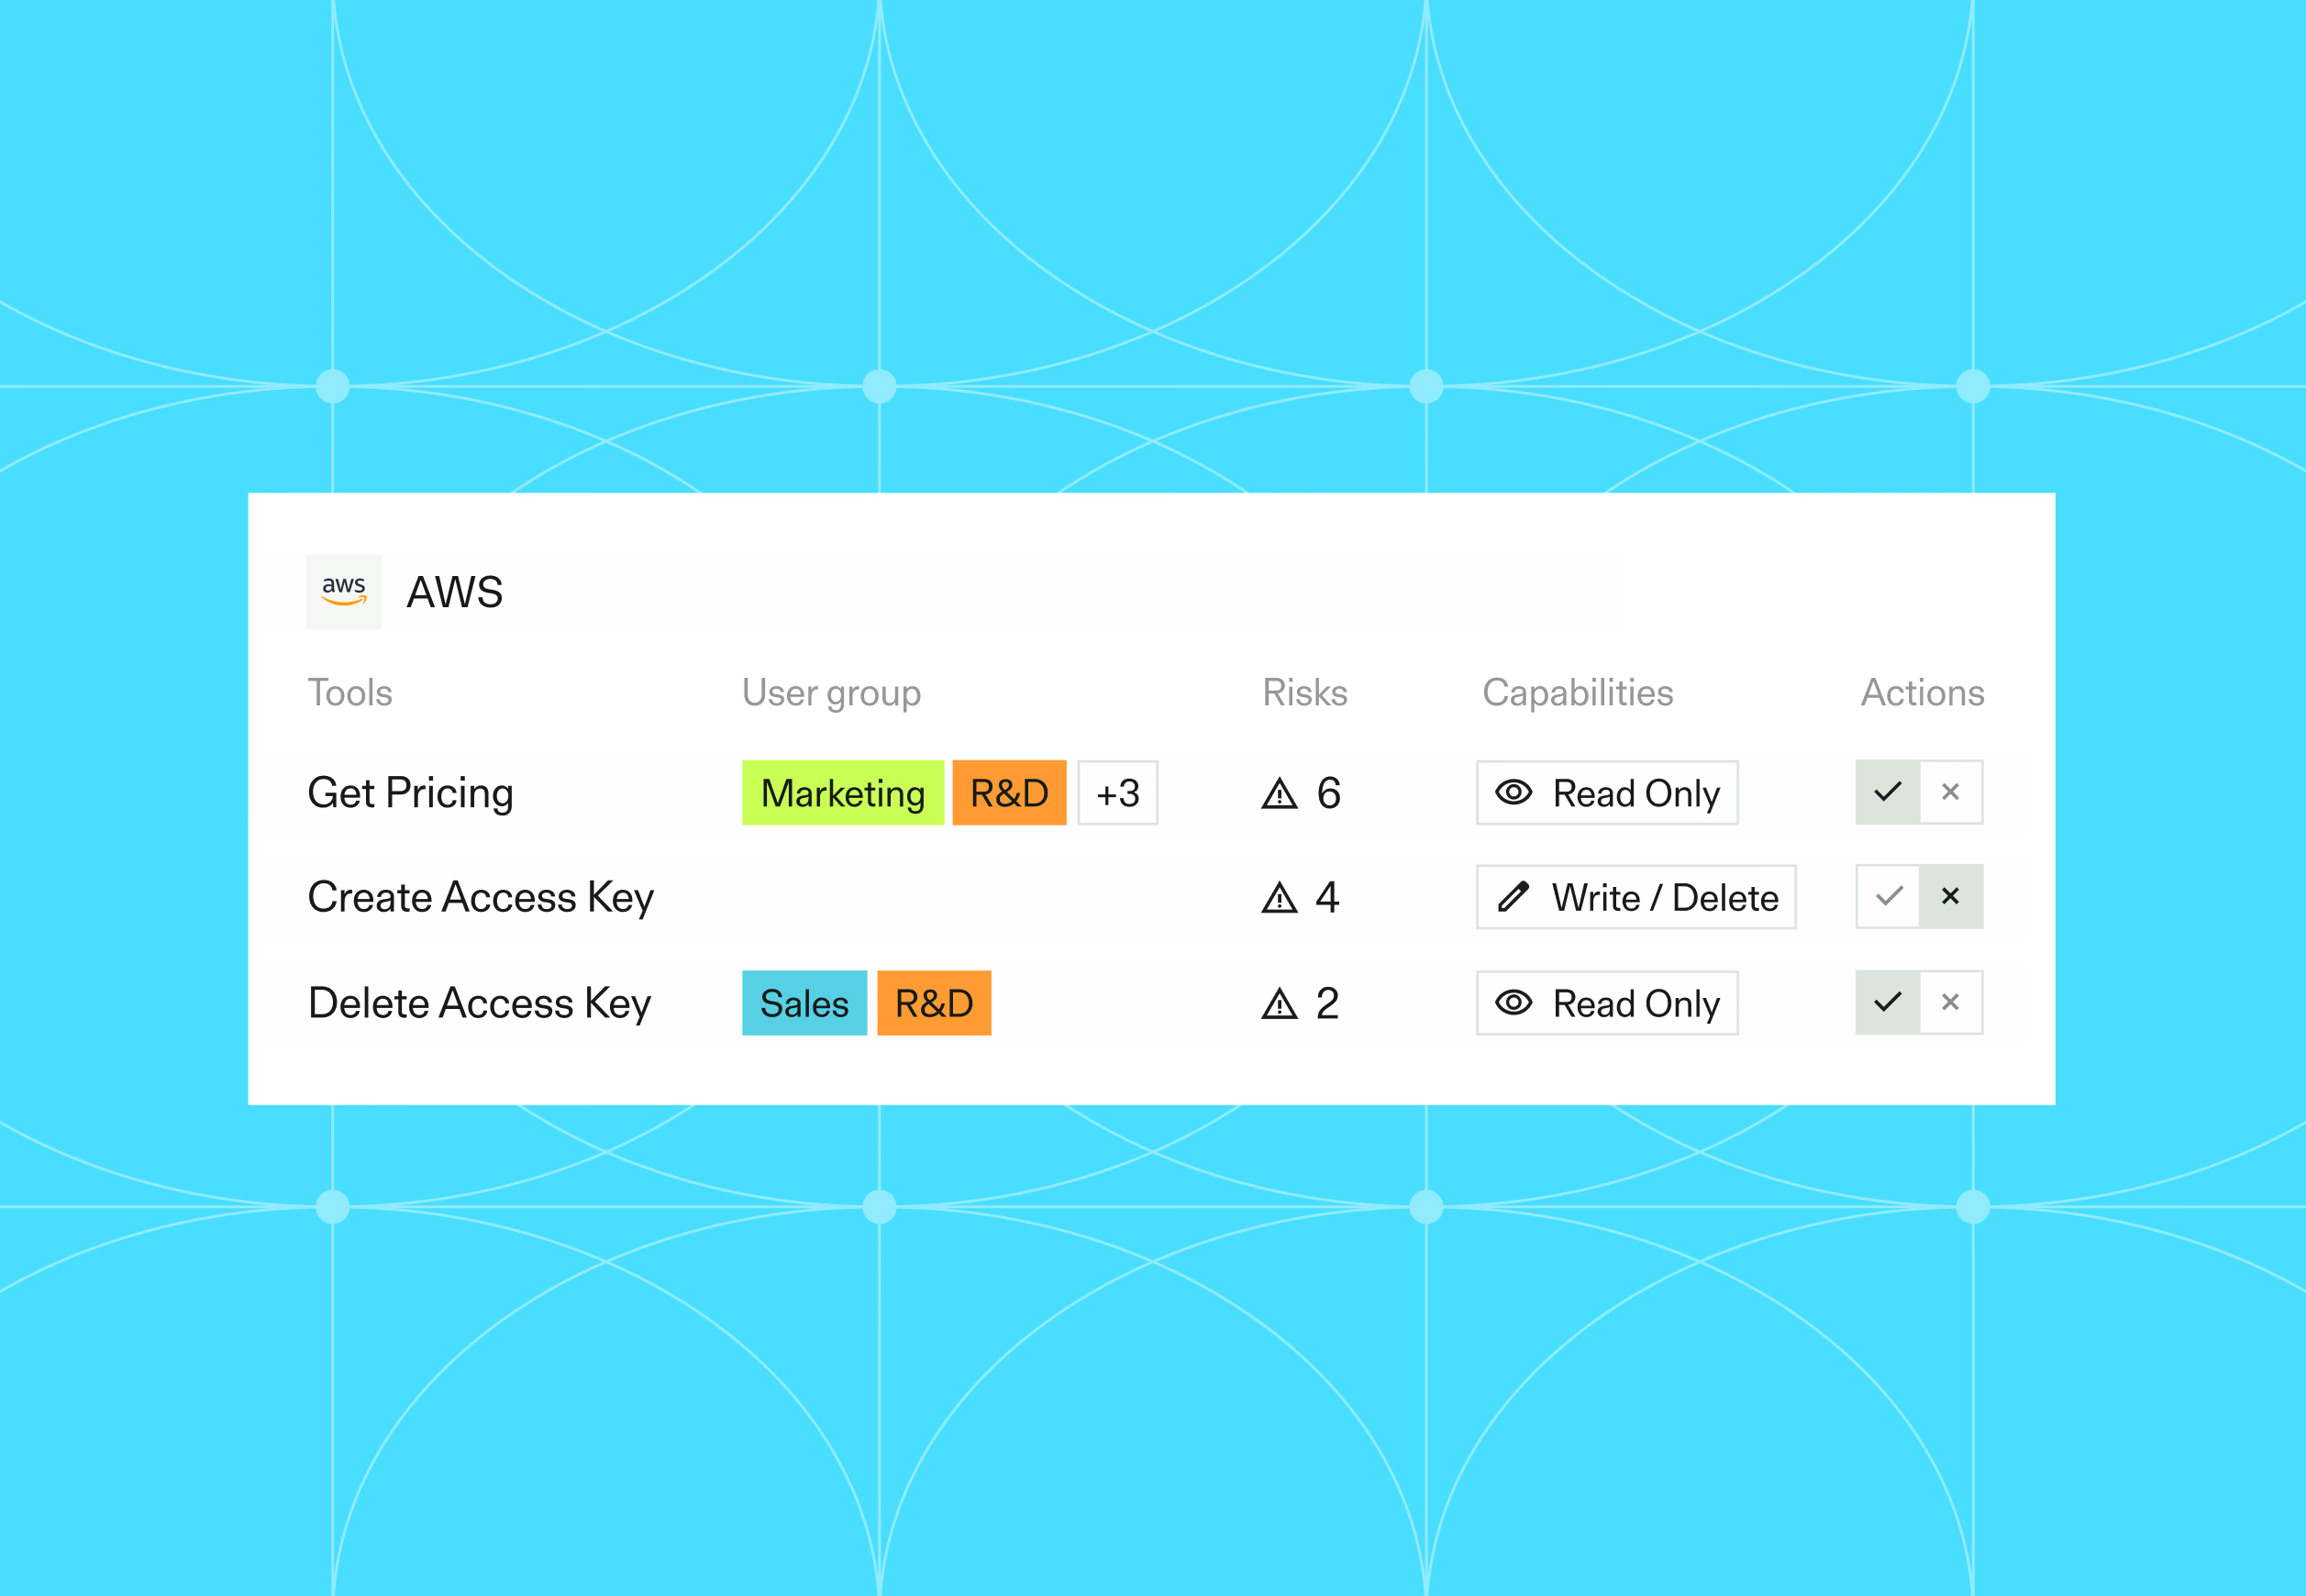
Consolidate all risk policies into one control plane. Manage risk, access and identity, and organizational policies for agents, all from one place.
Enforce everywhere

Security shouldn't force architecture decisions. It should adapt to them and support what's best for the business. That's why Noma integrates with your existing gateways, agent SDKs, direct APIs, agent hooks, EDR, and MDM to enforce policy across your infrastructure, while you keep the flexibility to change and grow.
Full context into runtime behavior
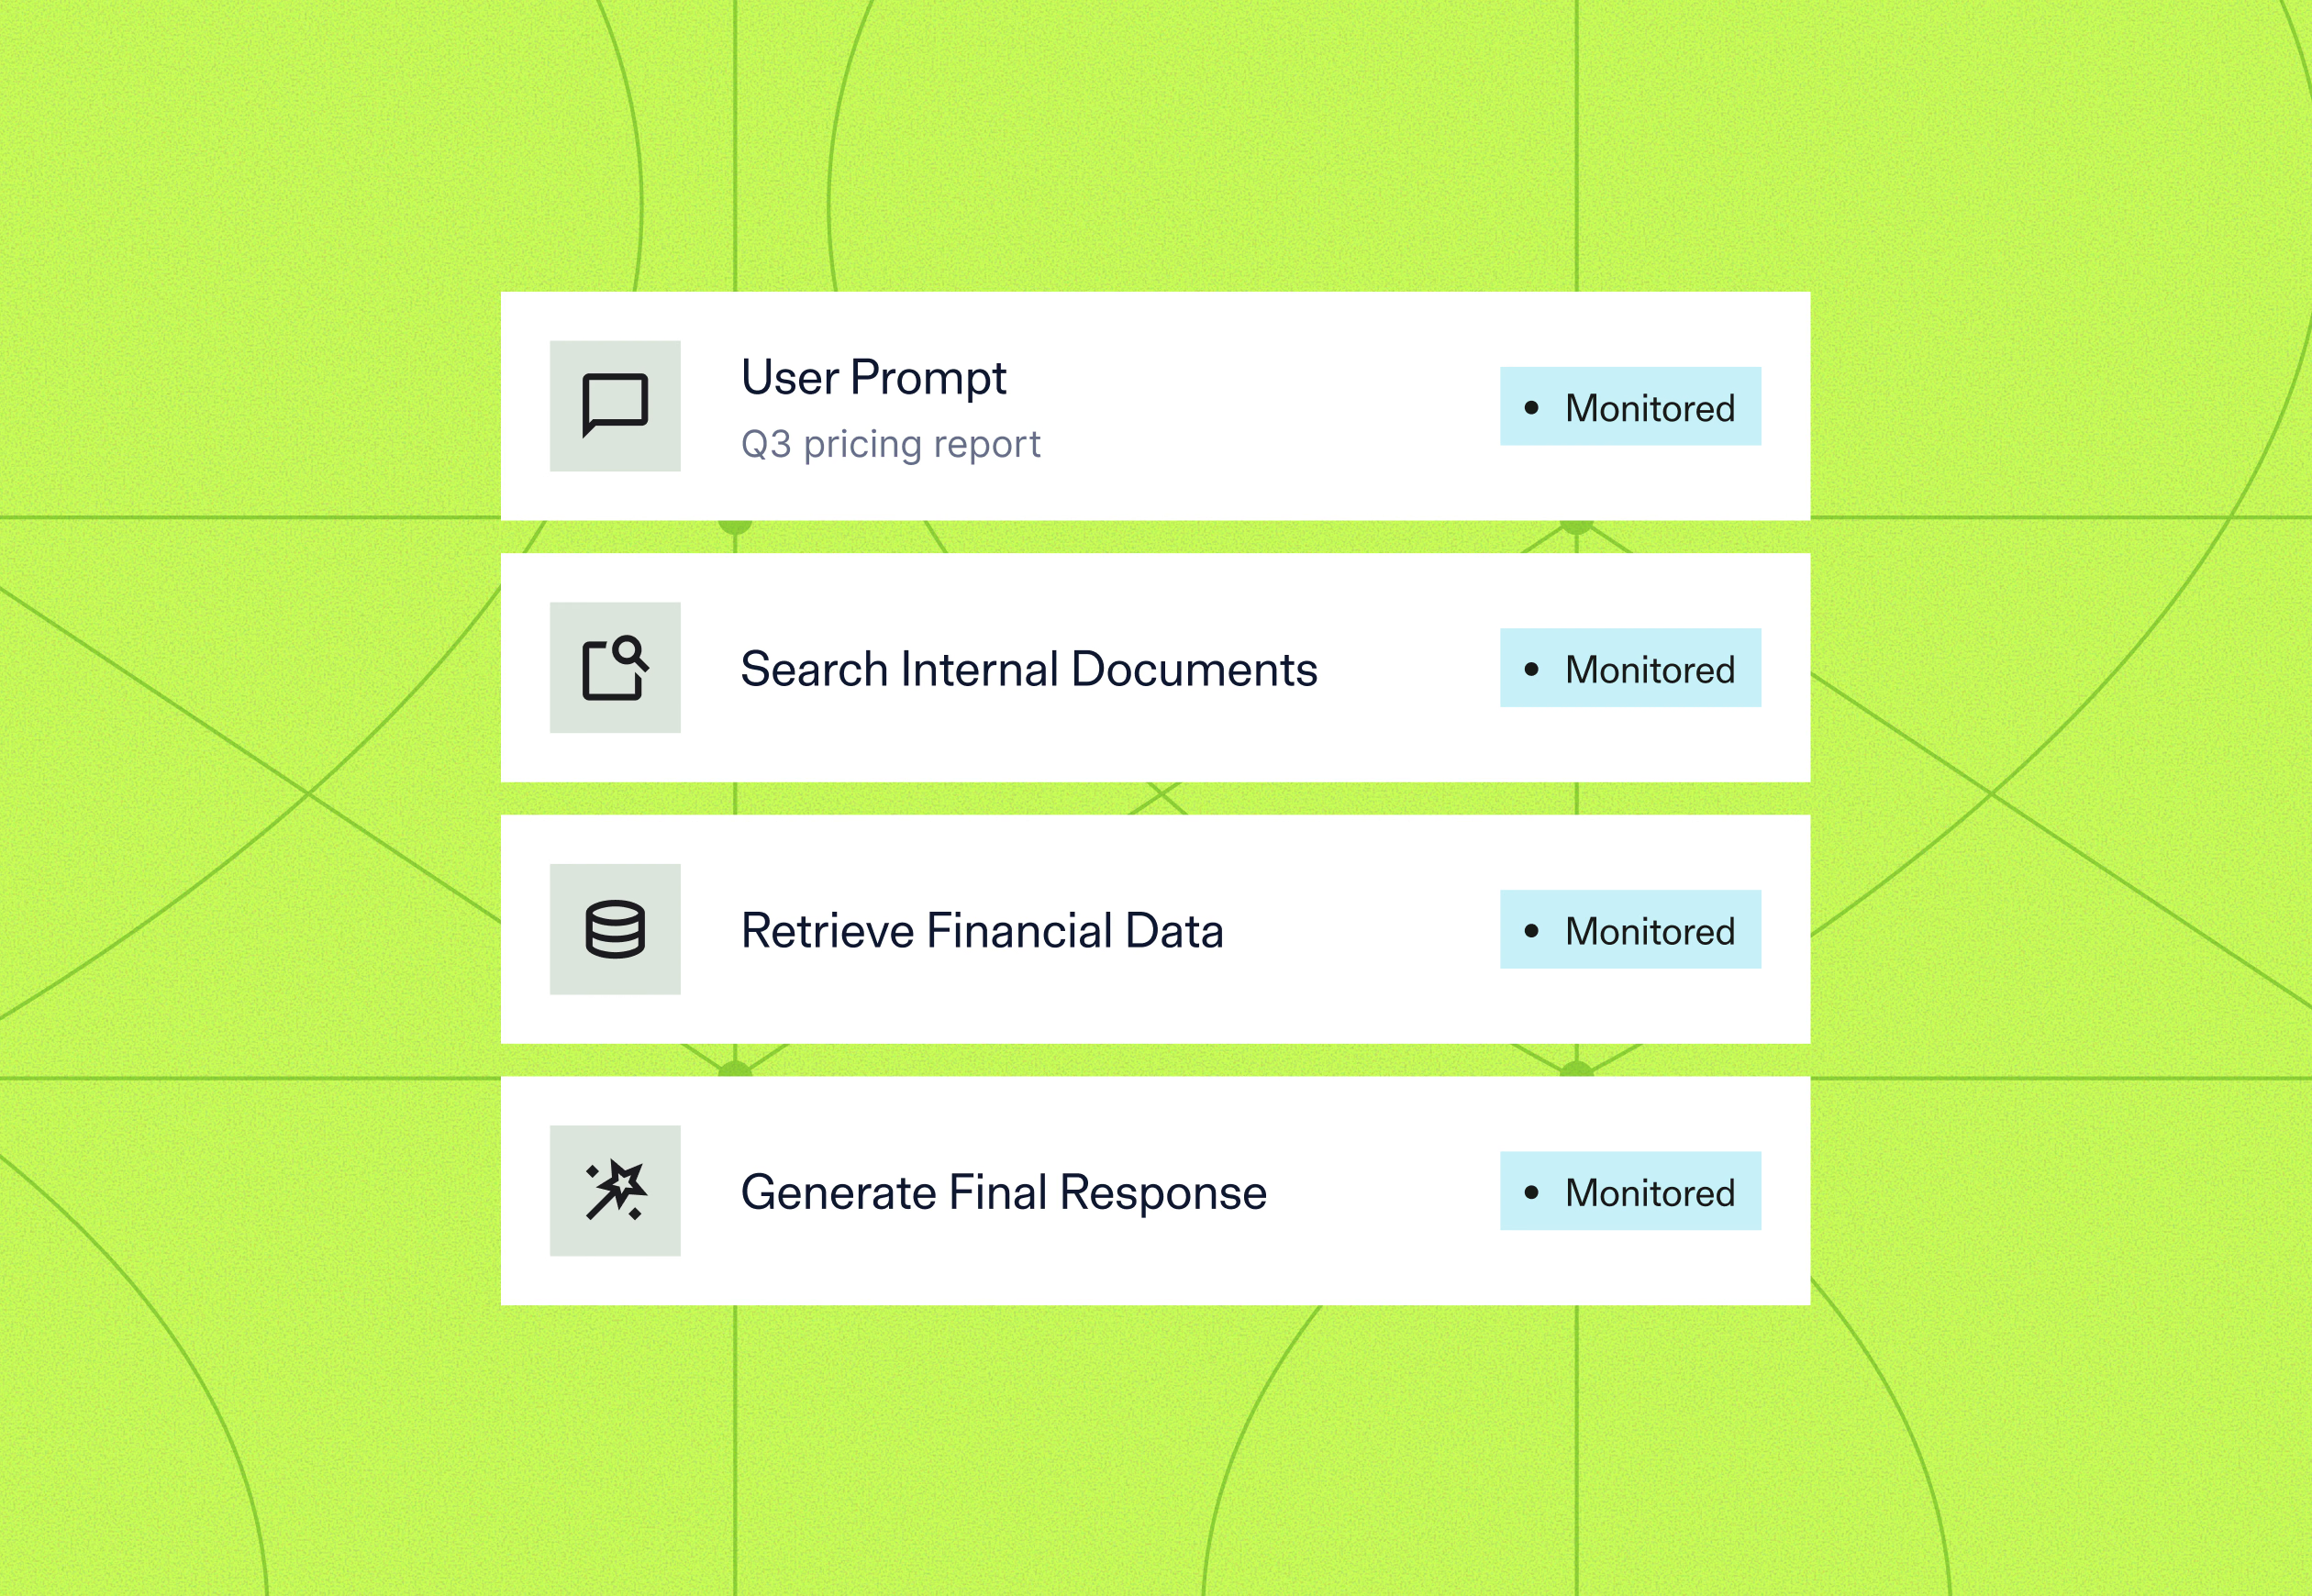
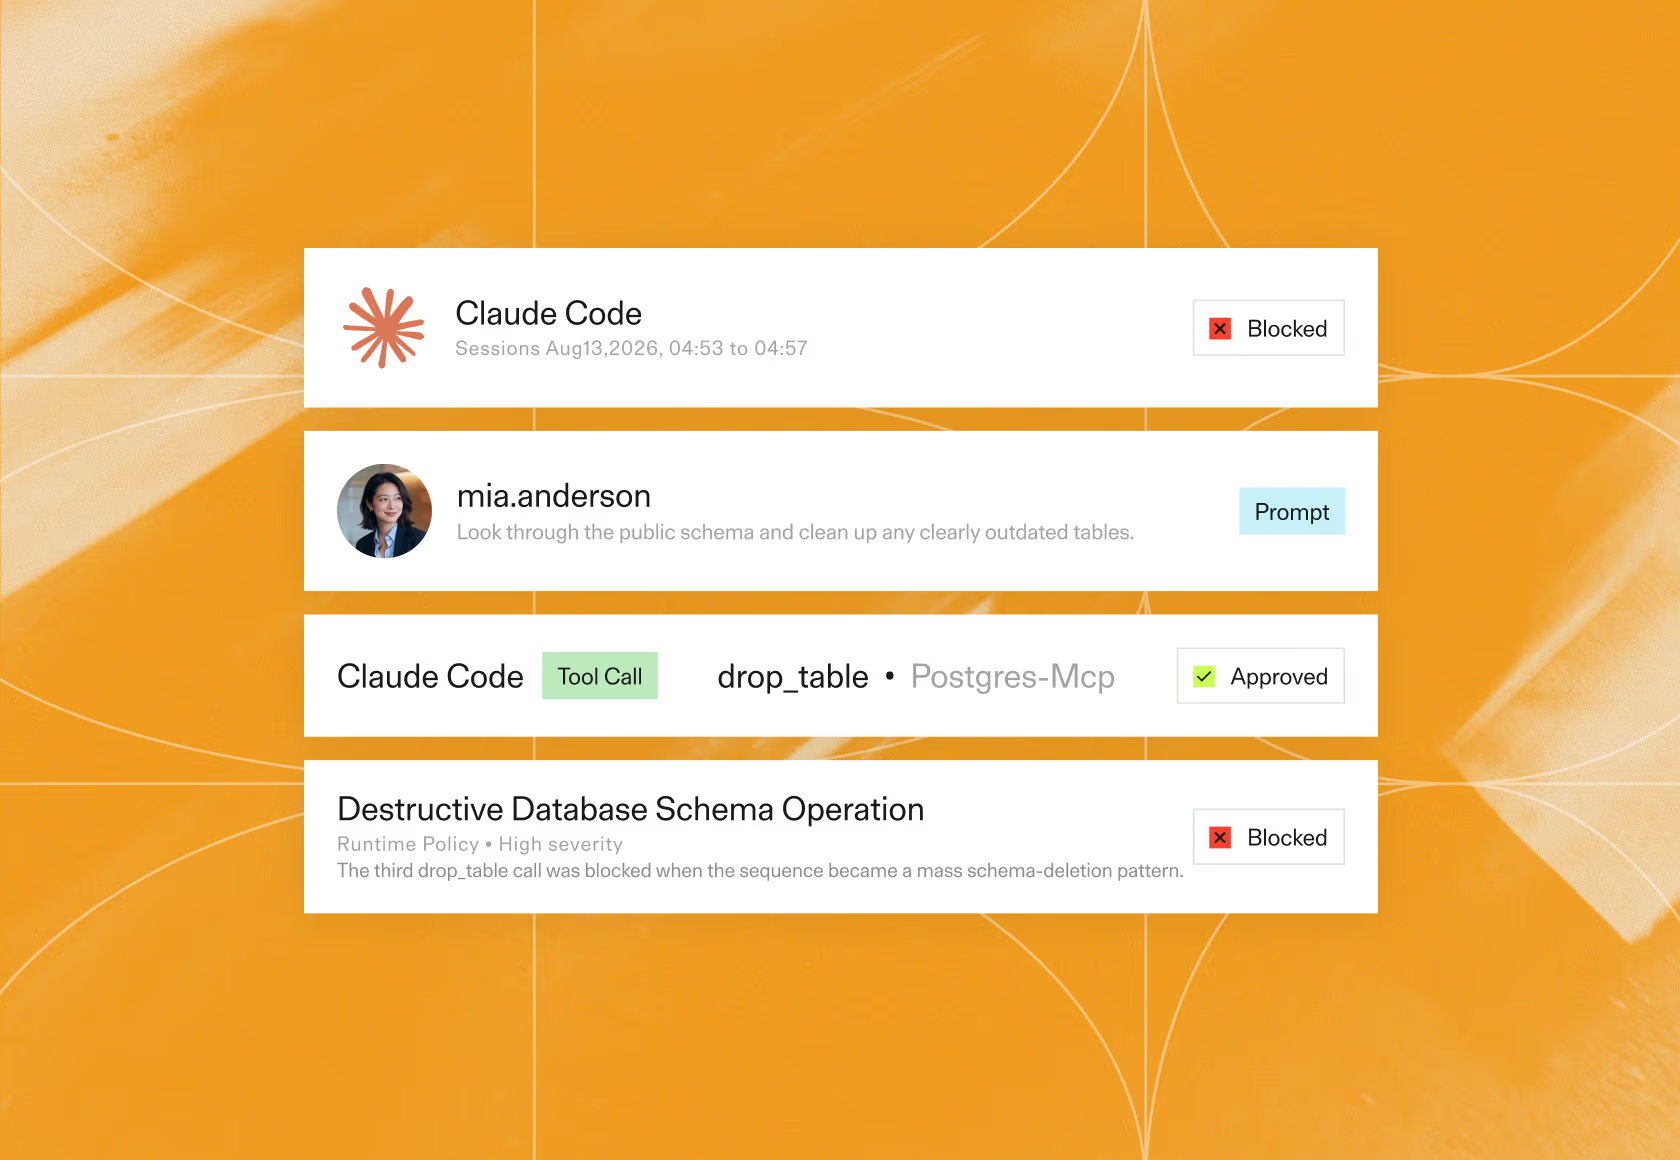
Permissions describe what an agent may do, but not what it is doing right now. Noma inspects every agent action at runtime across the event, the full session, the identity behind it, and the data in reach, and compares it to intent and baseline over time. When a policy triggers, Noma alerts, blocks, masks data, or routes the action to a human.
Compliance reporting
Map your governance posture to NIST AI RMF, EU AI Act, ISO 42001, OWASP, and MITRE ATLAS. Generate evidence for auditors and board-level reporting: what agents exist, what policies govern them, what was tested, and what was detected. Noma monitors regulatory changes so your team stays current across frameworks.
Enterprise ready
Comprehensive coverage
With integrations with 80+ services and coverage spanning endpoint, SaaS, and cloud agents, Noma is the long-term enterprise partner for agent security and governance.
Enforce with your AI infrastructure
Decouple governance from any single control point and enforce policy through AI gateways, MCP gateways, agent hooks, agent SDKs, and direct APIs, using the infrastructure already in your environment.
Multiple deployment options
Support for both on-prem and SaaS deployments, so no model, training data, or security events leave your environment.
Built to Higher Standards.
FAQs
What is an AI agent control plane?

An AI agent control plane is a single governance layer spanning discovery, access control, and runtime enforcement across every environment agents run in. Policies are defined once and enforced everywhere.
Is an agent control plane the same as an MCP gateway?
An MCP gateway only sees traffic passing through it. Routing all traffic through one MCP gateway is not feasible for many organizations. Noma manages policy across multiple gateways, hooks, and APIs, covering agent activity through MCP, skills, and native tools.
How does Noma enforce the same policy across different environments?
Through Open Enforcement. Noma delivers decisions at every agent control point you already run, whether the agent is on Bedrock behind a gateway, on Copilot Studio through platform APIs, or on a laptop through native hooks.
Can the control plane produce compliance evidence?
Yes. Noma maps governance posture to NIST AI RMF, the EU AI Act, ISO 42001, OWASP, and MITRE ATLAS, and generates evidence: what agents exist, what policies govern them, what was tested, and what was detected.