Securing agent identity and access with Noma
See every agent, MCP, and skill

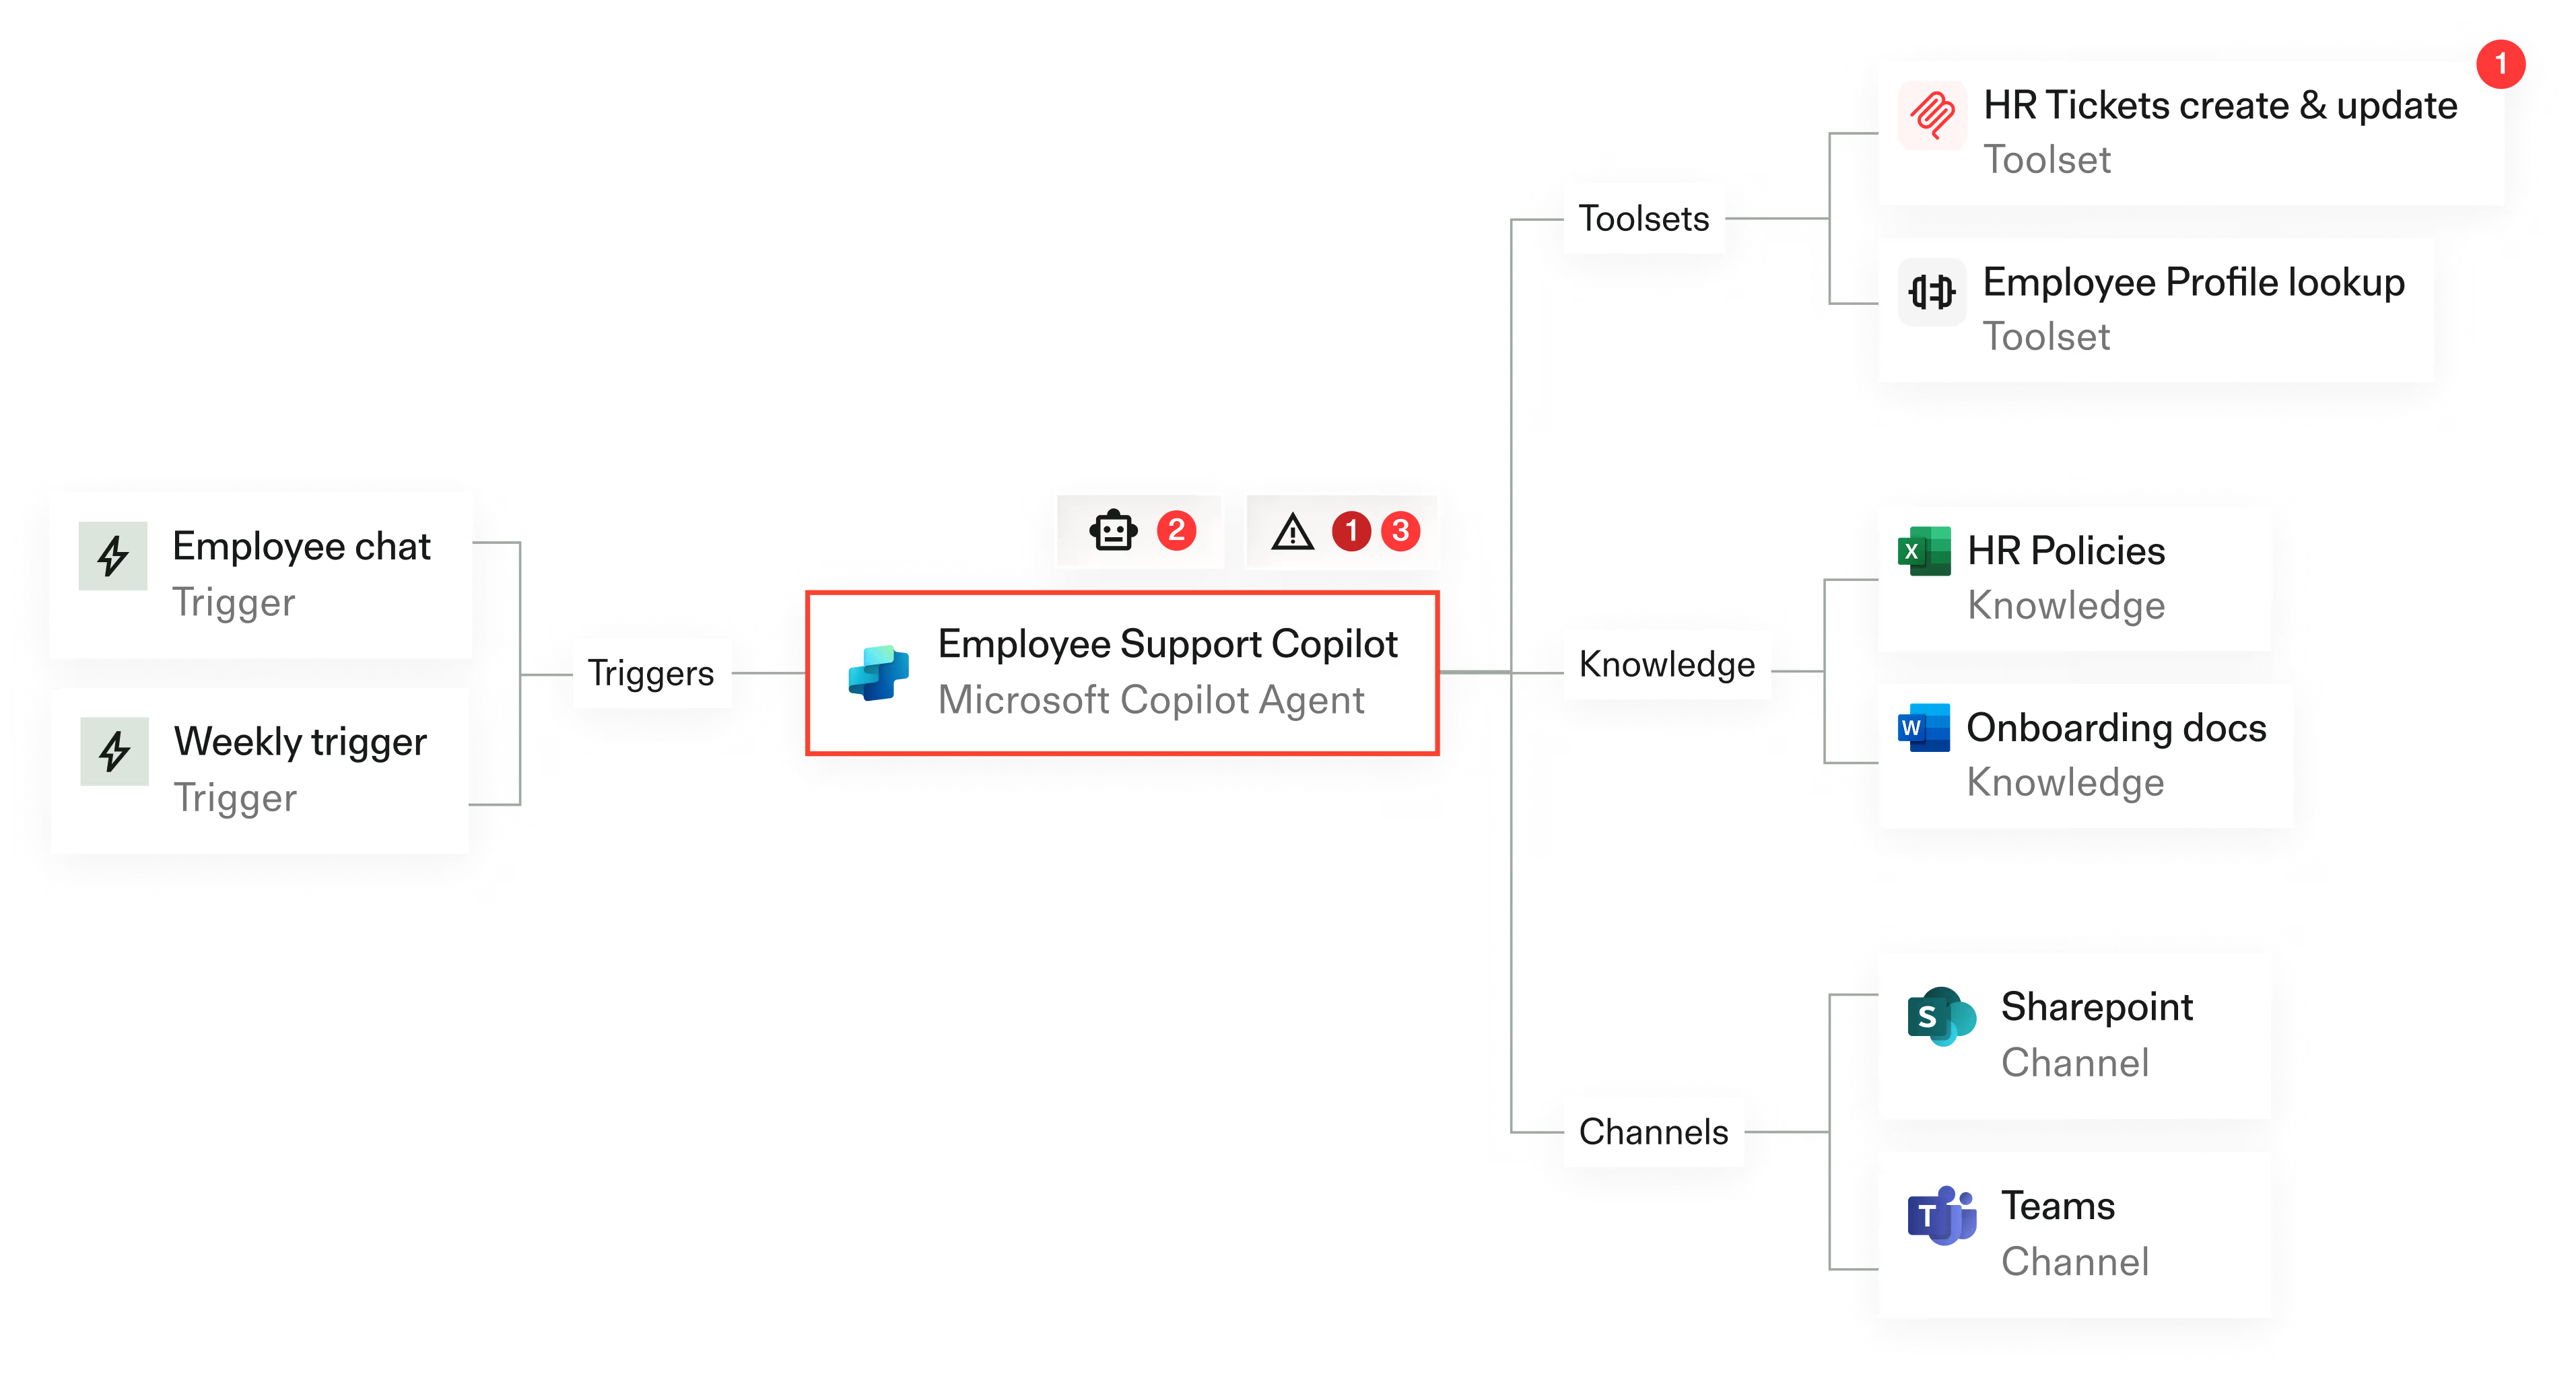
Discover agents, MCP servers, and skills across your organization. Use that inventory to build a registry of approved components, including agents employees introduced without a security review.
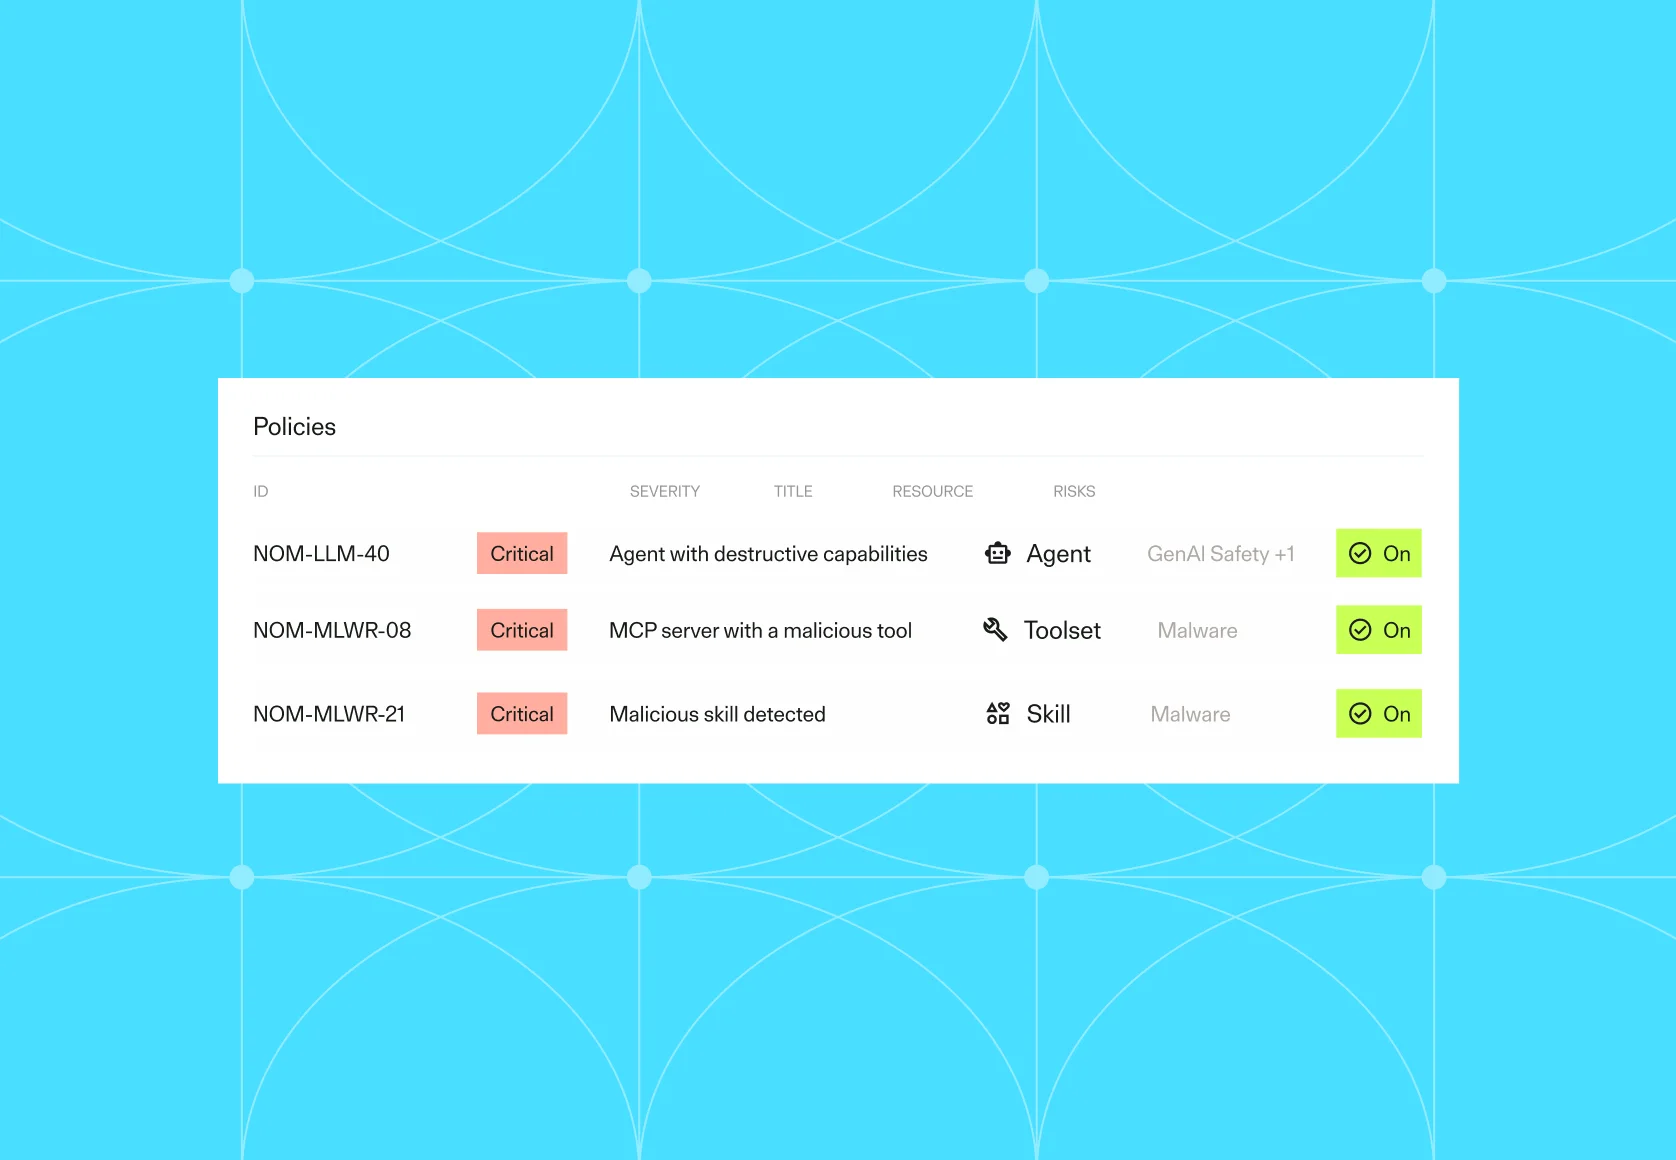
Enforce policies based on tools or users
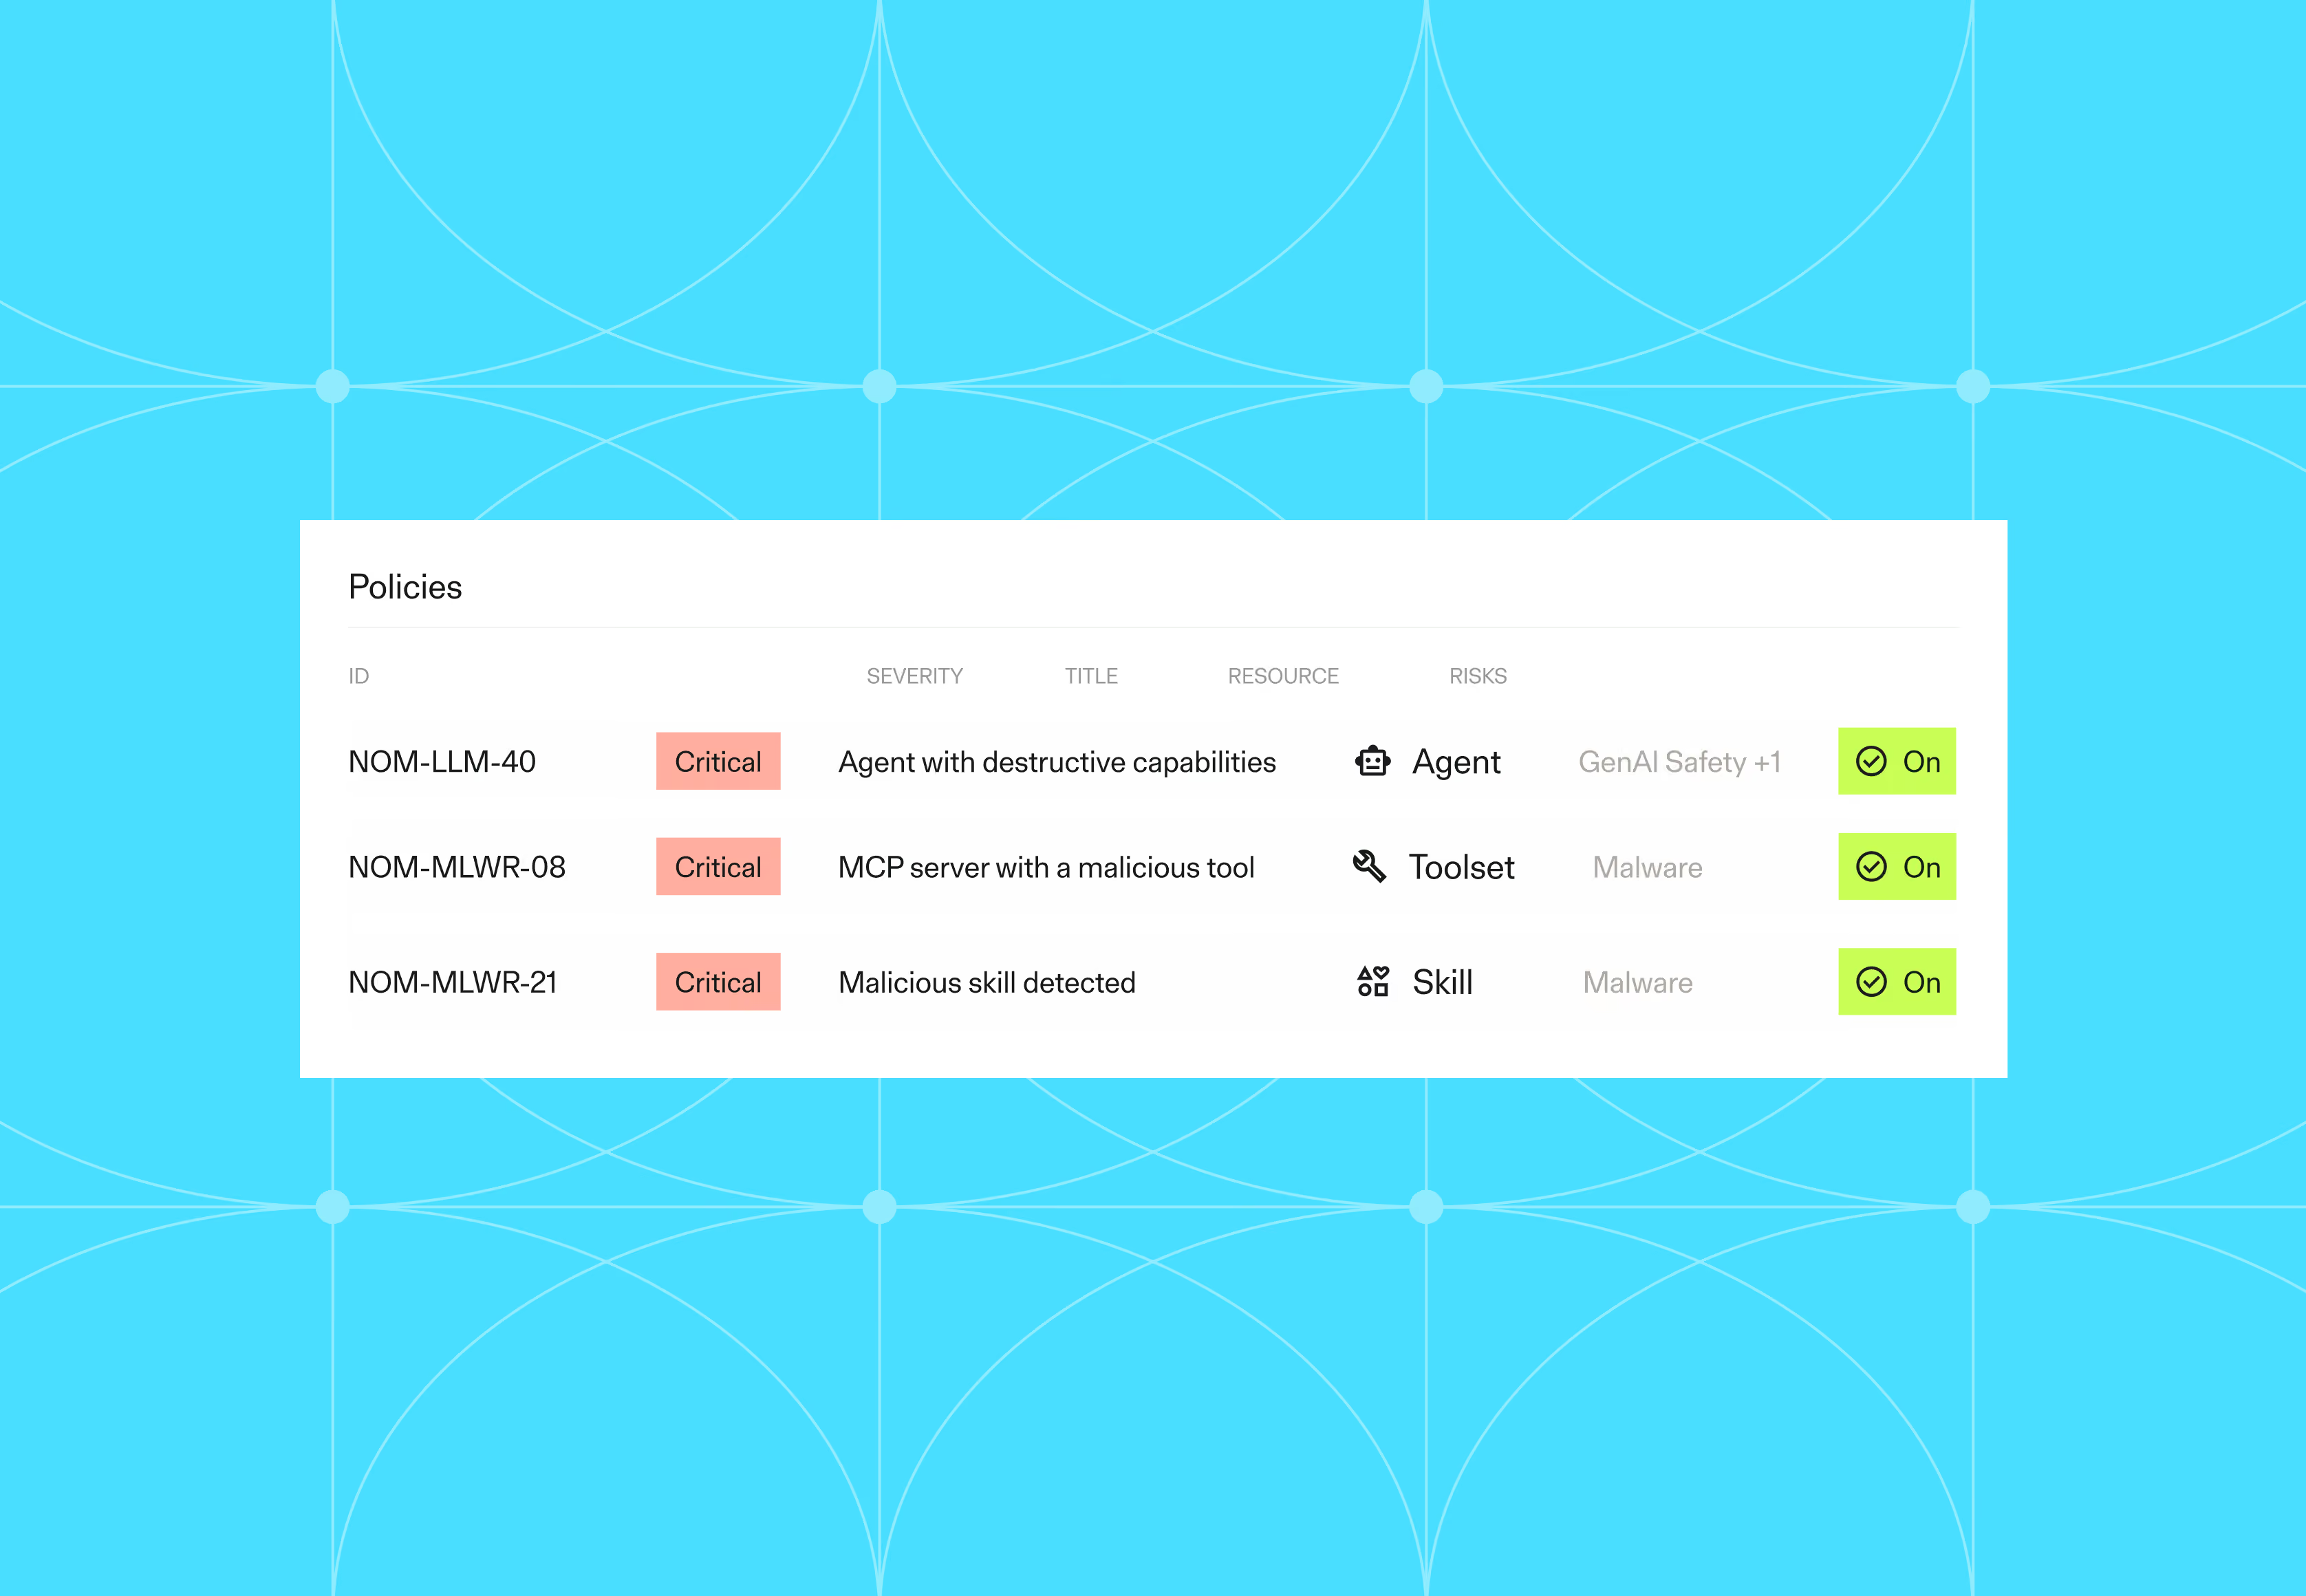
Agents owned by different users might need different access to the same tool. Noma uses identity and tool sensitivity to determine which actions an agent is allowed to take with MCPs and skills.
Govern without the architecture tax

Enforce access decisions through your gateways, hooks, and APIs. Keep agent policy centralized while your teams use different tools and platforms.
Watch what agents do with the access

Permission to use a tool does not make every action safe. Noma checks agent activity against the intended task and detects risky behavior during execution.



Enterprise ready
Comprehensive coverage
With integrations with 80+ services and coverage spanning endpoint, SaaS, and cloud agents, Noma is the long-term enterprise partner for agent security and governance.
Enforce with your AI infrastructure
Decouple governance from any single control point and enforce policy through AI gateways, MCP gateways, agent hooks, agent SDKs, and direct APIs, using the infrastructure already in your environment.
Multiple deployment options
Support for both on-prem and SaaS deployments, so no model, training data, or security events leave your environment.
Built to Higher Standards.
FAQs
What is agentic identity?

Agentic identity is treating every AI agent as an identity in the organization: knowing who it acts for, what it's allowed to do, and whether its actions match that intent. Agents are non-deterministic and operate at far greater scale than human or machine identities.
Why can't my IdP manage agent identities?
Most agents never appear in the IdP, and new protocols like XAA are far from enterprise-ready authorization. Noma governs agent access today, keyed to the IdP groups you already maintain.
How does Noma enforce agent identity policies?
Noma enforces at every existing agent control point: gateways, agent hooks, agent SDKs, direct APIs, and EDR or MDM integrations. No traffic rerouting, no new architecture.
Can Noma detect an agent acting outside its owner's permissions?
Yes. Noma ties each agent to its human owner and their IdP group, inspects behavior at runtime, and detects drift from the agent's intent or its baseline behavior.