Answer questions about AI risk with evidence
AI COMPLIANCE
Noma records what every agent is allowed to do and what it actually did, so the audit trail exists before anyone asks for it. Findings map to ISO 42001, the EU AI Act, NIST AI RMF, MITRE ATLAS, and the OWASP LLM Top 10 for audit-ready reporting.

Acme Inc.
Industry Co
Robust AI Security
Security and Governance
AI and Agents
Industry Co
RealBusiness
Acme Inc.
Industry Co
Robust AI Security
Security and Governance
AI and Agents
Industry Co
RealBusiness
Make your agent deployments audit-ready
Framework mappings
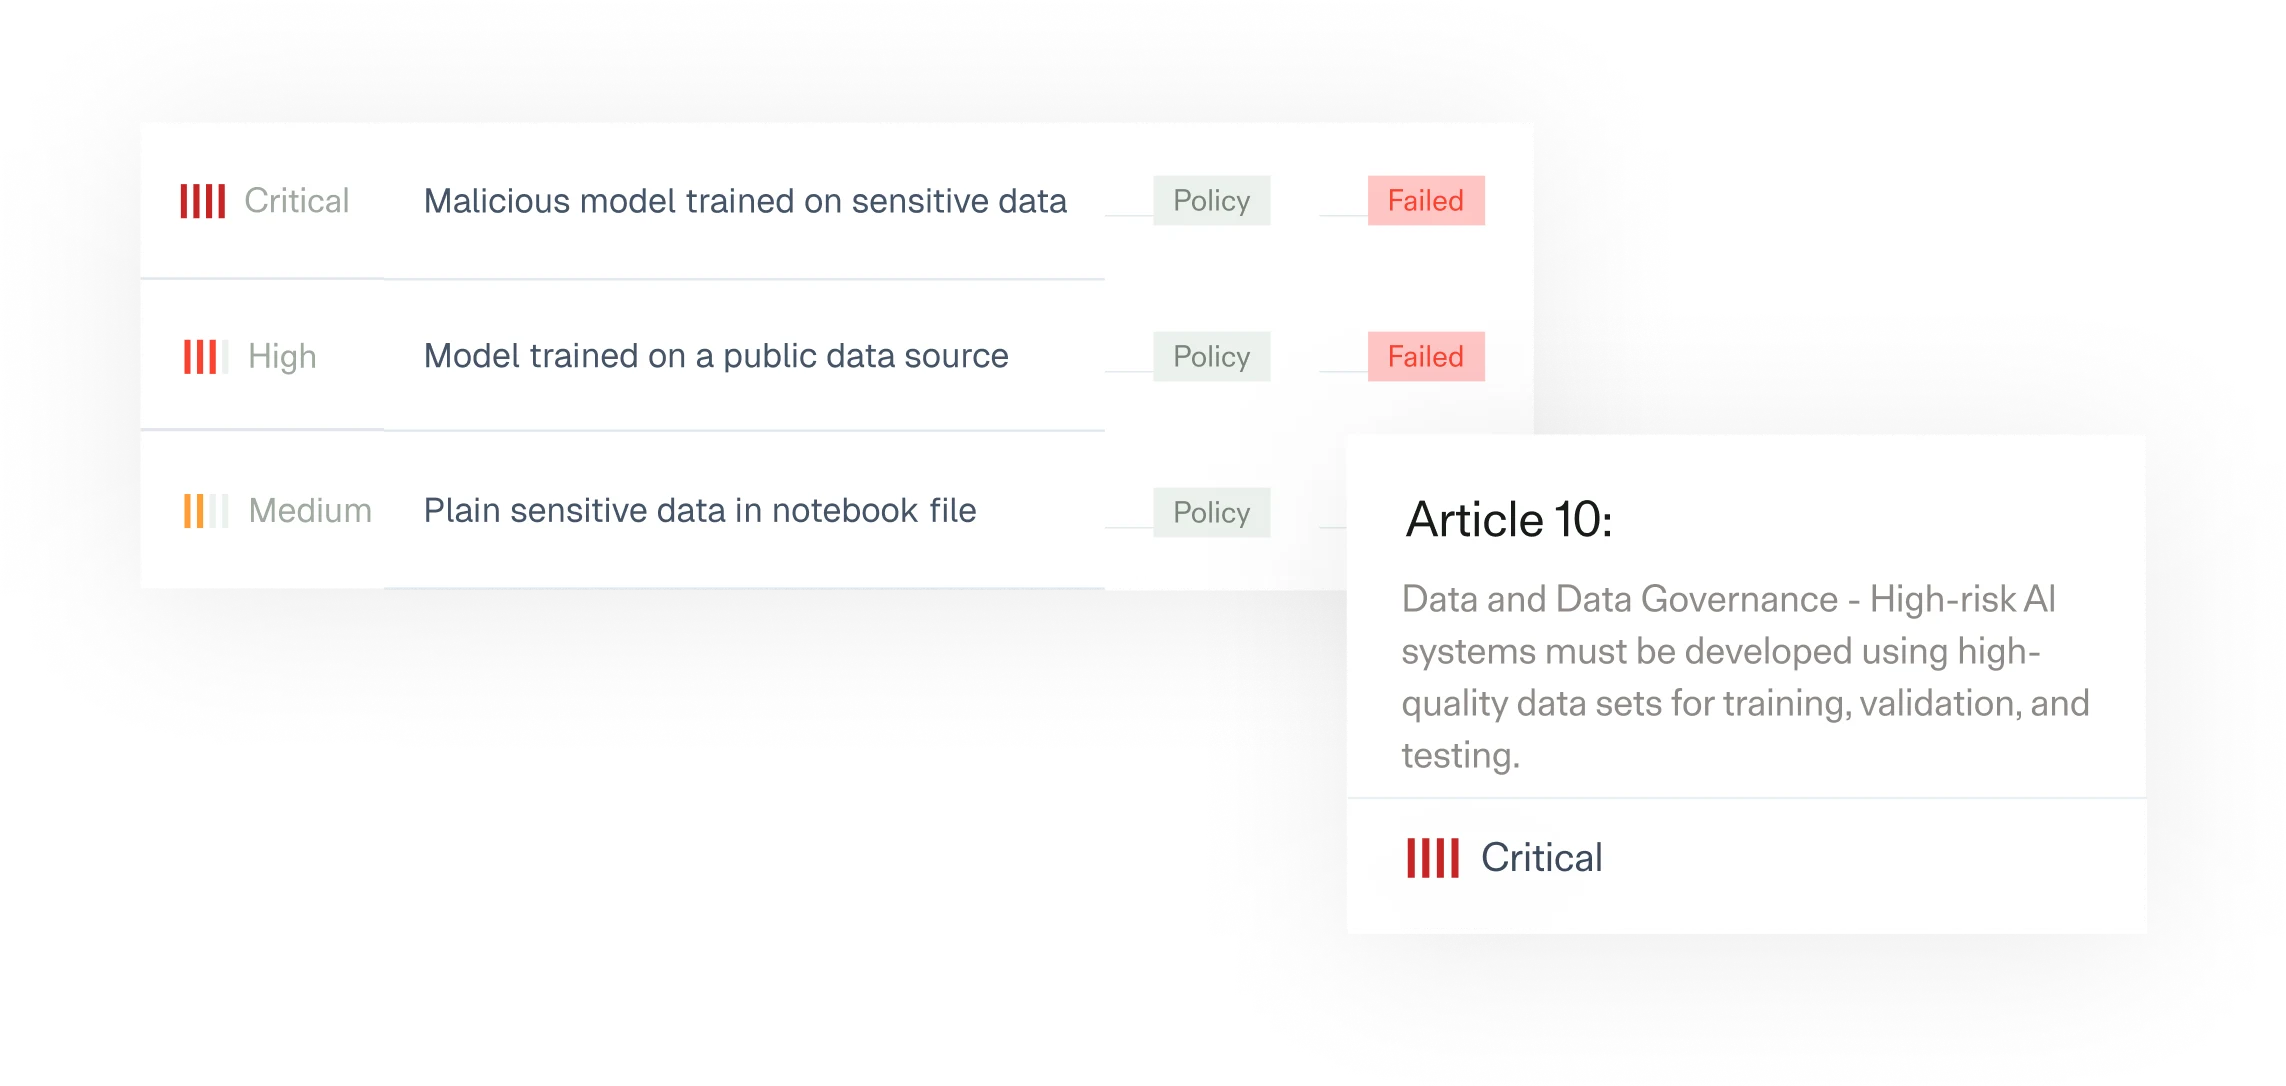
Every finding in the Noma platform maps to specific controls in the frameworks your organization needs to comply with: NIST AI RMF, EU AI Act, and ISO 42001 for regulatory compliance, and OWASP LLM Top 10 and MITRE ATLAS for industry benchmarks and security coverage. Each finding includes which control is affected and the severity, so GRC teams can prioritize remediation and track progress against their target framework.
Learn More
AI asset inventory
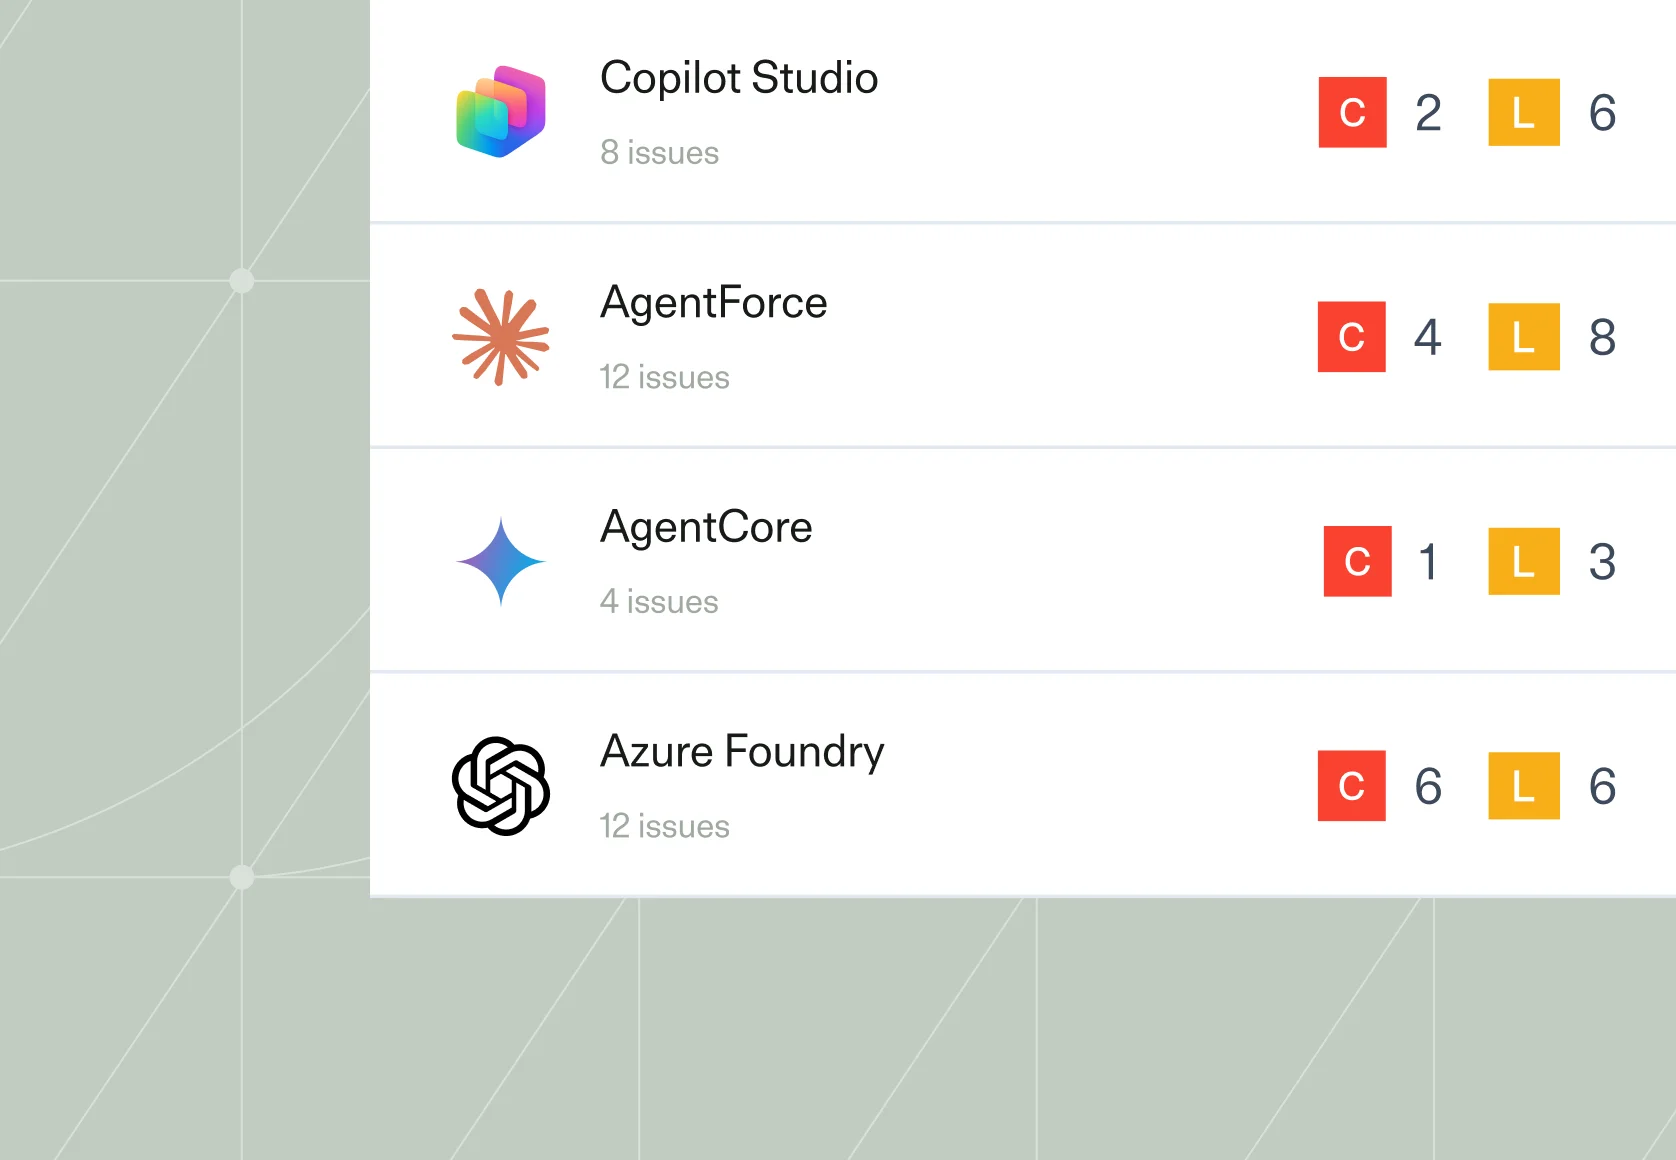
Compliance programs start with knowing what you have. Noma provides a continuous, auditable inventory of every AI agent, model, MCP server, tool, and data connection across your organization. This is the foundation auditors ask for first, and the one most organizations struggle to produce manually.
Learn More
Adversarial test evidence
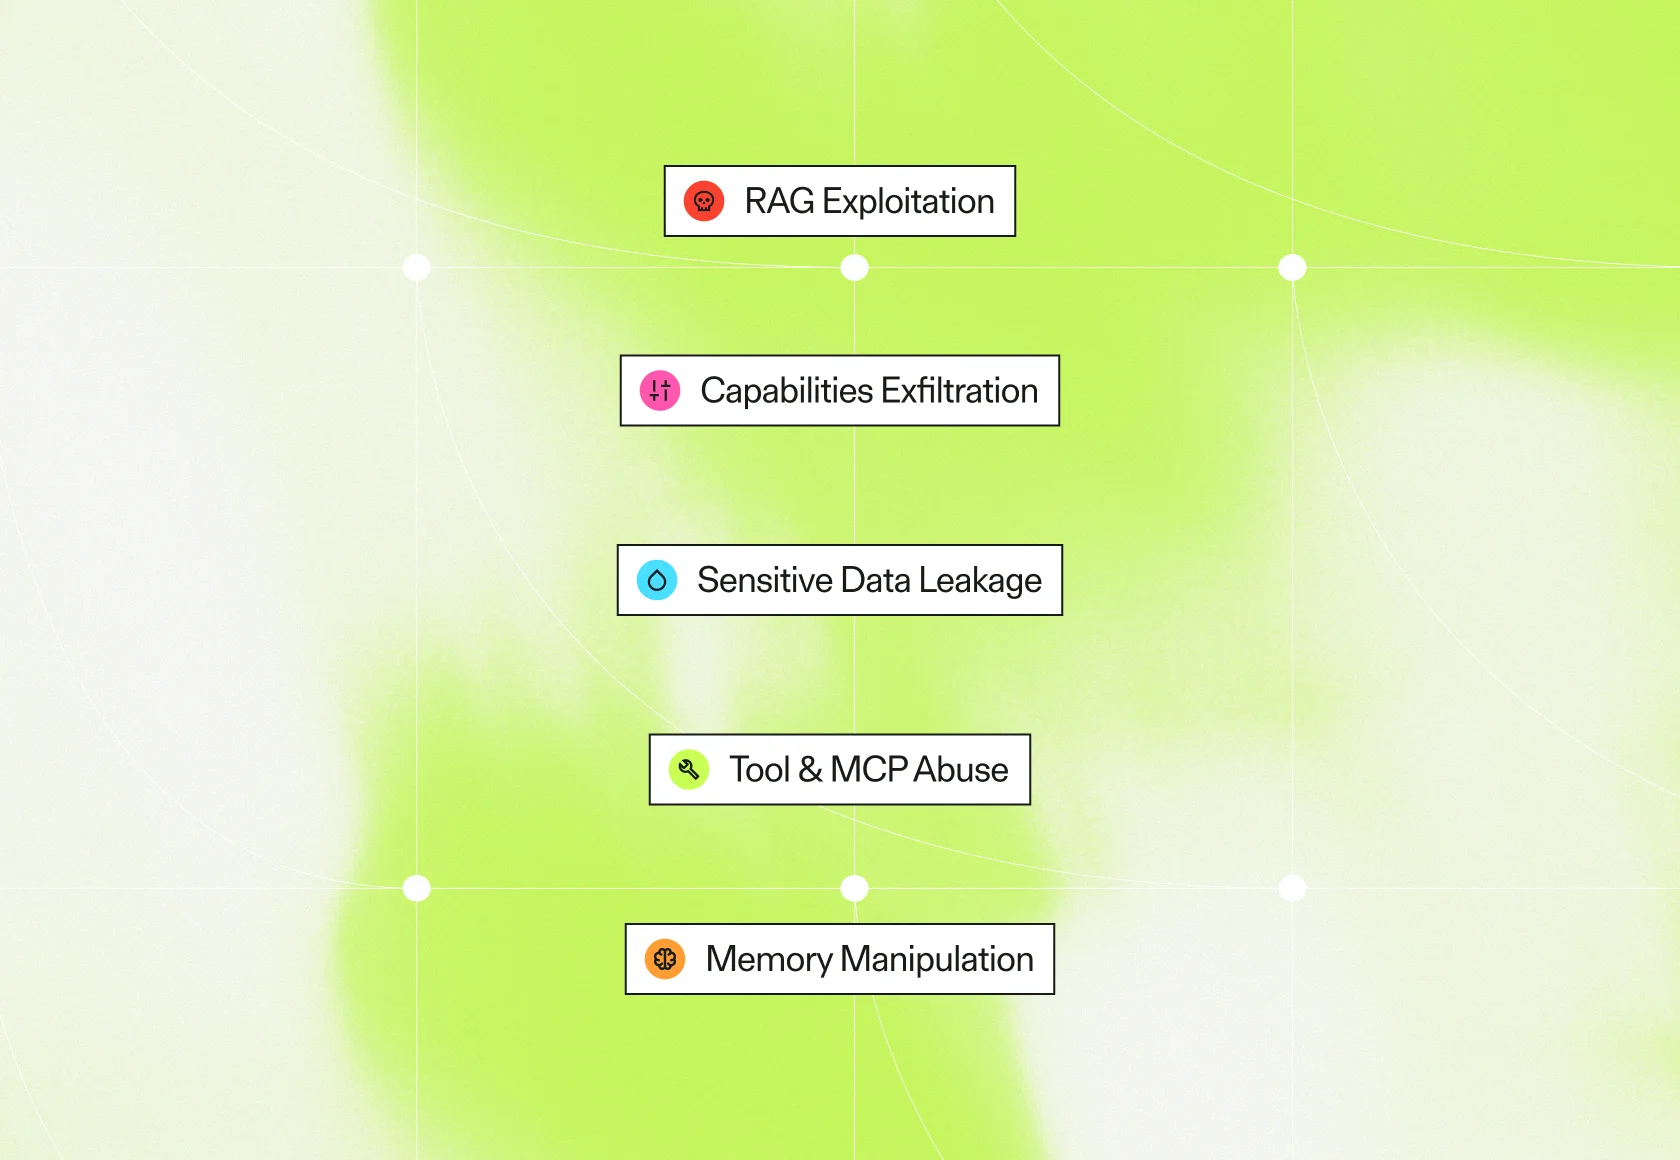
Regulators and auditors want proof that your AI applications have been tested for known attack categories. Noma AI Red Teaming generates quantitative results mapped to OWASP and MITRE ATLAS: which attacks were attempted, which succeeded, and what the current posture looks like.
Learn More
Runtime audit trails
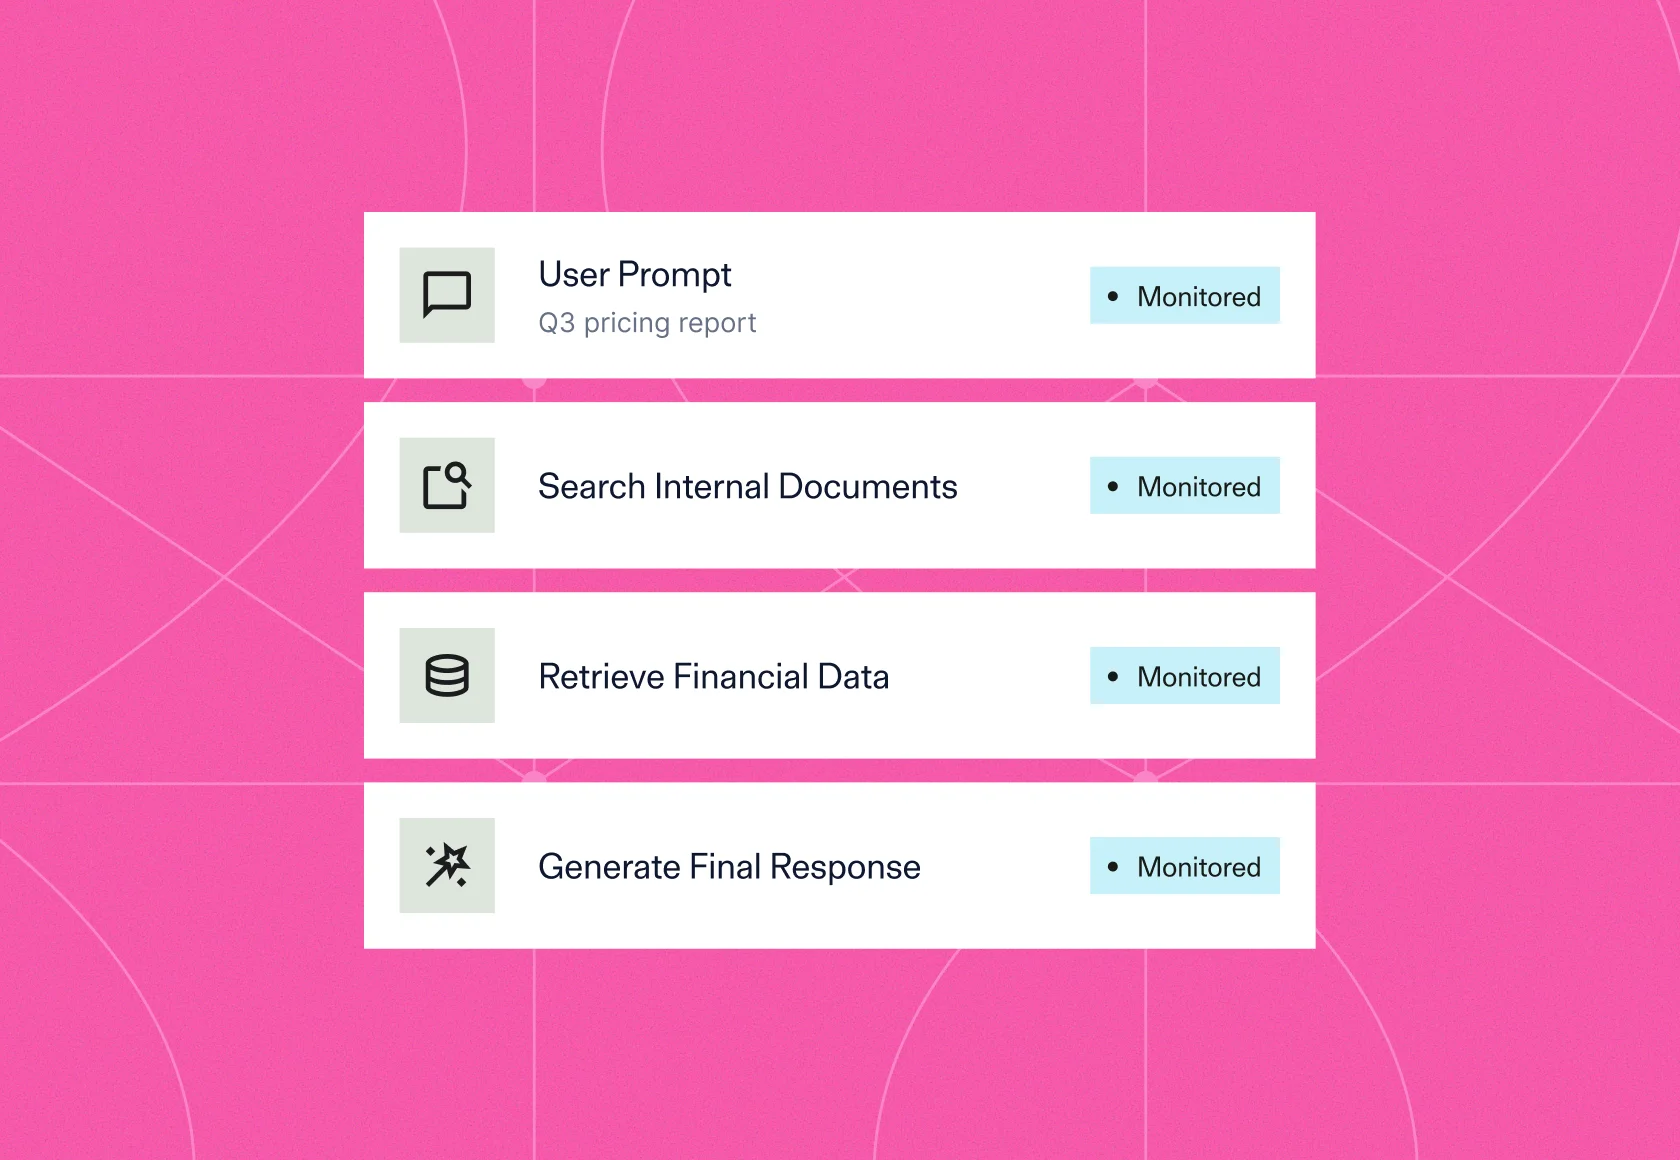
Proof that controls are configured is not enough. Auditors want to see that controls are actively enforced. Noma records every prompt, response, tool call, and enforcement action, providing a complete audit trail of what happened, what was detected, and what action was taken. Enterprise customers like UiPath actively use Noma's compliance capabilities to support their ISO 42001 certification.
Learn More
Staying current with regulations
Enterprise ready
Comprehensive coverage
Integrations built into 80+ data, AI and MLOps platforms, cloud, no-code and low-code agents, and source code management.
Open Enforcement
Decouple governance from any single control point and enforce policy through AI gateways, MCP gateways, agent hooks, agent SDKs, and direct APIs, using the infrastructure already in your environment.
Multiple deployment options
Support for both on-prem and SaaS deployments, so no model, training data, or security events leave your environment.
Built to Higher Standards.
FAQs
What AI regulations does Noma help with?

Noma maps findings and controls to the EU AI Act, NIST AI RMF, and ISO 42001, and to the OWASP LLM Top 10 and MITRE ATLAS security benchmarks, with framework-specific evidence for auditors.
What evidence does Noma produce for auditors?
A continuous AI asset inventory, framework control mappings with severity, adversarial test results, and runtime audit trails covering every prompt, tool call, and enforcement action.
Does Noma track regulatory changes?
Yes. Noma monitors regulatory developments and updates its compliance mappings, so teams stay current without chasing changes across NIST, ISO, and EU AI Act requirements.
Can Noma support ISO 42001 certification?
Yes. Noma's inventory, policy governance, testing evidence, and runtime audit trails map to ISO 42001 controls. Enterprise customers like UiPath use Noma's compliance capabilities to support their ISO 42001 certification.