AI agents went from pilot to production faster than almost anyone planned for. Security teams are now being asked to govern software that reads company data, calls tools, and takes action on its own, often with controls built for a different era.
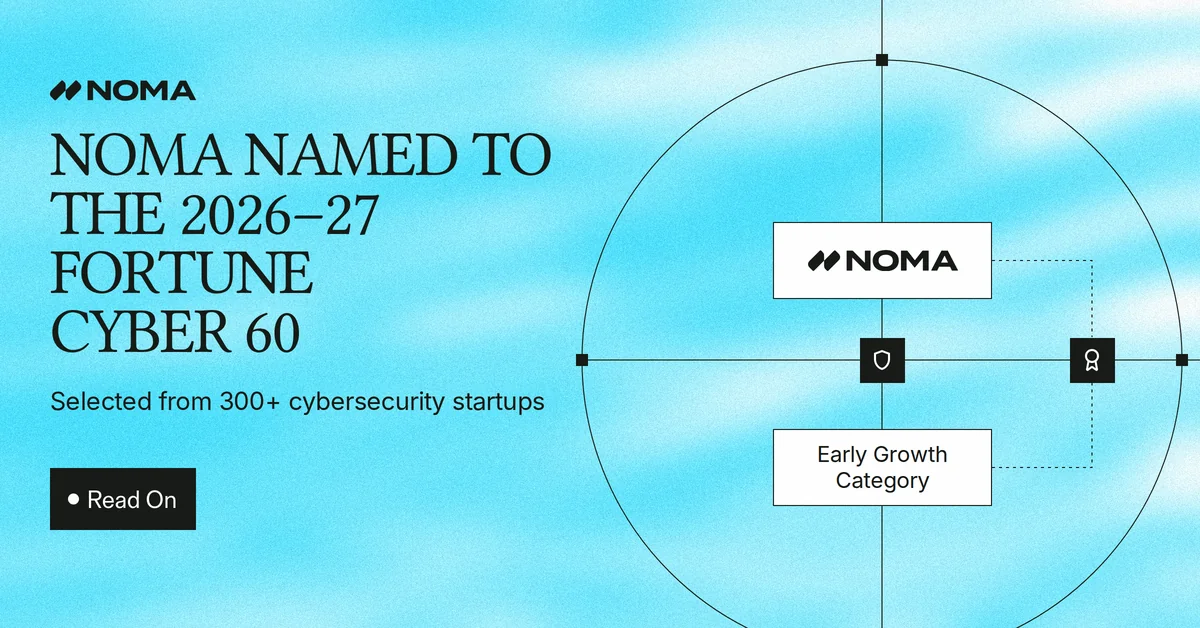
That's the problem Noma was built to solve, and today we're proud to share that Noma has been named to the 2026–27 Fortune Cyber 60, in the early growth category. The list is presented by Lightspeed Venture Partners and Amazon Web Services in partnership with Fortune, and it recognizes 60 of the most important venture-backed cybersecurity companies.
Now in its fourth year, the list names 20 companies in each of three stages: early stage, early growth, and growth. Lightspeed evaluated more than 300 cybersecurity startups, weighing annual recurring revenue, growth over the current and prior year, and business operations, and Fortune reviewed and validated the final list. You can see the full list at https://lsvp.com/cyber60-2026-2027/.
Agents are moving faster than the controls around them
Lightspeed published the list alongside its Cyber60 CISO Survey, conducted by Wakefield Research among 200 U.S. CISOs at companies with at least $500 million in annual revenue. The findings line up closely with what we hear from security leaders every week:
- AI agents are in production at 77% of surveyed companies.
- Only 20% of companies using or exploring agents have a complete agent inventory.
- Confidence is slipping. Teams' confidence in assessing and mitigating AI-specific risks fell from 71% last year to 55%.
- Access is the next frontier. Agent identity, authorization, and access governance is the top category CISOs plan to evaluate over the next year, at 55%.
The threat picture is shifting with it. Compromised or hijacked agents now tie AI-generated phishing and deepfakes as CISOs' top AI threat, at 51%, and 48% plan to evaluate runtime guardrails for agents in production. Lightspeed's own opportunity map puts agent identity and access governance and agent runtime security at the top of its list.
Put simply: most enterprises already have agents doing real work, and most can't yet say exactly which agents they have, what those agents can reach, or what they're doing with that access.
Why permitted actions are the hard part
Access permissions tell you what an agent may use. They don't tell you what it will do with that access. An agent might be allowed to read sensitive data and allowed to send a message, yet sending that data outside the organization is exactly what you need to stop. Agents can also be manipulated, drift from their instructions, or simply make mistakes, with no attacker involved.
Stopping that kind of sequence takes context: the task, the identity behind the agent, the data involved, and the actions leading up to the moment that matters. That's why we built Noma as one agent control plane, owned by security and serving the entire business. It brings discovery, access control, red teaming, and runtime protection together across endpoint, SaaS, and cloud environments.
At its core, Noma's Runtime Context Engine connects identity, intent, blast radius, and behavior over time to detect when permitted actions become dangerous. Controls work through the gateways, agent hooks, and APIs teams already use, so security can step in when behavior turns risky without forcing the business to change its AI tools or architecture.
Acknowledgements
This recognition belongs to our team, our customers, and the security leaders who've trusted us with some of their hardest problems. Thank you to Lightspeed, AWS, and Fortune for the recognition, and congratulations to our fellow honorees.
Want to see how Noma stops rogue agents without slowing your business down? Book a demo and we'll walk you through it.