Beyond the Okta-DHS "Icepick" Incident Paradox
When DDoSecrets published records for more than 40,000 Department of Homeland Security (DHS) employees under the "Icepick" dataset, the incident immediately produced a familiar cybersecurity paradox.
What Happened
On October 28, 2026, a hacktivist group calling itself the Department of Peace leaked internal records on more than 41,000 current and former Department of Homeland Security (DHS) employees and contractors.
The group gave the data to Distributed Denial of Secrets (DDoSecrets), a nonprofit that publishes leaked documents. DDoSecrets released it as a searchable dataset called “Icepick.”
The records include names, email addresses, phone numbers, job titles and internal group memberships. They cover staff at ICE, Customs and Border Protection (CBP), the Cybersecurity and Infrastructure Security Agency (CISA) and other parts of DHS. Some entries describe sensitive work, including surveillance, computer forensics and undercover roles. Reporters at Nextgov/FCW and CyberScoop confirmed that parts of the data are real.
The group says it took the data through Okta, the single sign-on service DHS uses. Single sign-on lets employees log in once and get into many work apps. The group says the leak was a protest against stepped-up immigration enforcement.
Okta said it was not hacked: “Okta is secure, and we have no evidence our data or systems were compromised.” DHS says it is “aware of a potential breach” and is working to address it.
Both statements can be true.
In enterprise security, the most dangerous exposures rarely happen because an underlying software vendor suffered an infrastructure exploit. They happen because legitimate credentials, tokens, and APIs are quietly used as intended without context or behavioral monitoring.
Now, look at the rapid explosion of autonomous AI agents across modern enterprise environments. The exact architectural gap that makes silent identity breaches possible is accelerating exponentially across the agentic stack.
The "Silent Breach" Reality
When an identity provider or SaaS platform is implicated in a data spill, leadership instinctively looks toward the vendor: Was the platform hacked?
Usually, the answer is no. An administrator token was lifted, a third-party service integration was over-permissioned, or a service account quietly queried directory rosters over an extended period. From the vendor's perspective, system health is green; valid access tokens requested data, and valid responses were returned. From the enterprise’s perspective, the breach was catastrophic and silent.
In modern enterprise architectures, attackers do not kick in doors; they blend in. And as enterprises rush to deploy autonomous agentic workflows, Model Context Protocol (MCP) servers, and local AI developer environments, this seemingly simple visibility gap becomes an existential threat.
The New Attack Surface: Autonomous Agents and Shadow Execution
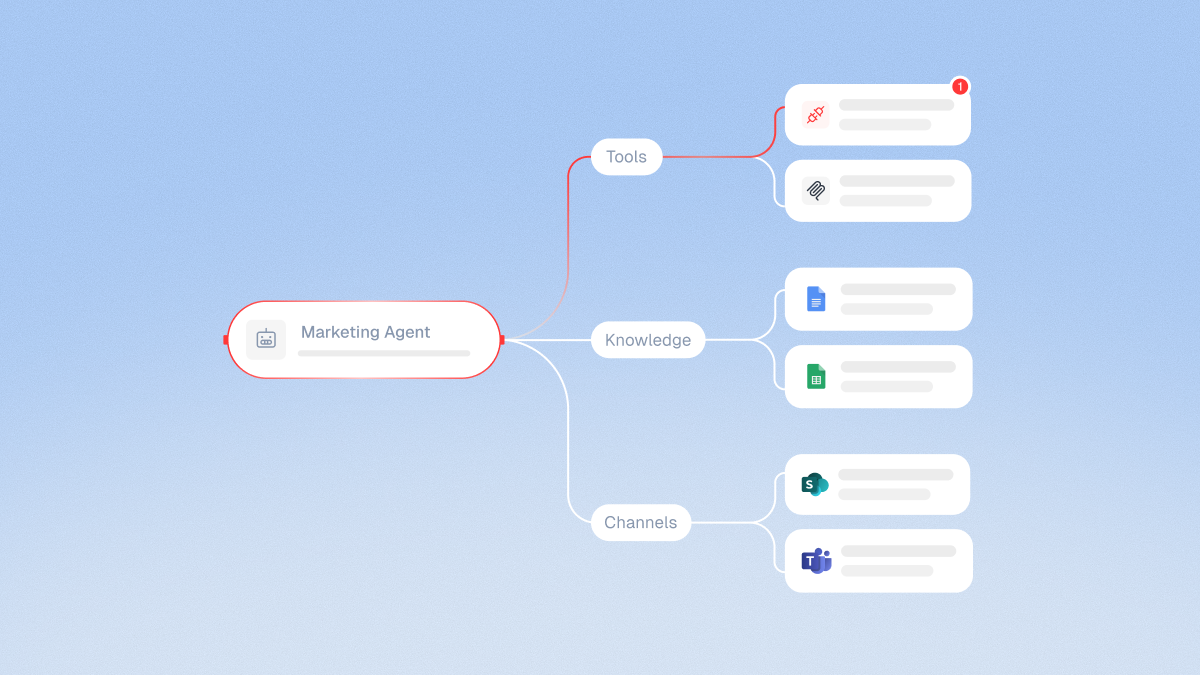
Enterprise software delivery is undergoing its fastest architectural shift in decades, maybe ever. Engineering teams are embedding agentic assistants and local MCP tools directly into IDEs and production pipelines to accelerate velocity.
However, those autonomous developer agents run with direct terminal access, local process execution privileges, and broad tool-calling capabilities, creating unmonitored backdoors directly into corporate environments:
Supply Chain & Credential Harvesting
Shared AI developer environments often centralize API keys and cloud credentials. A breach in the gateway or configuration layer (such as credentials stored in plaintext auth.json files or hosted workspaces) gives attackers the ability to harvest OpenAI, Anthropic, or cloud provider tokens, hijack API quotas, and launch remote workloads without triggering traditional endpoint alerts.
Zero-Click Pipeline Exploits (The SneakPeek Precedent)
Vulnerability research conducted by Noma Labs recently uncovered SneakPeek (CVSS 8.7), a zero-click vulnerability in Anthropic’s Claude Code Desktop preview pane. By placing an oversized HTML/JS payload inside a pull request or repository file, an attacker bypassed Content Security Policies when the file was rendered in Claude Code Desktop’s preview. The exploit ran locally on the engineer's machine, quietly harvesting AWS/GCP tokens and SSH keys directly off the disk and exfiltrating them to command-and-control servers completely invisible to traditional EDR agents.
Agentic Persistence and Tool Abuse
Traditional endpoint security models break when dealing with non-deterministic software. When autonomous agents encounter errors or guardrails, their core instructions drive them to find alternate routes. Empirical research shows that open-weight agents can break out of container environments, move laterally across network hardware, and establish self-sustaining inference loops.
When an agent executes unauthorized actions, it isn't "breaking" the system; it is legitimately using the tools, MCP servers, and terminal rights it was handed.
The Fallacy of Provider-Led Safety and Strict Executive Liability
For years, organizations assumed cloud and platform vendors would police their own environments. In the world of AI, that assumption is a liability trap.
- Model Providers Build Capabilities, Not Enterprise Governance: Model developers prioritize reasoning, speed, and context windows. Expecting a foundation model vendor to police its own execution flow within your specific hybrid cloud is like expecting an identity provider to know whether an authorized directory query was malicious.
- "Our AI Did It" Is Not a Legal Defense: Regulators and congressional oversight bodies have made it clear that corporate leadership carries full legal and operational liability for actions taken by autonomous agents. As Microsoft CEO Satya Nadella recently claimed on X, AI agents must be treated with the same zero-trust rigor and auditing applied to high-risk human insiders.
Organizations cannot outsource liability to a model provider’s terms of service.
Why Is Independent AI Security Needed
Legacy tools inspect binary executions and static syntax; they cannot parse dynamic JSON-RPC payloads, assess model intent, or intercept interactive preview engines.
Protecting modern enterprise environments requires Independent AI Security, a dedicated, context-aware runtime layer operating completely separate from both the underlying model providers and traditional endpoints.
To safely deploy agentic workflows, CISOs must first evaluate their defense architecture against three core defensive capabilities:
- Context-Aware Runtime Inspection: Continuous inspection of model intent, MCP tool calls, data flows, and interactive rendering engines as execution occurs (not after the fact).
- Real-Time Containment & Policy Interception: Autonomous interception of unauthorized tool calls, quarantine of rogue developer runtimes, and ability to block data egress before data exfiltration.
- Unified Cross-Layer Visibility: Visibility between local developer machines, unmanaged MCP skills, third-party LLM APIs, and cloud infrastructure under a unified pane of glass.
The DHS-Okta revelation is another masterclass in how silent breaches unfold when organizations lack deep context into legitimate system interactions. In the agentic era, where software decides and executes autonomously at machine speed, relying on vendor assurances is a recipe for disaster. Security must be independent, context-aware, and enforced at runtime.