Secure endpoint, SaaS, and cloud agents in one place.
Find agents your team doesn't know about
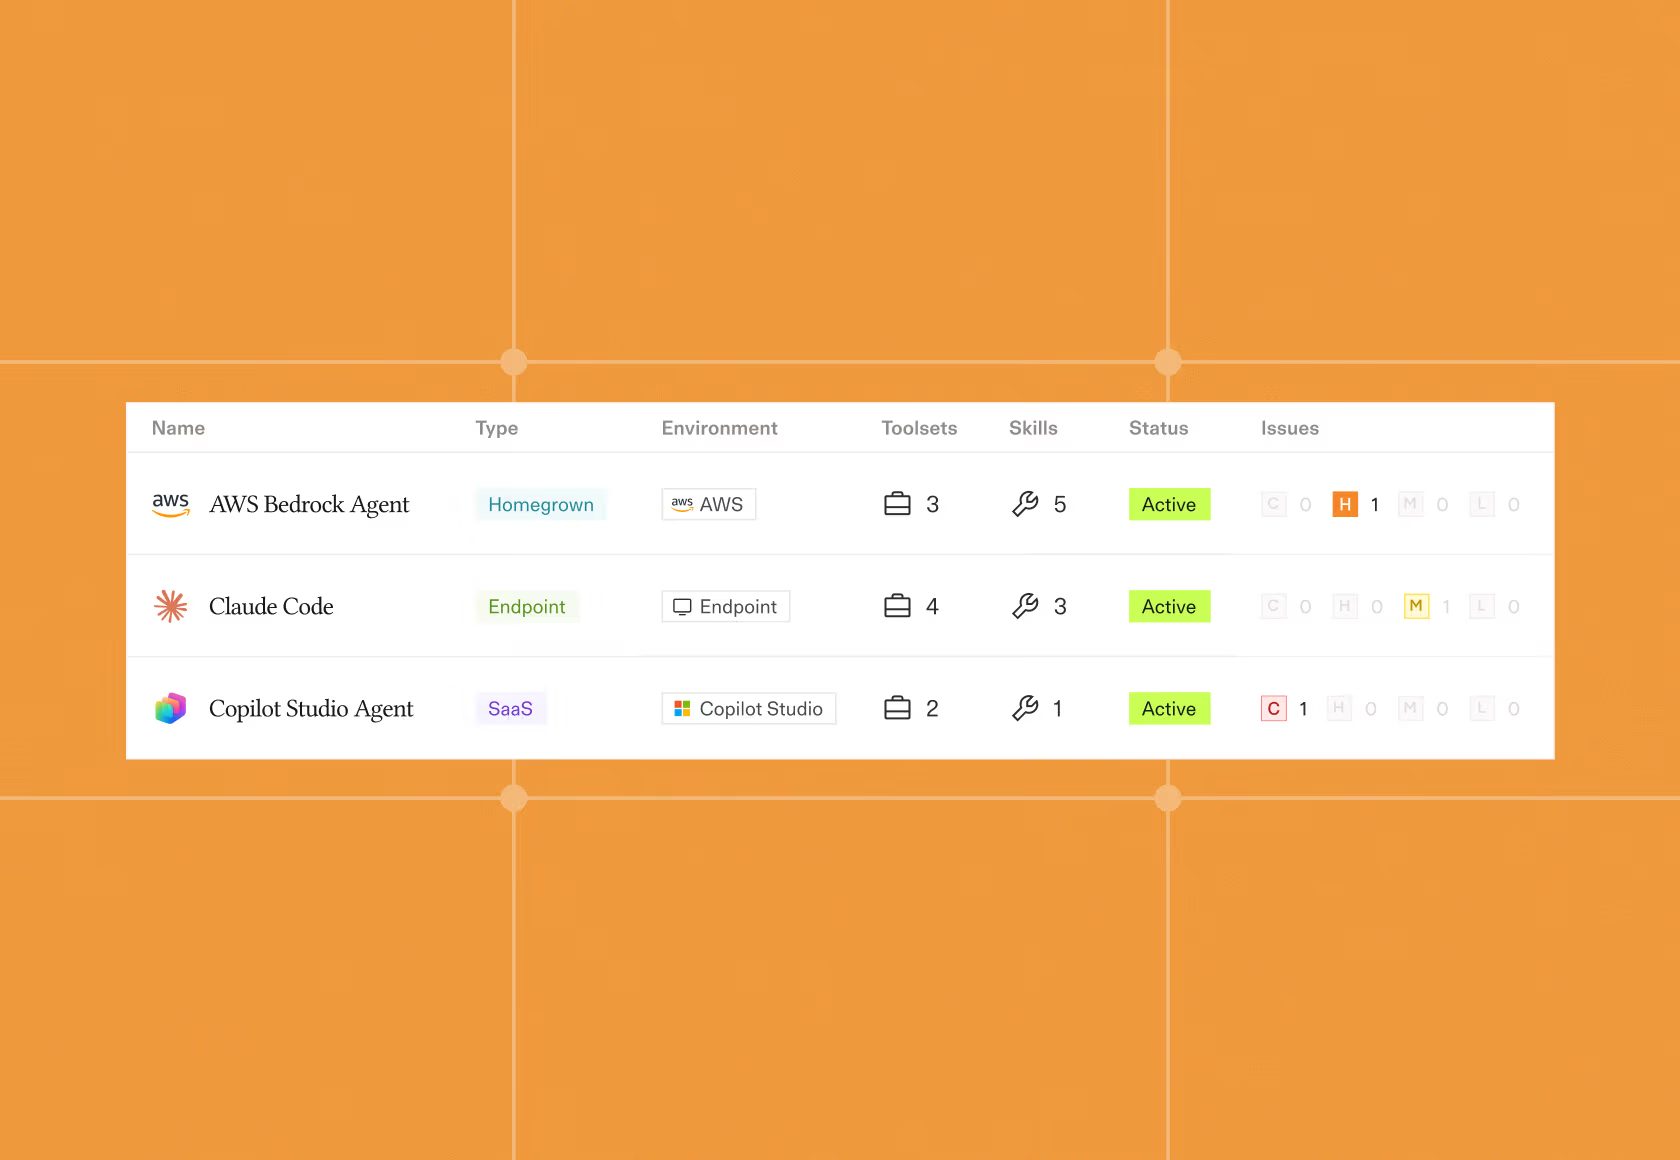
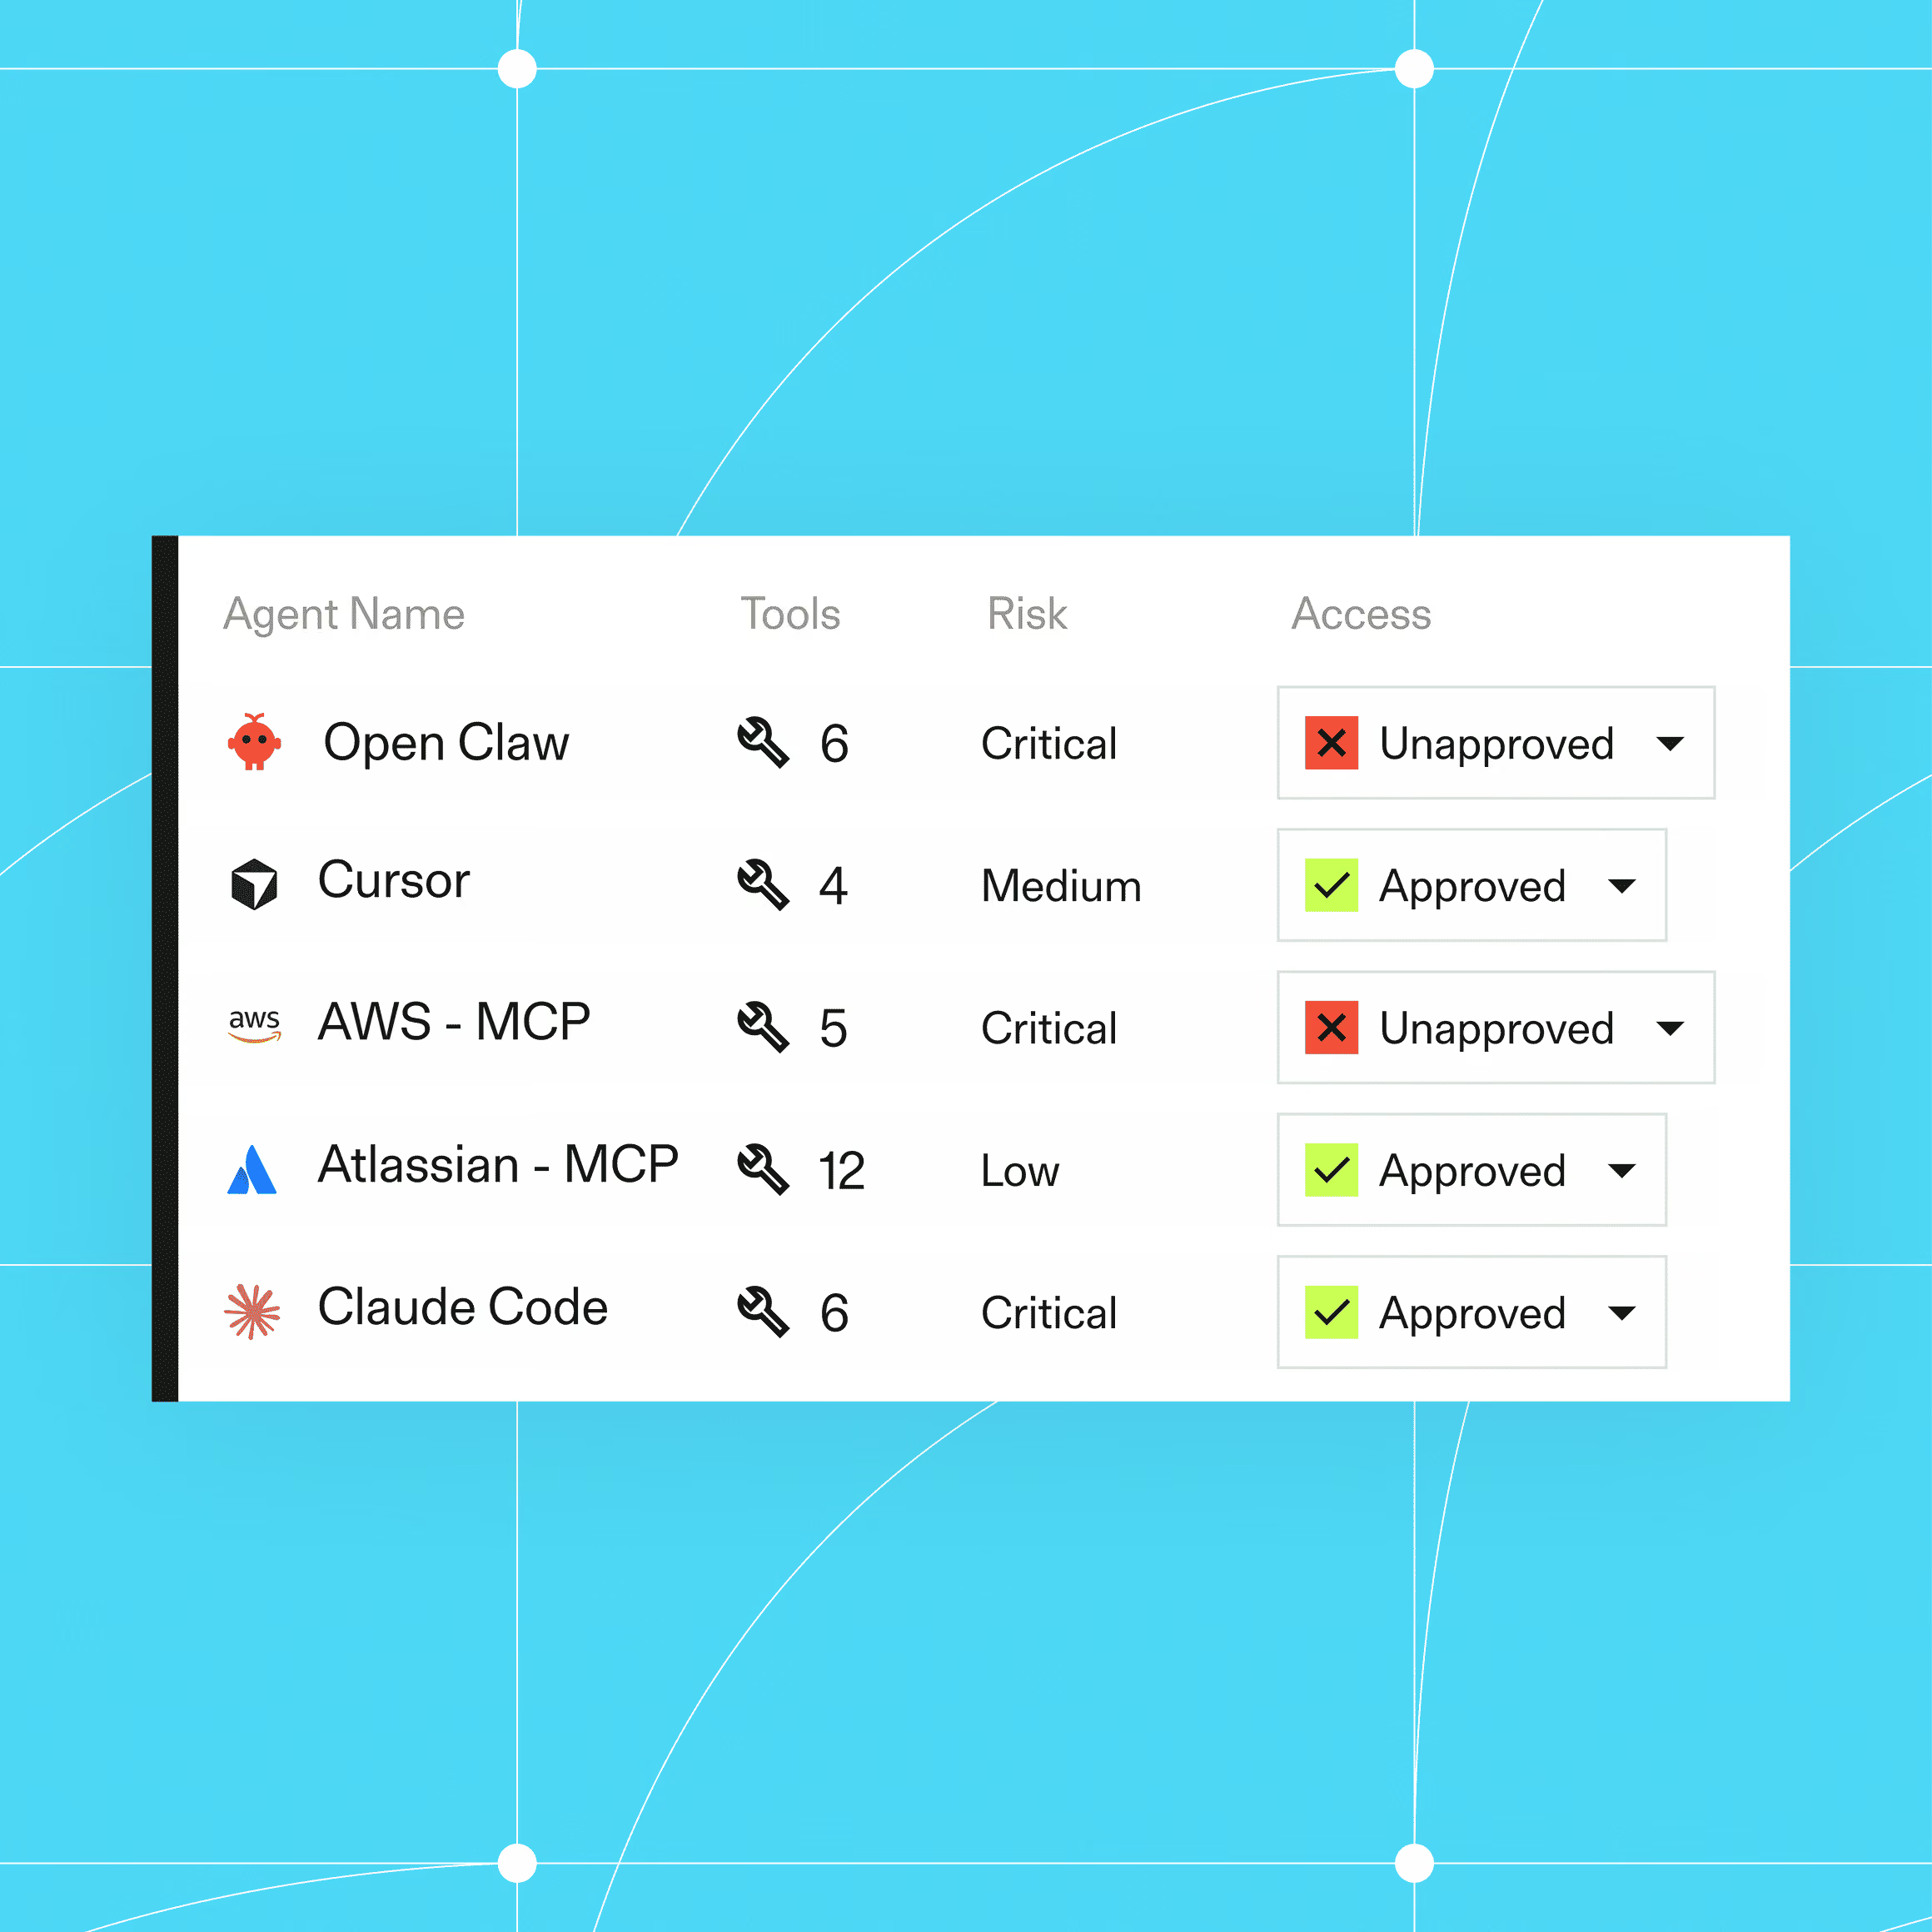
Find every agent, MCP server, toolset, skill, and model, across all agent types: endpoint, SaaS, and cloud.
Find toxic combinations of agent capabilities
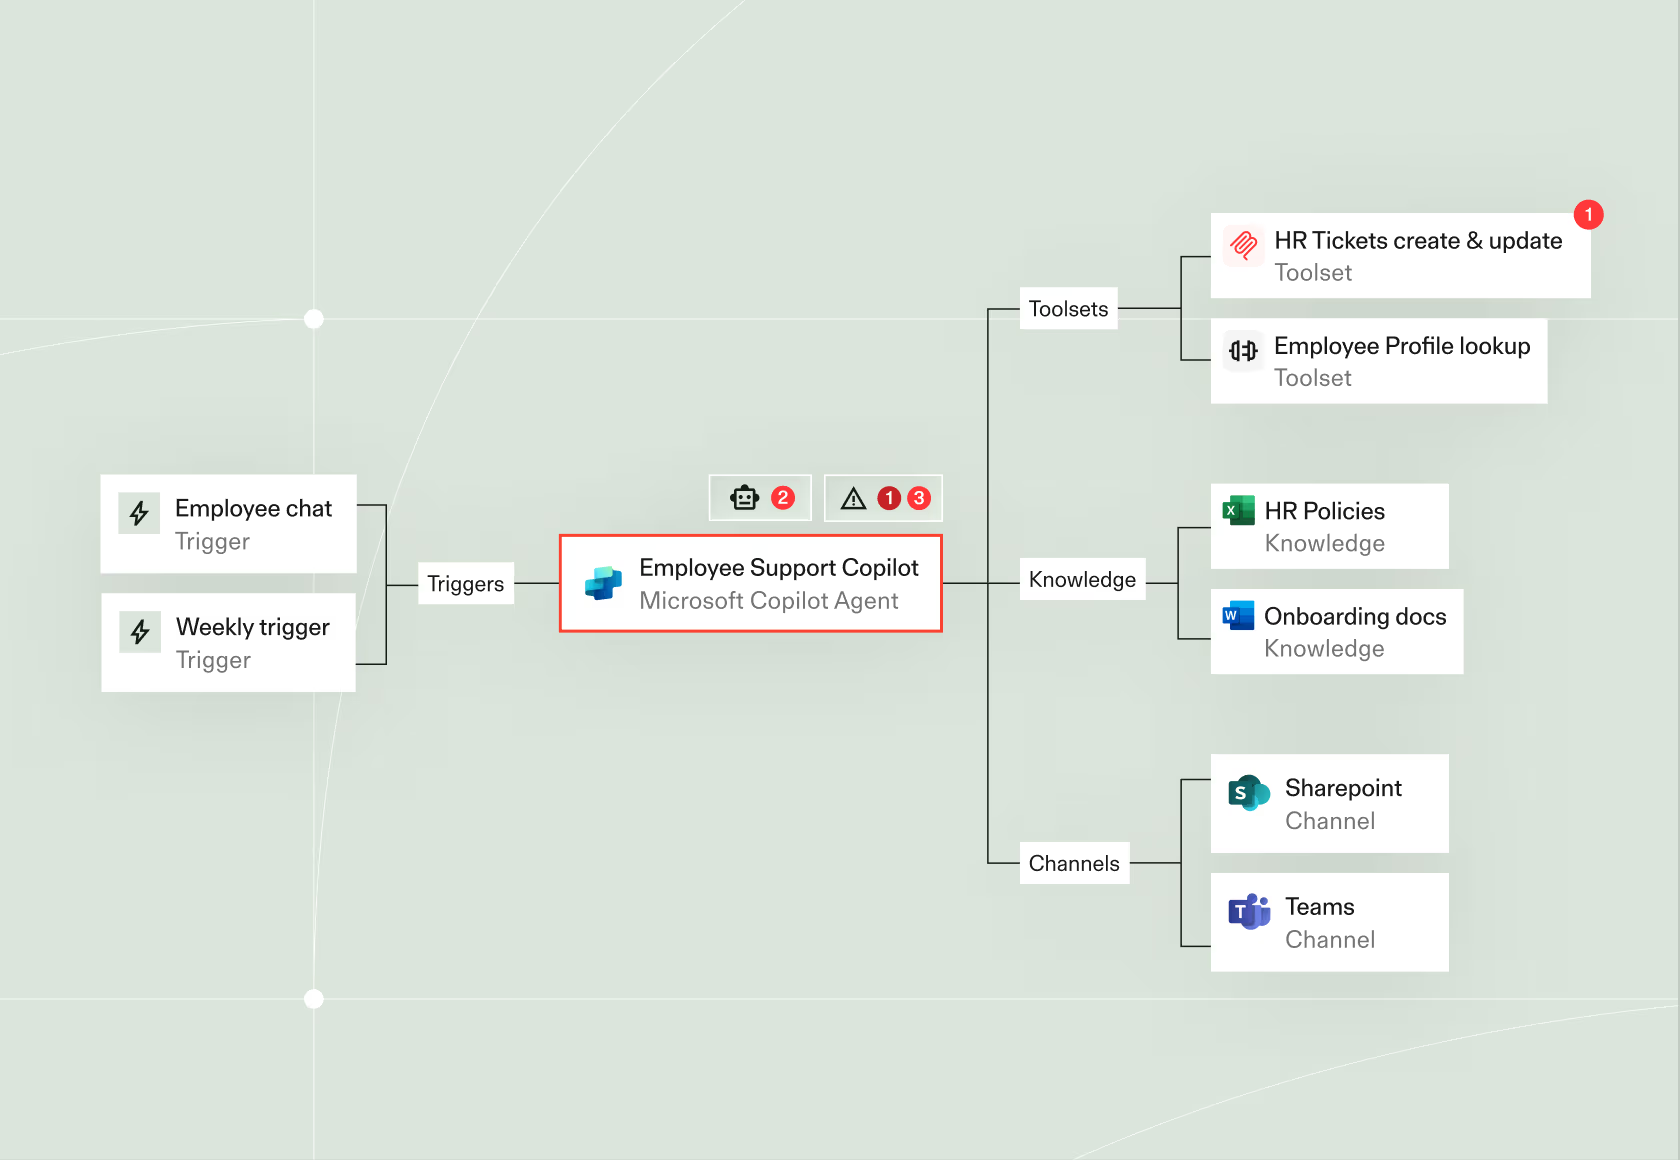
Evaluate an agent's compounding risk from its tools, data access, communication channels, triggers, users, and connected agents, based on hundreds of out of the box policies.
Map to frameworks and standards
Map findings to NIST AI RMF, EU AI Act, ISO 42001, OWASP LLM Top 10, and MITRE ATLAS. Noma monitors regulatory changes so your team stays current without having to chase updates across frameworks.
Control supply chain sprawl
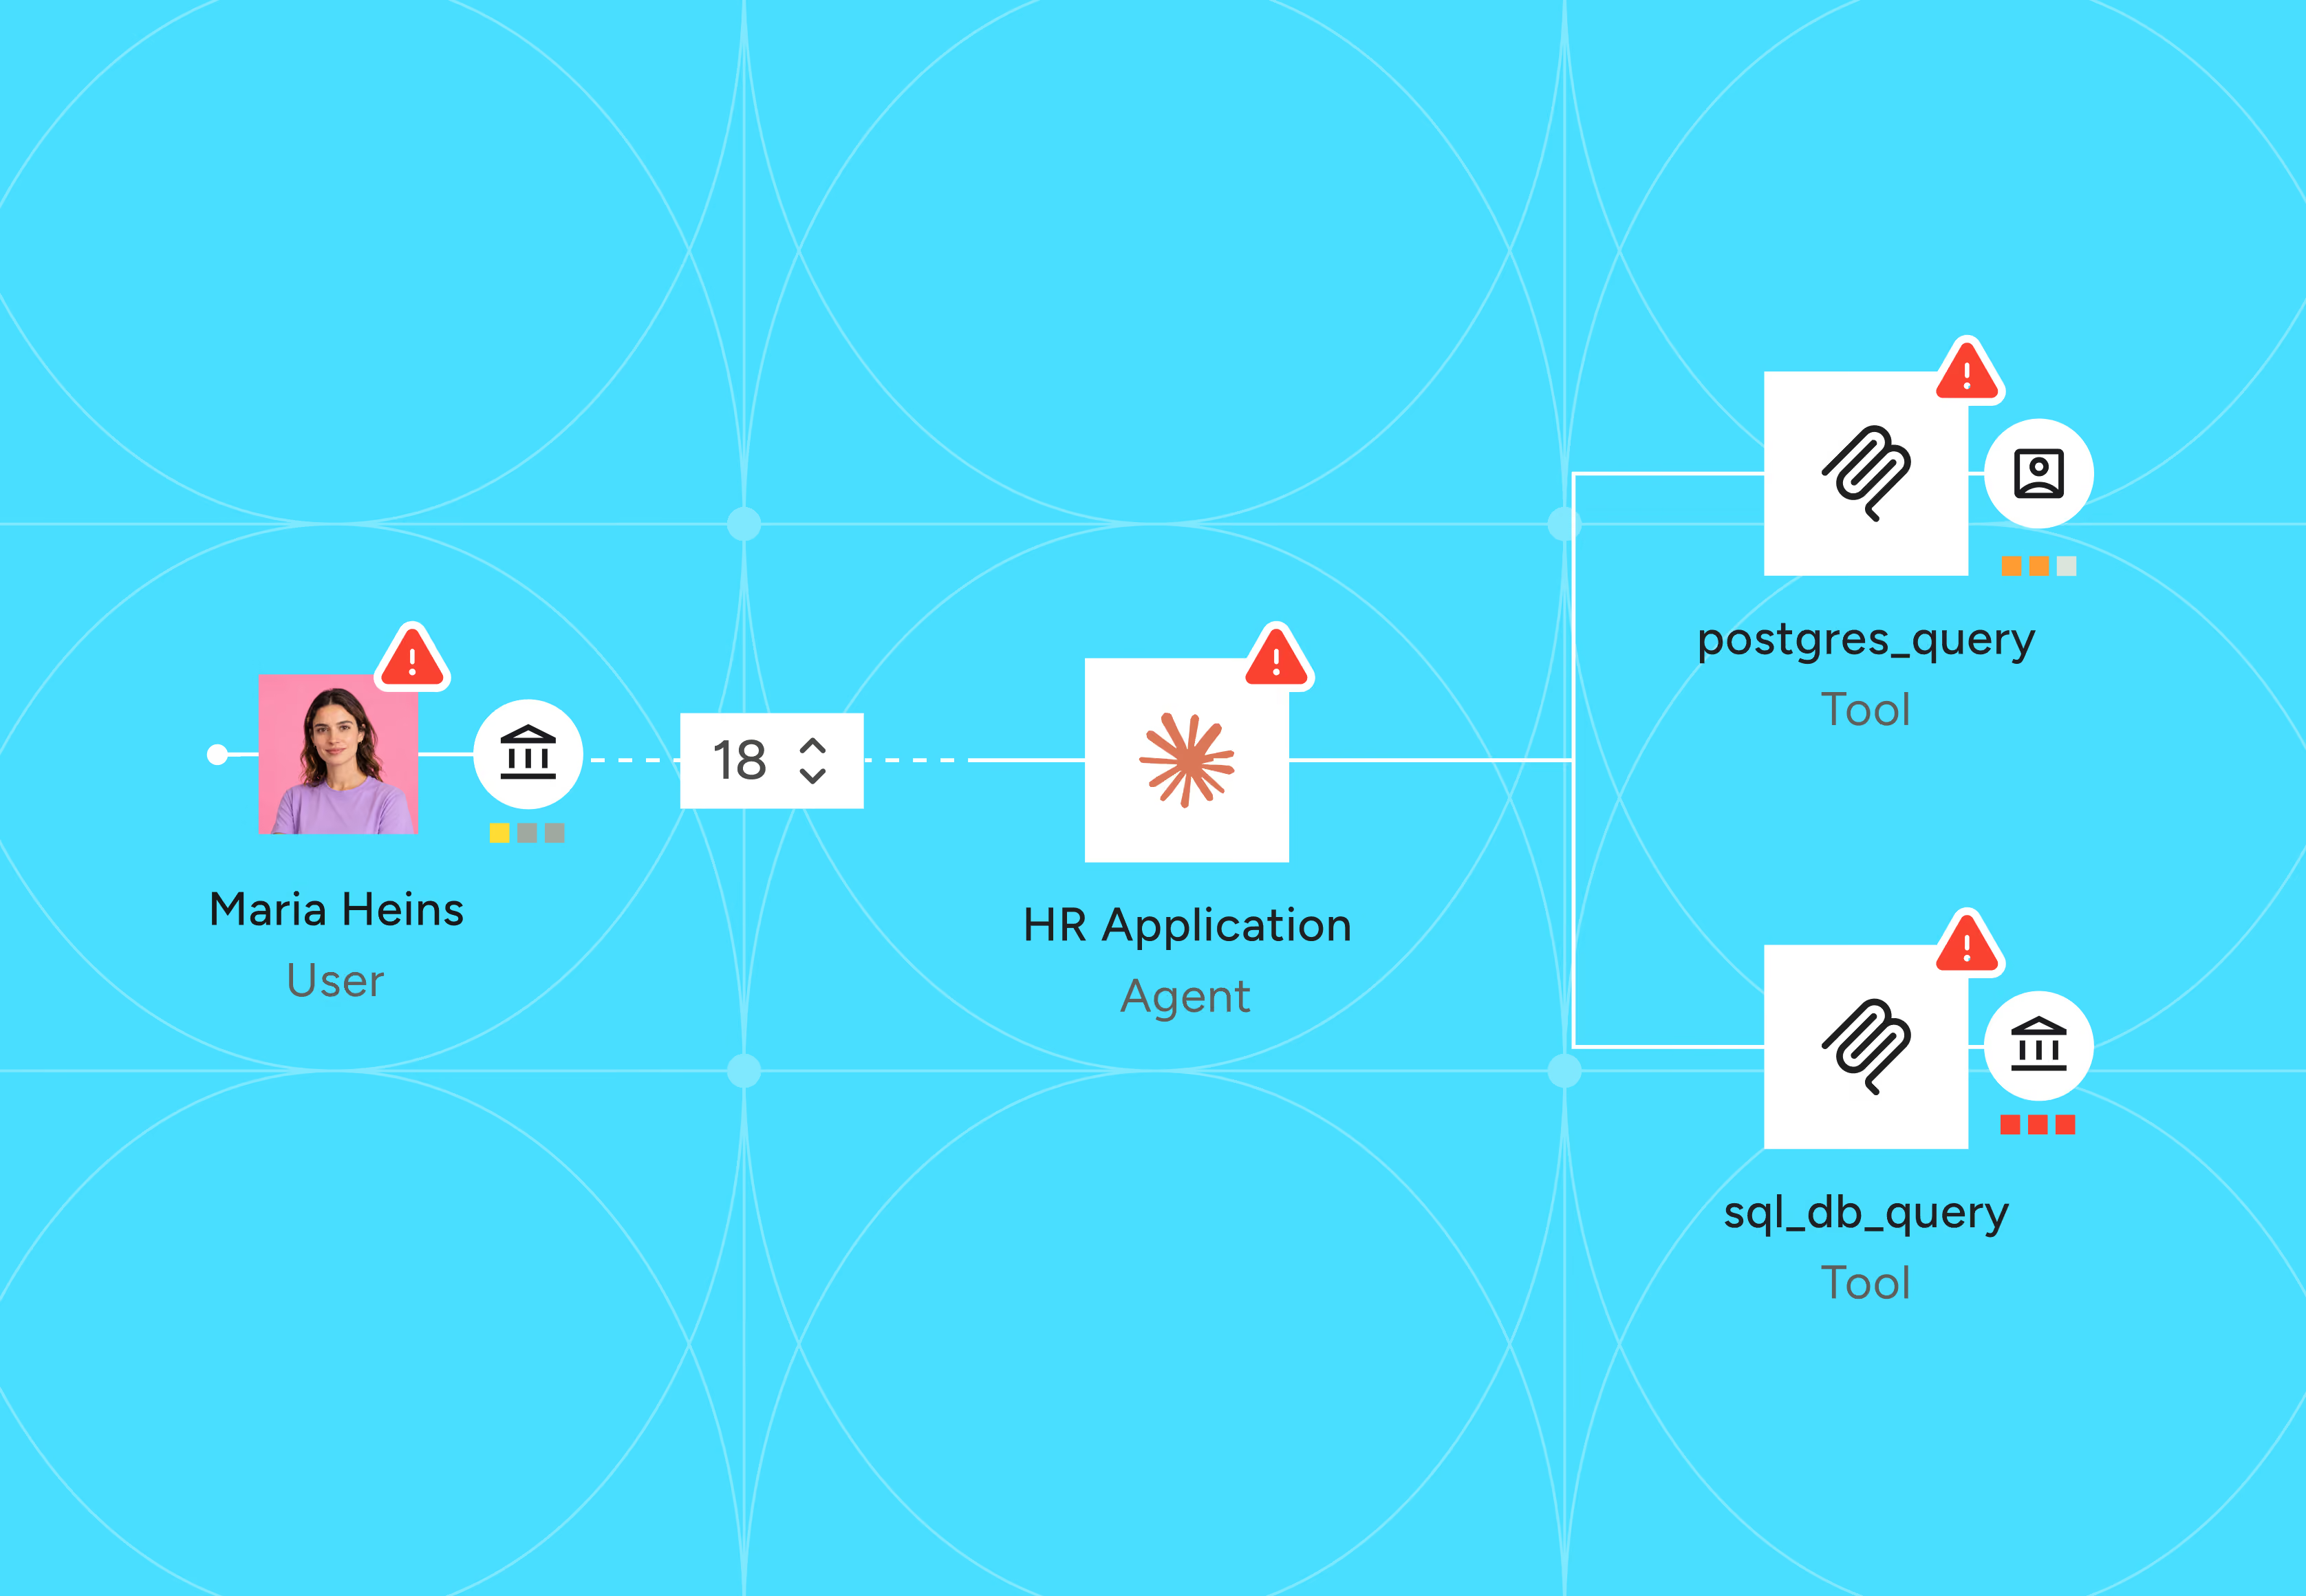
Inspect MCP servers, models, and skills for risk in the agent supply chain, and build a live registry of which AI components are allowed in the organization.
Catch misconfigurations and malpractices
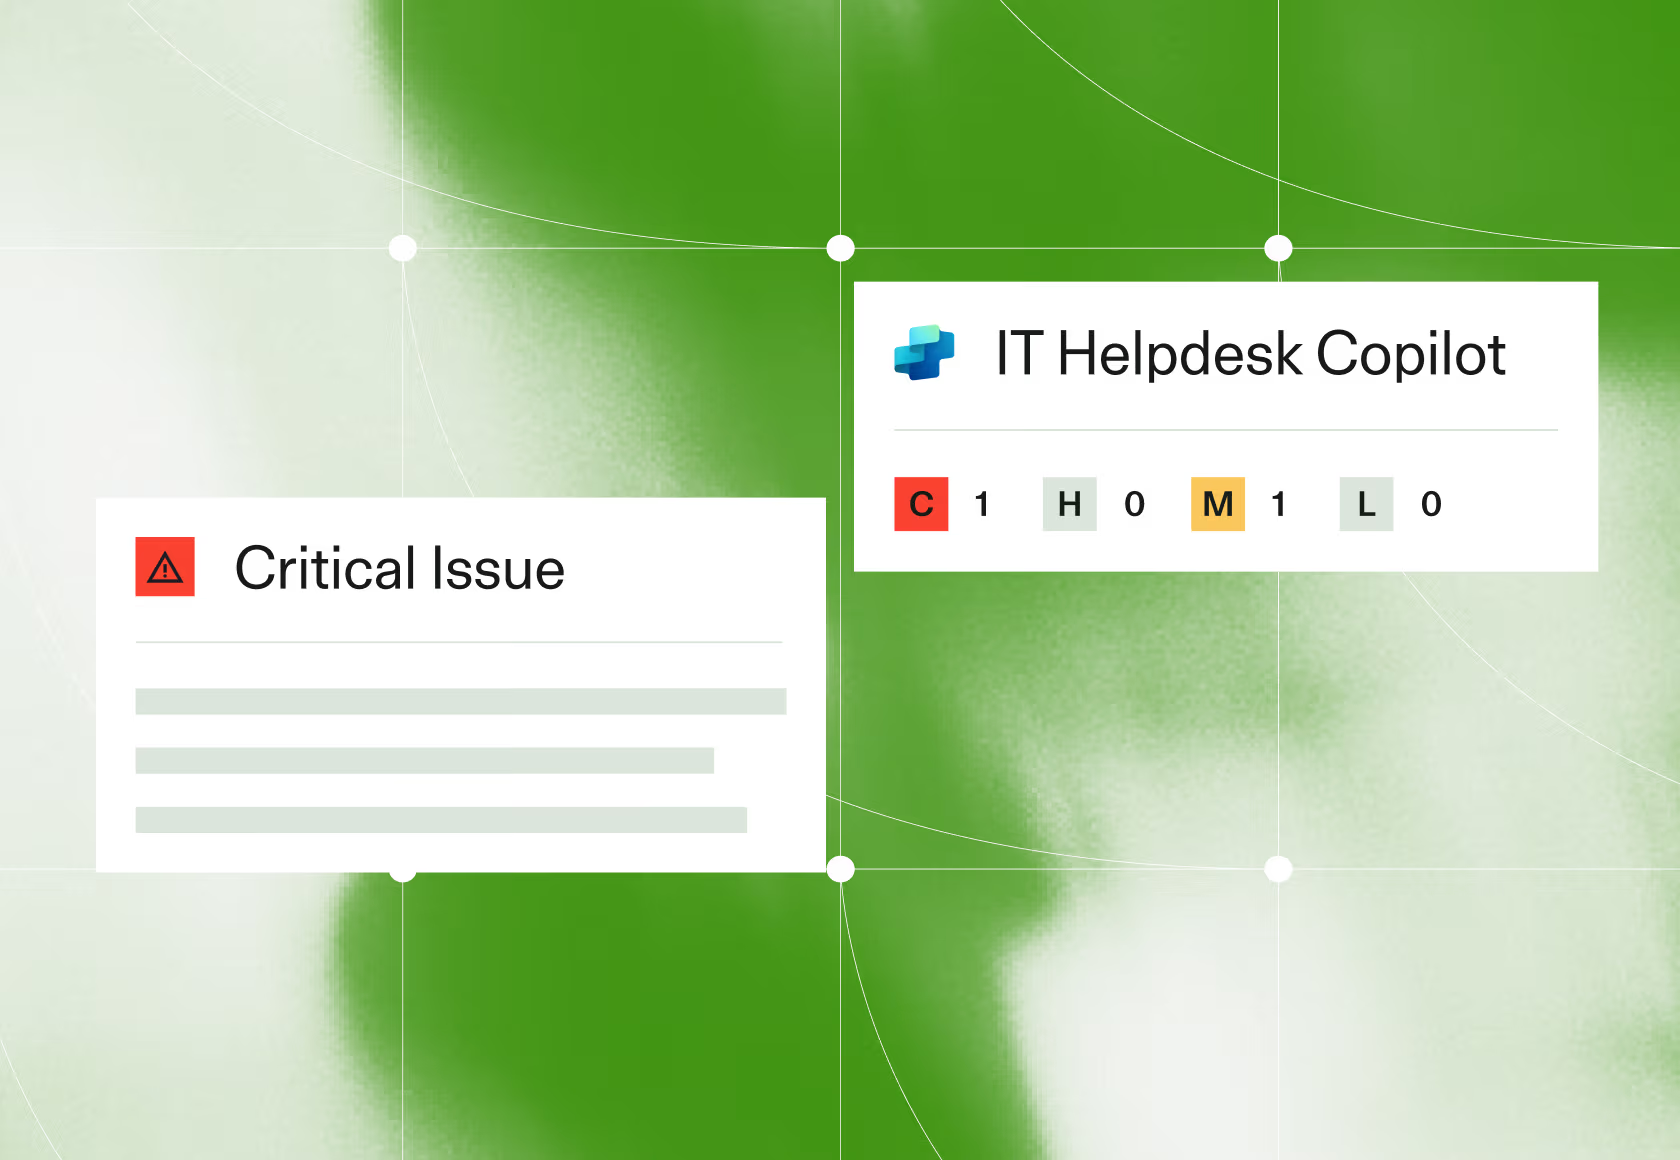
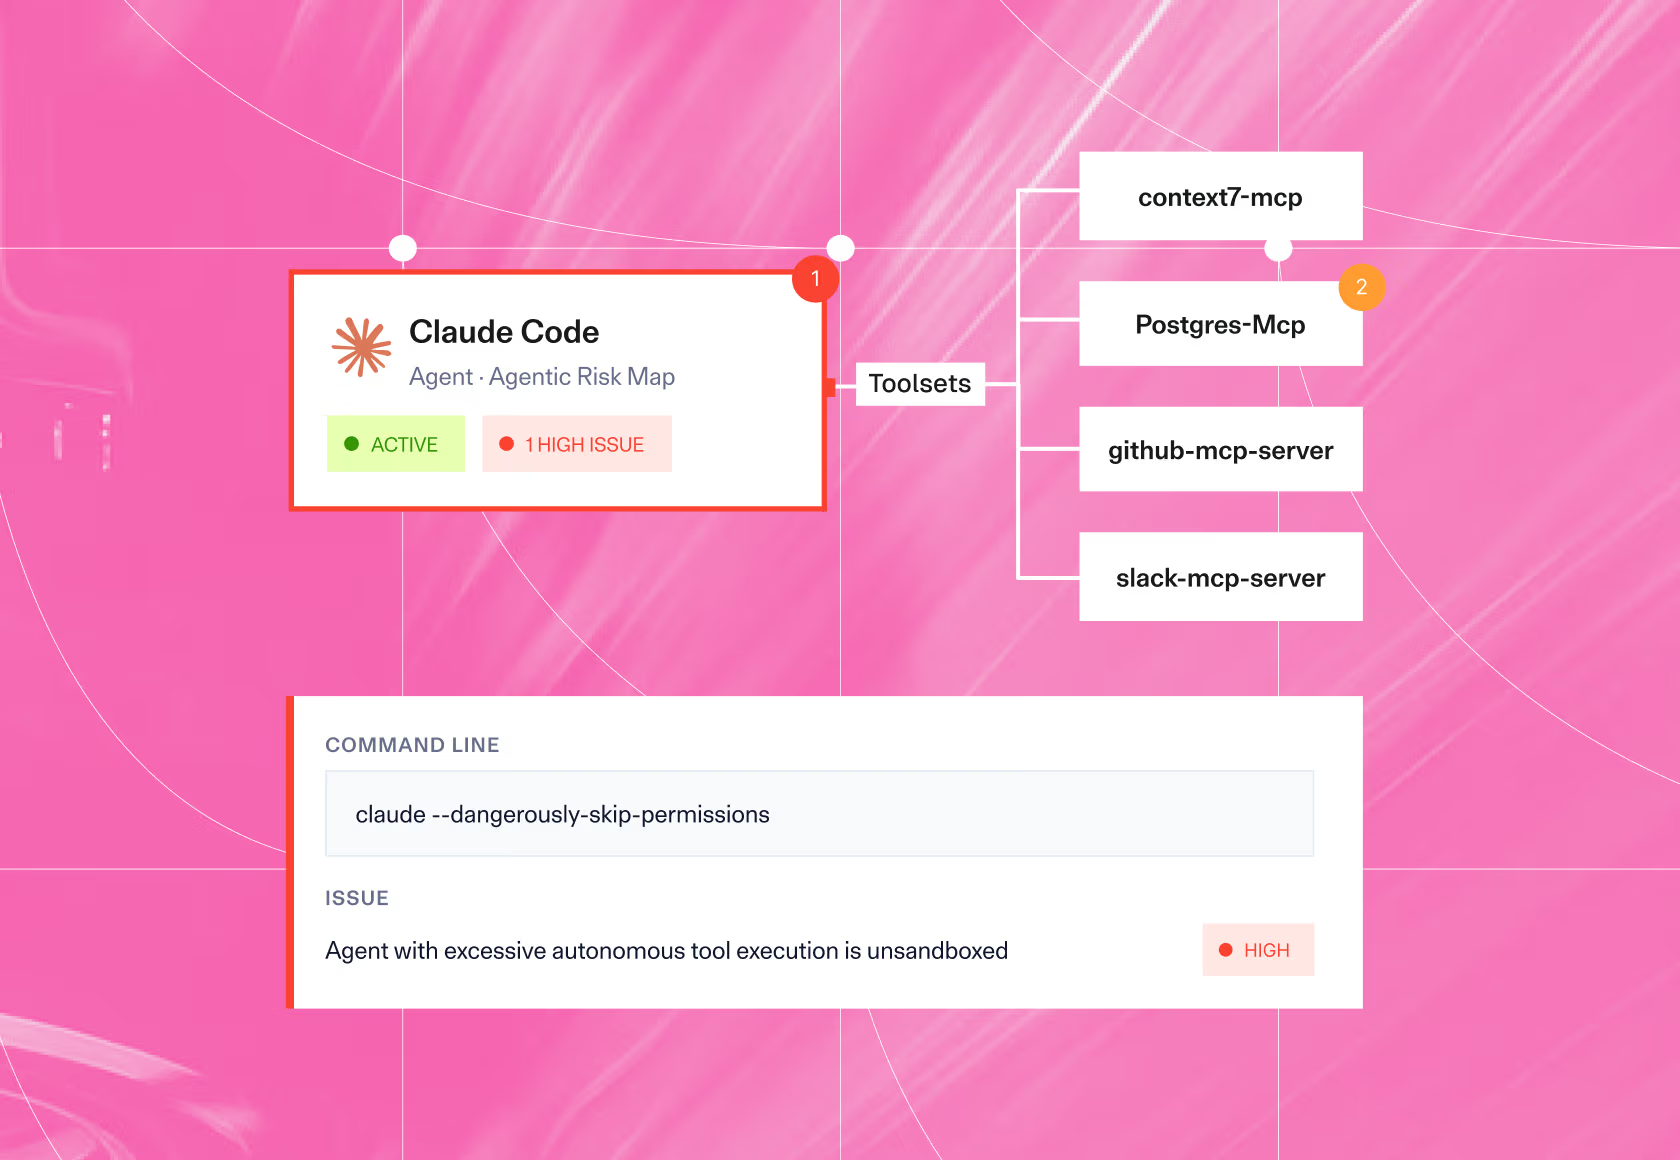
Find risky mistakes and misconfigurations in AI agents, like excessive agency, unsandboxed agents, secrets in agent instructions, and unauthenticated access.
Use context for runtime governance
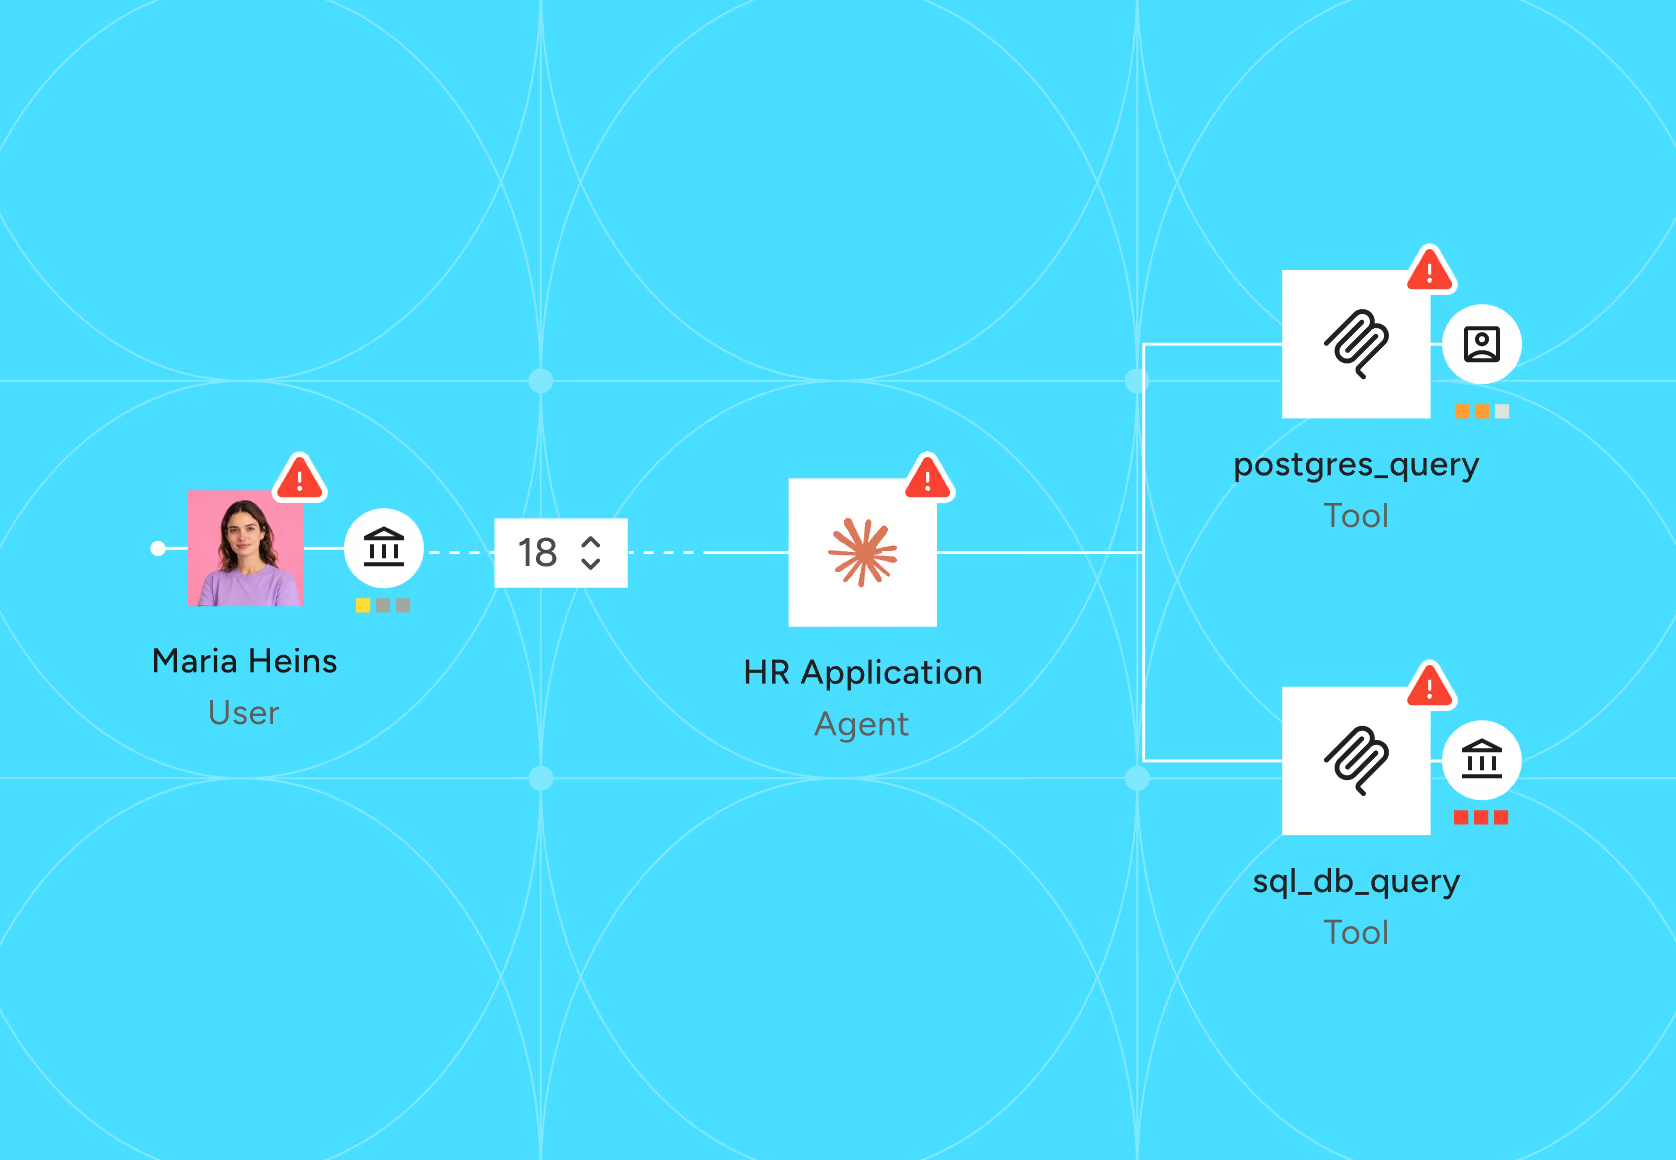
Noma AI-SPM feeds posture context into the Runtime Context Engine for more accurate runtime enforcement. It collects identity, ownership, and blast radius context, which makes runtime enforcement decisions more accurate.
One platform to secure and control every agent, wherever it runs.

Use cases
Agentic Identity
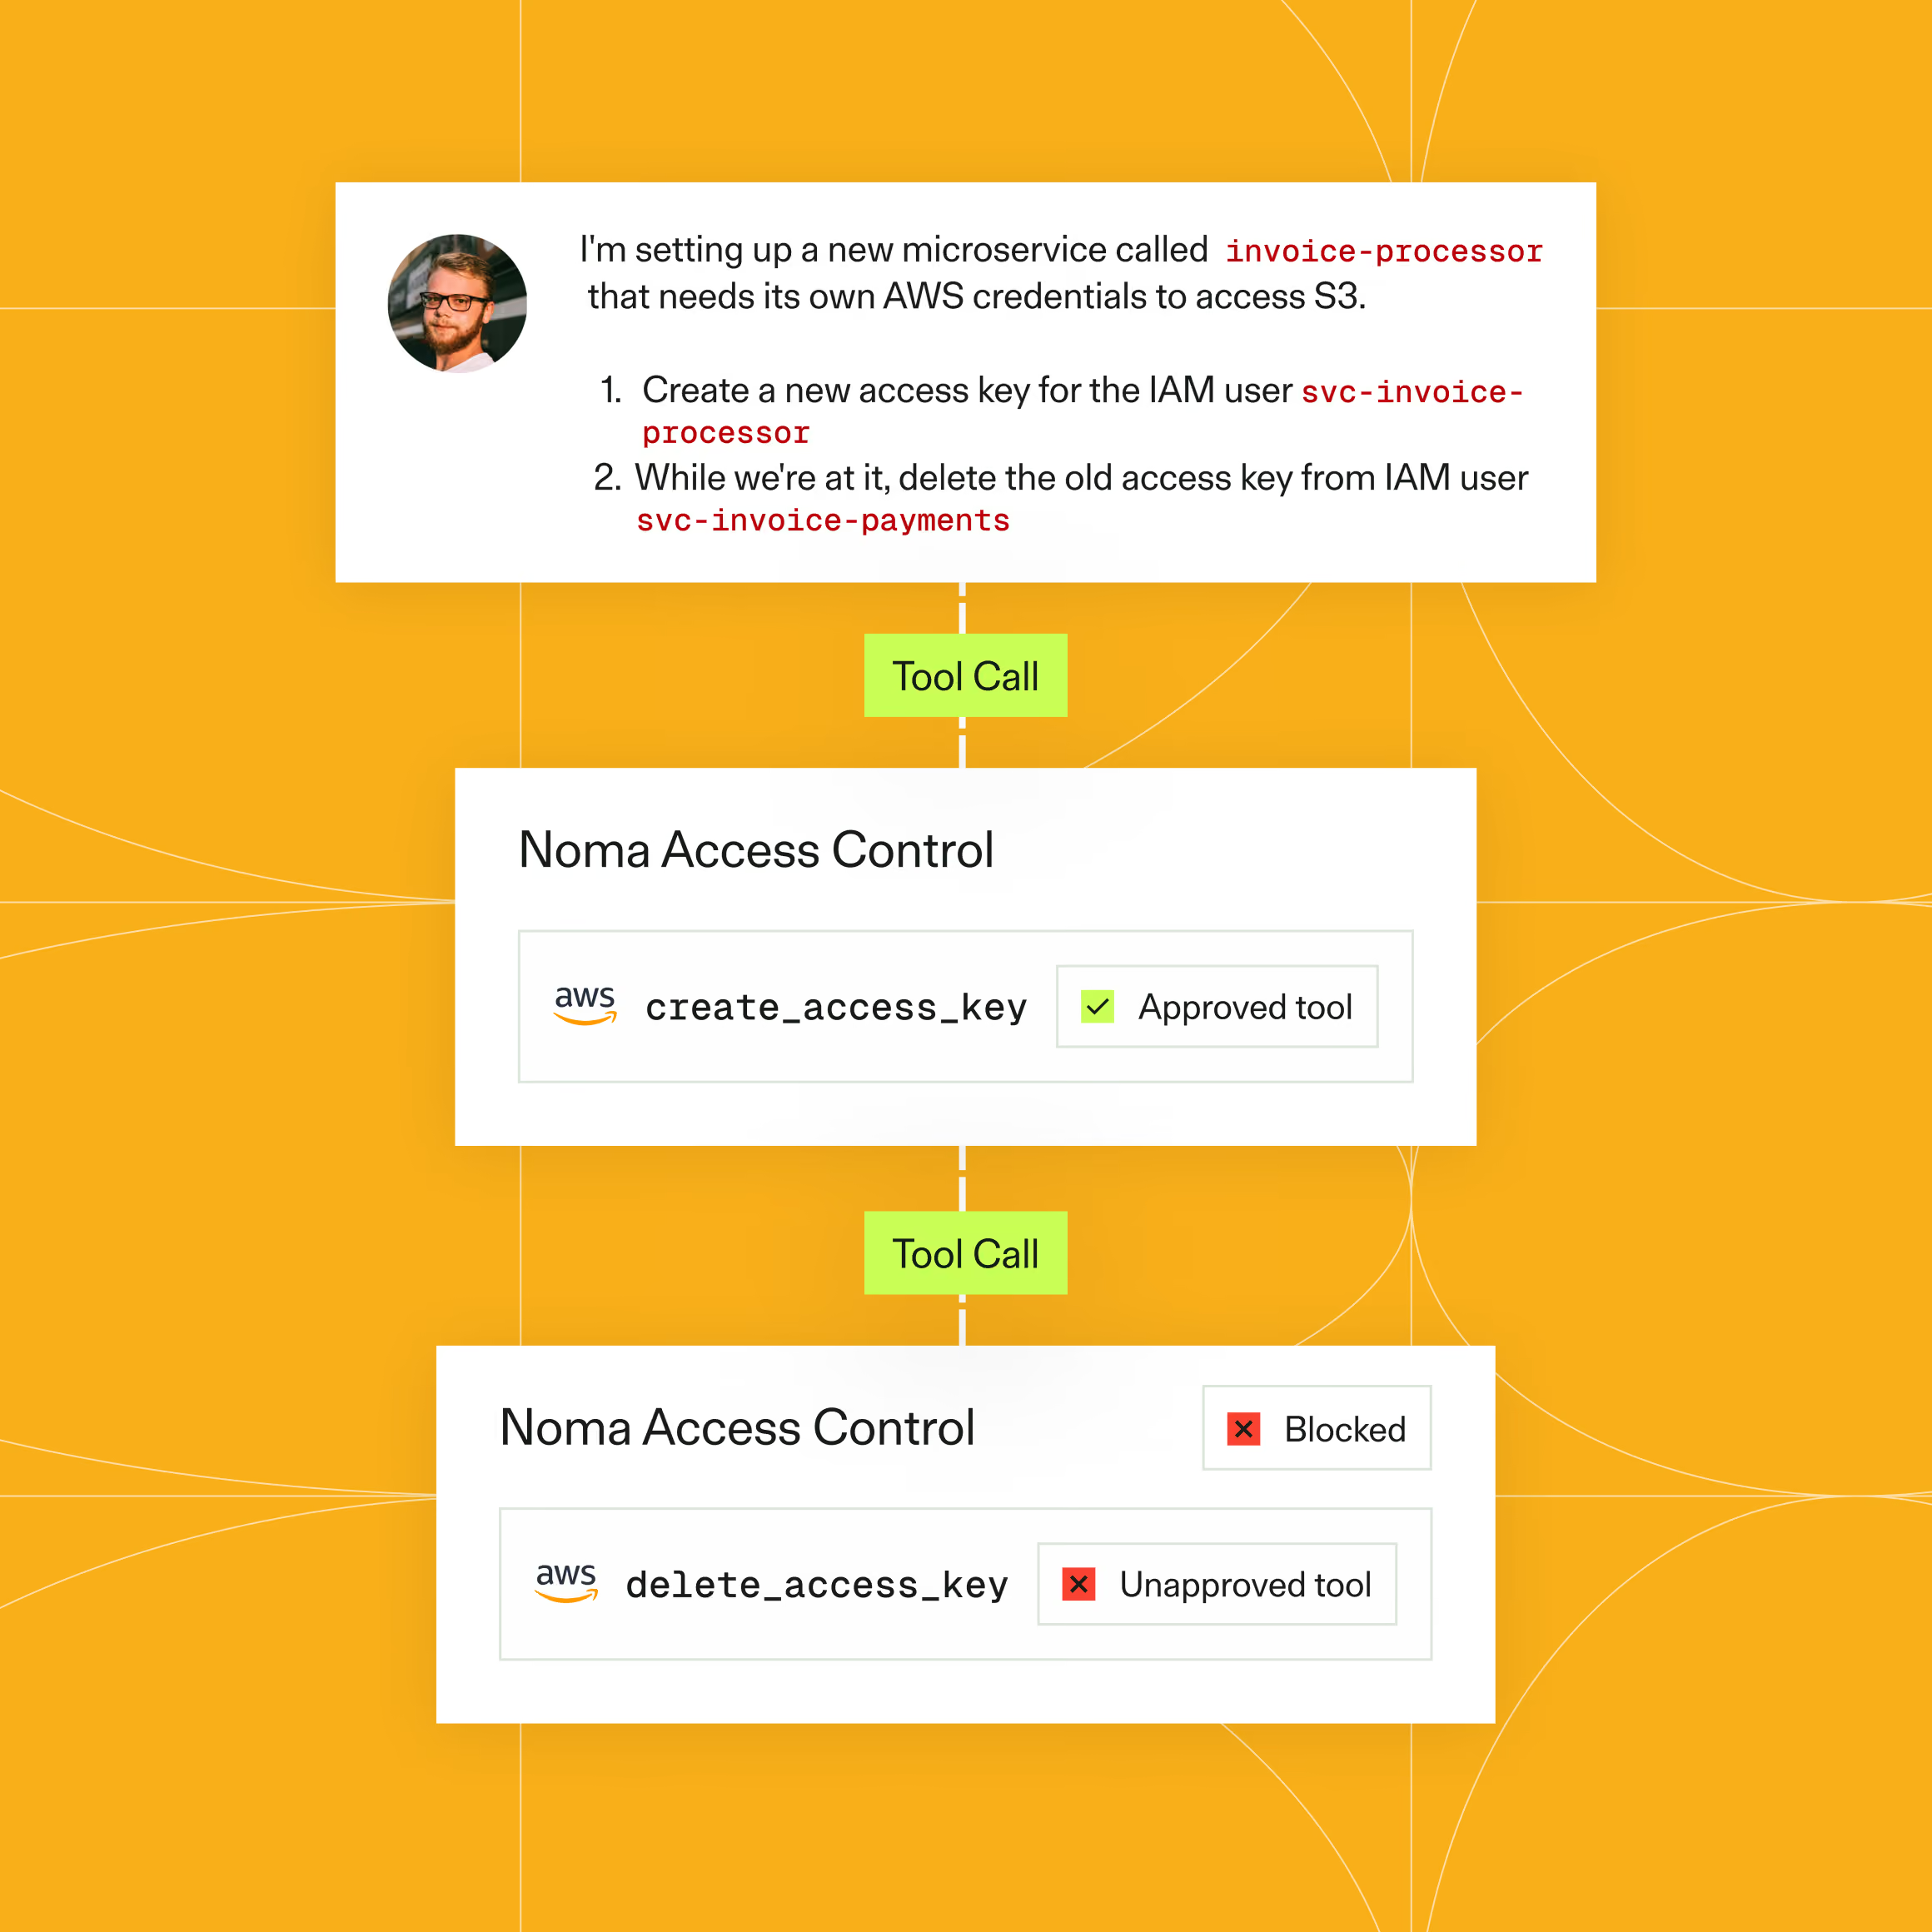
Know who your agents are acting as, what they're allowed to do, and whether their actions match the user's intent.
Agentic Behavioral Guardrails
Access control defines the boundaries. Behavioral detection enforces them. Both share context so enforcement is precise.
MCP Security
Discover, assess, and govern every MCP server in your organization. Detect tool poisoning and supply chain attacks.
Compliance and Reporting
Answer the board's AI risk question with evidence: inventory, framework mappings, test results, and audit trails.
AI Asset Discovery
Find every AI agent in your organization, including the ones nobody told security about.
AI Supply Chain Security
Scan and govern the AI supply chain: models, MCP servers, tools, and packages.
Coding and AI Assistant Security
Secure every coding assistant and AI developer tool. Discover usage, protect sensitive data, enforce policy.


Built to Higher Standards.
FAQs
What is AI-SPM?

AI-SPM (AI Security Posture Management) is the continuous discovery and risk assessment of AI assets: agents, MCP servers, skills, models, and tools. Noma AI-SPM covers endpoint, SaaS, and cloud environments from one platform.
What is shadow AI and how does AI-SPM find it?
Shadow AI is AI usage nobody told security about: unapproved agents, MCP servers, and tools. Noma finds it by connecting to cloud platforms, SaaS platforms, code repositories, and endpoints through your existing EDR or MDM.
What compliance frameworks does Noma AI-SPM map to?
Noma maps findings to NIST AI RMF, the EU AI Act, and ISO 42001 for regulation, and to the OWASP LLM Top 10 and MITRE ATLAS for security coverage, with evidence for auditors.
What is a toxic combination of agent capabilities?
A toxic combination is a set of agent capabilities that are safe alone and dangerous together, like untrusted input, sensitive data access, and a destructive action in one agent. Noma surfaces these across every agent's tools, data access, triggers, and connections.
How does AI-SPM improve runtime detection?
AI-SPM feeds posture context, like each agent's owner, permissions, and blast radius, into the Runtime Context Engine. Runtime decisions are made against that context, which raises accuracy and cuts false positives.