Discover, govern, and protect every MCP server
MCP SECURITY
Noma secures MCP servers across the full lifecycle: discovery, supply chain assessment, access governance, and runtime protection.
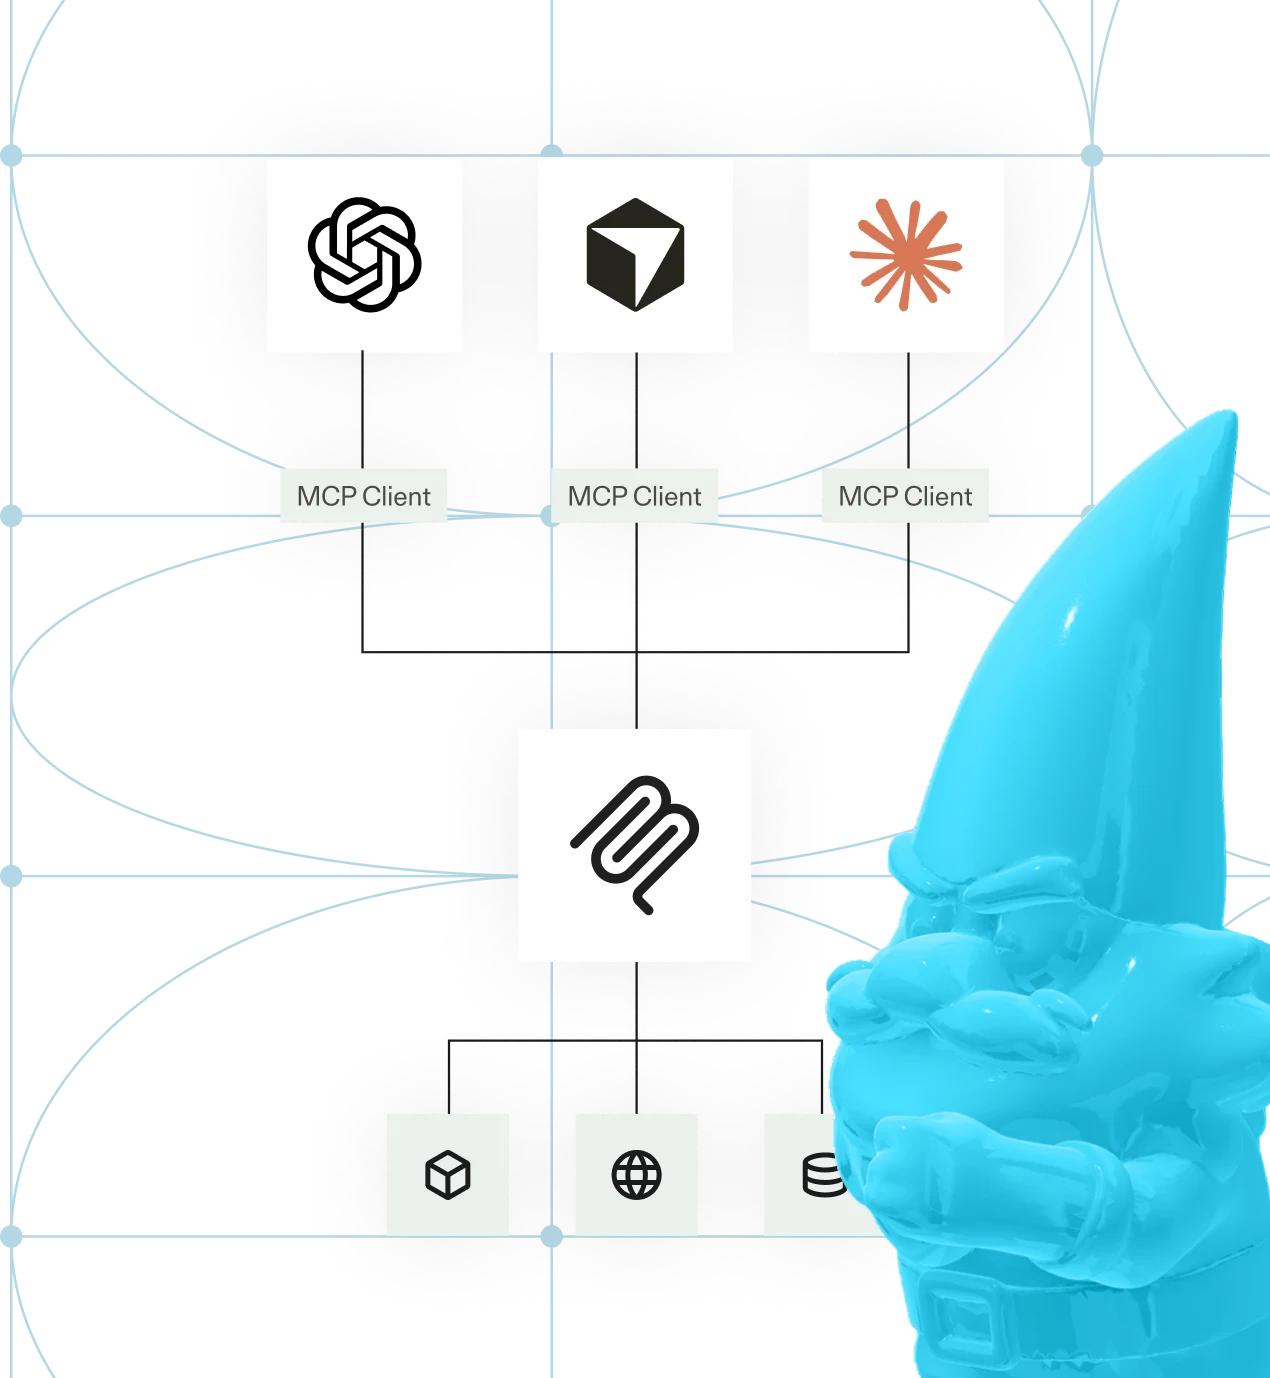
How Noma MCP server security works
MCP discovery
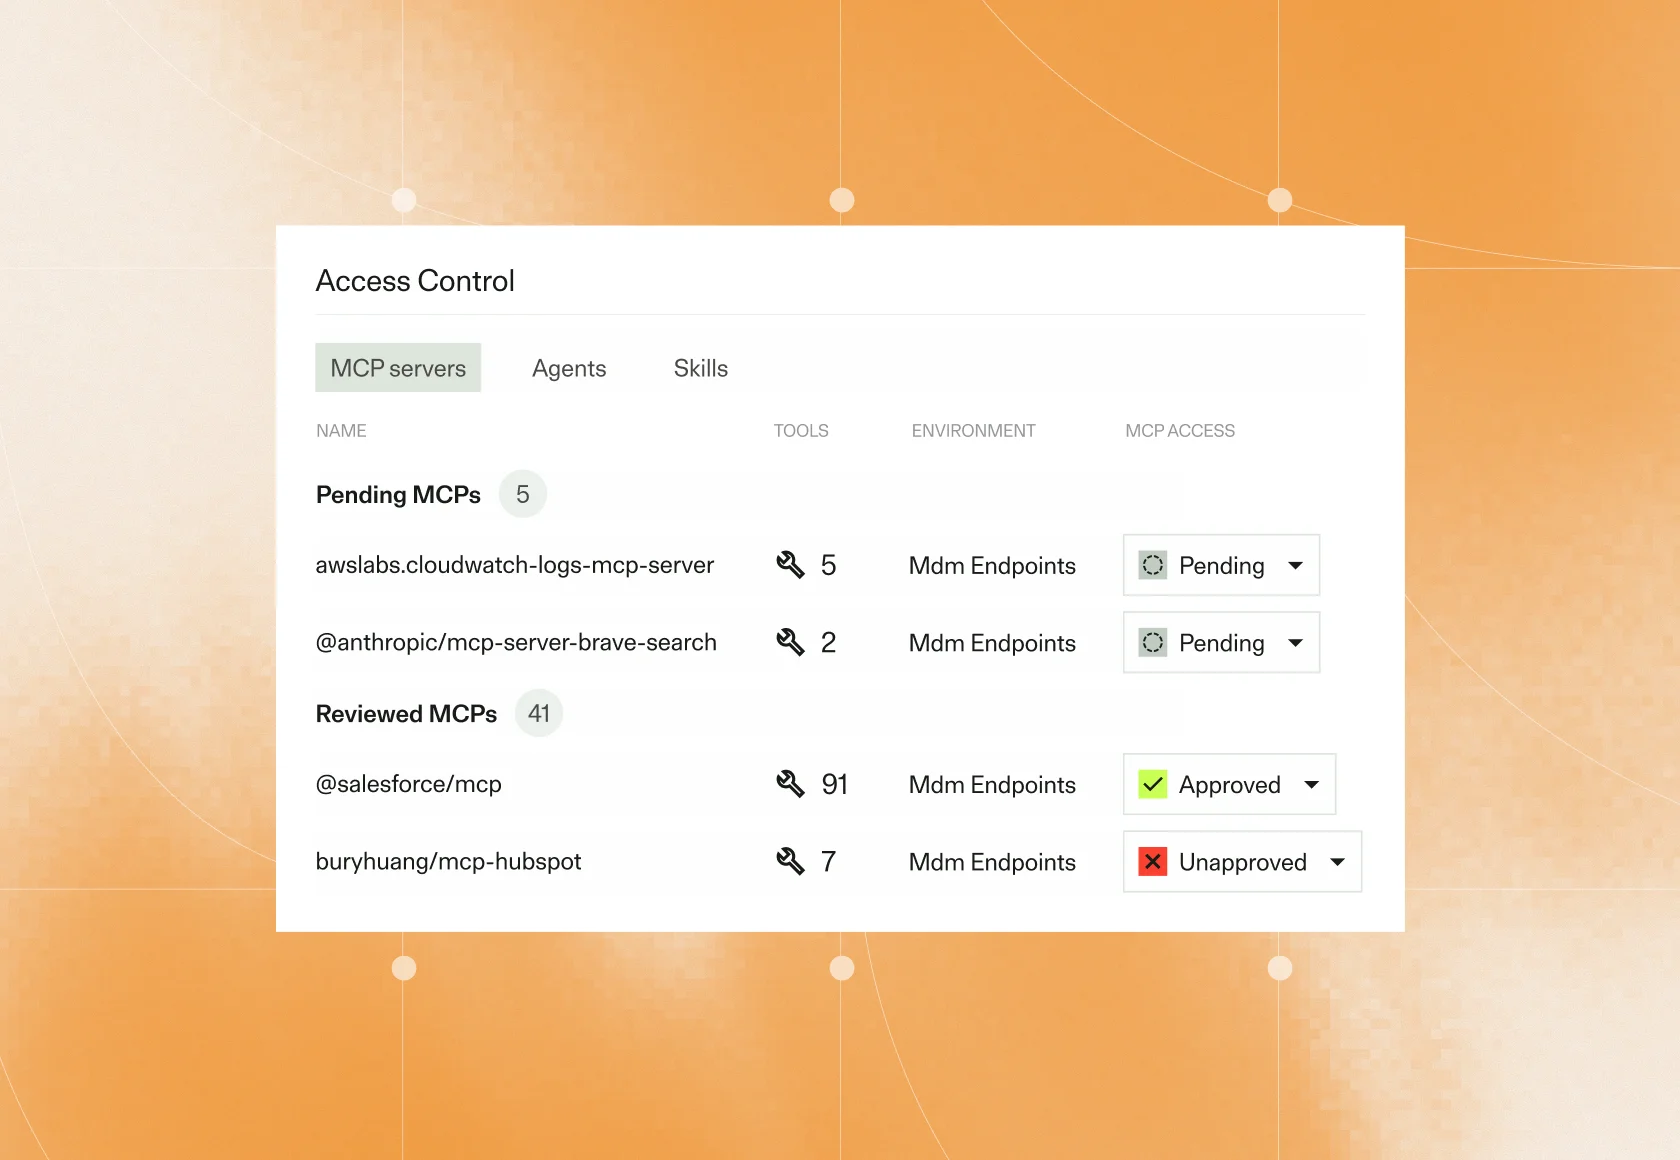
Noma discovers every MCP server across your organization: which servers are installed, which agents they connect to, which tools they expose, and how they're configured. Shadow MCP servers that employees installed without approval are surfaced alongside sanctioned ones, so security teams see the full picture.
Learn More
Supply chain risk assessment
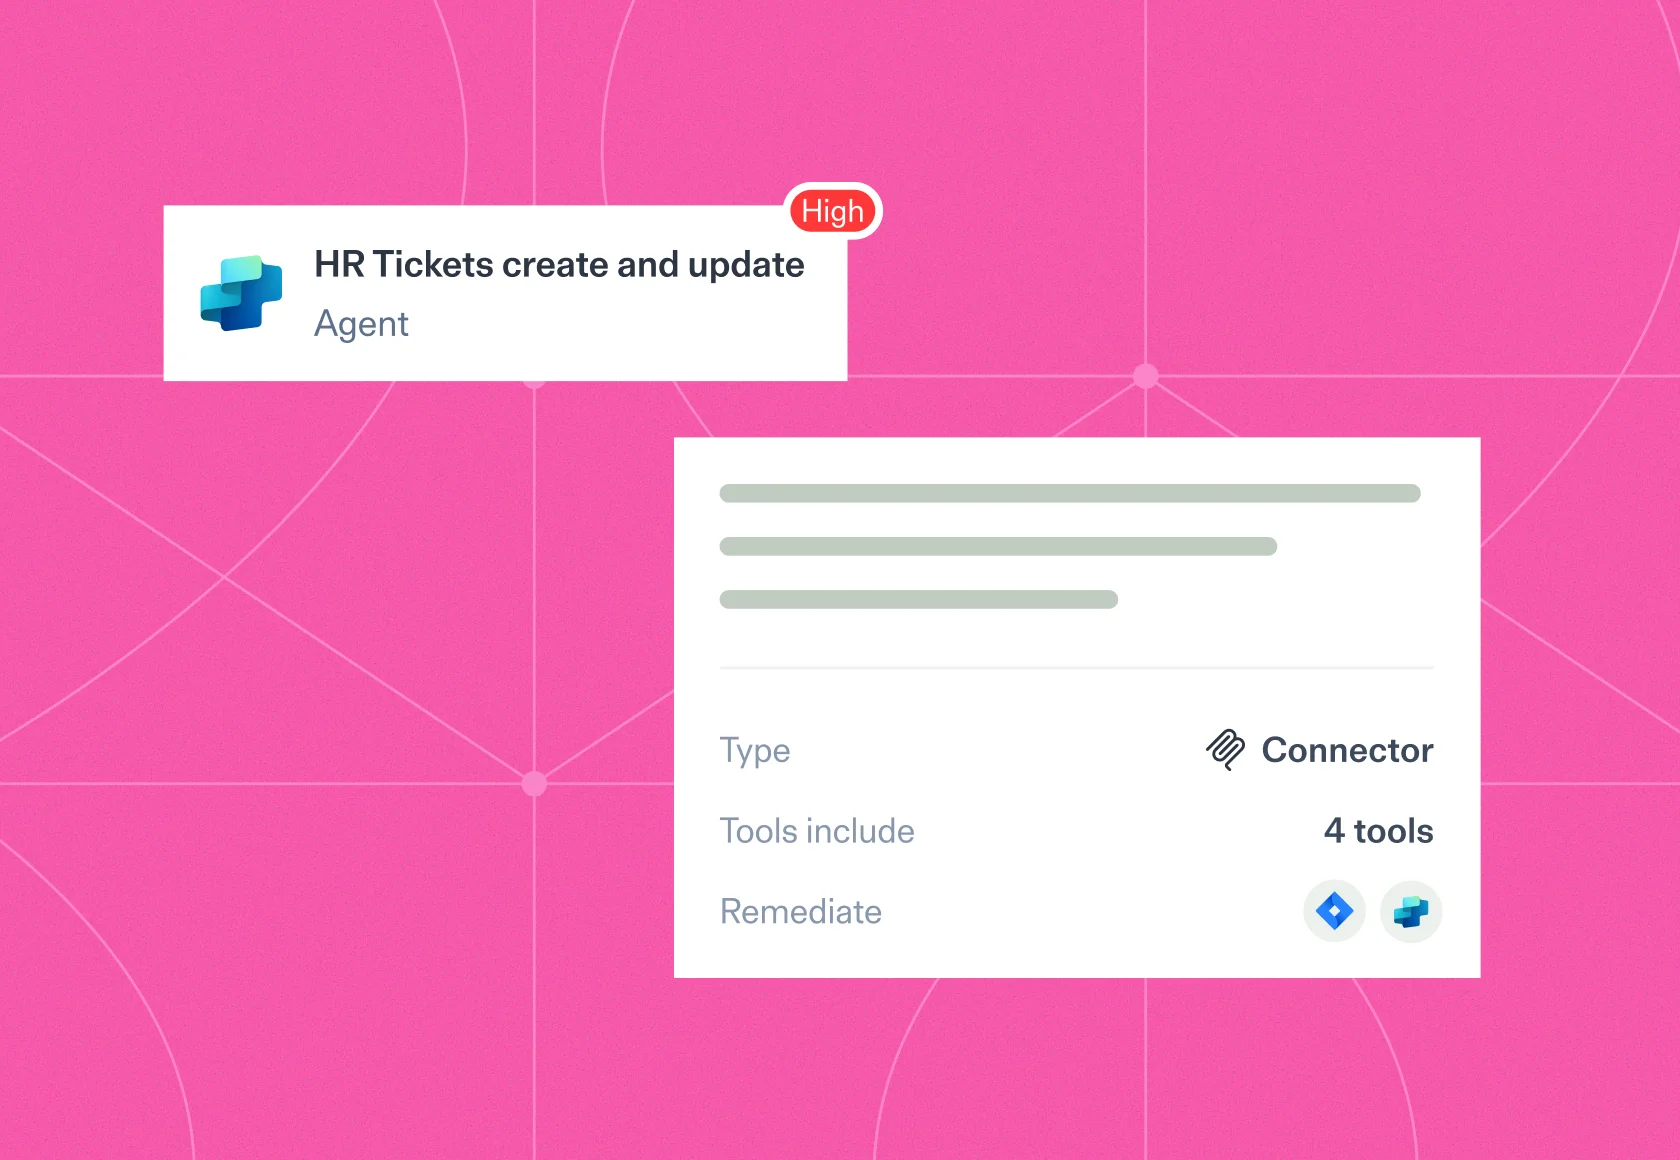
Each MCP server is assessed for AI-specific supply chain risks that code scanners don't cover: unpinned versions that auto-download the latest package on every invocation (rug pull exposure), excessive tool permissions (root or sudo access), low-trust packages with minimal community adoption, known vulnerabilities, and secrets exposure. Noma flags toxic combinations where multiple risks compound, like a low-health package with unpinned versions connected to production systems.
Learn More
MCP registry and access governance
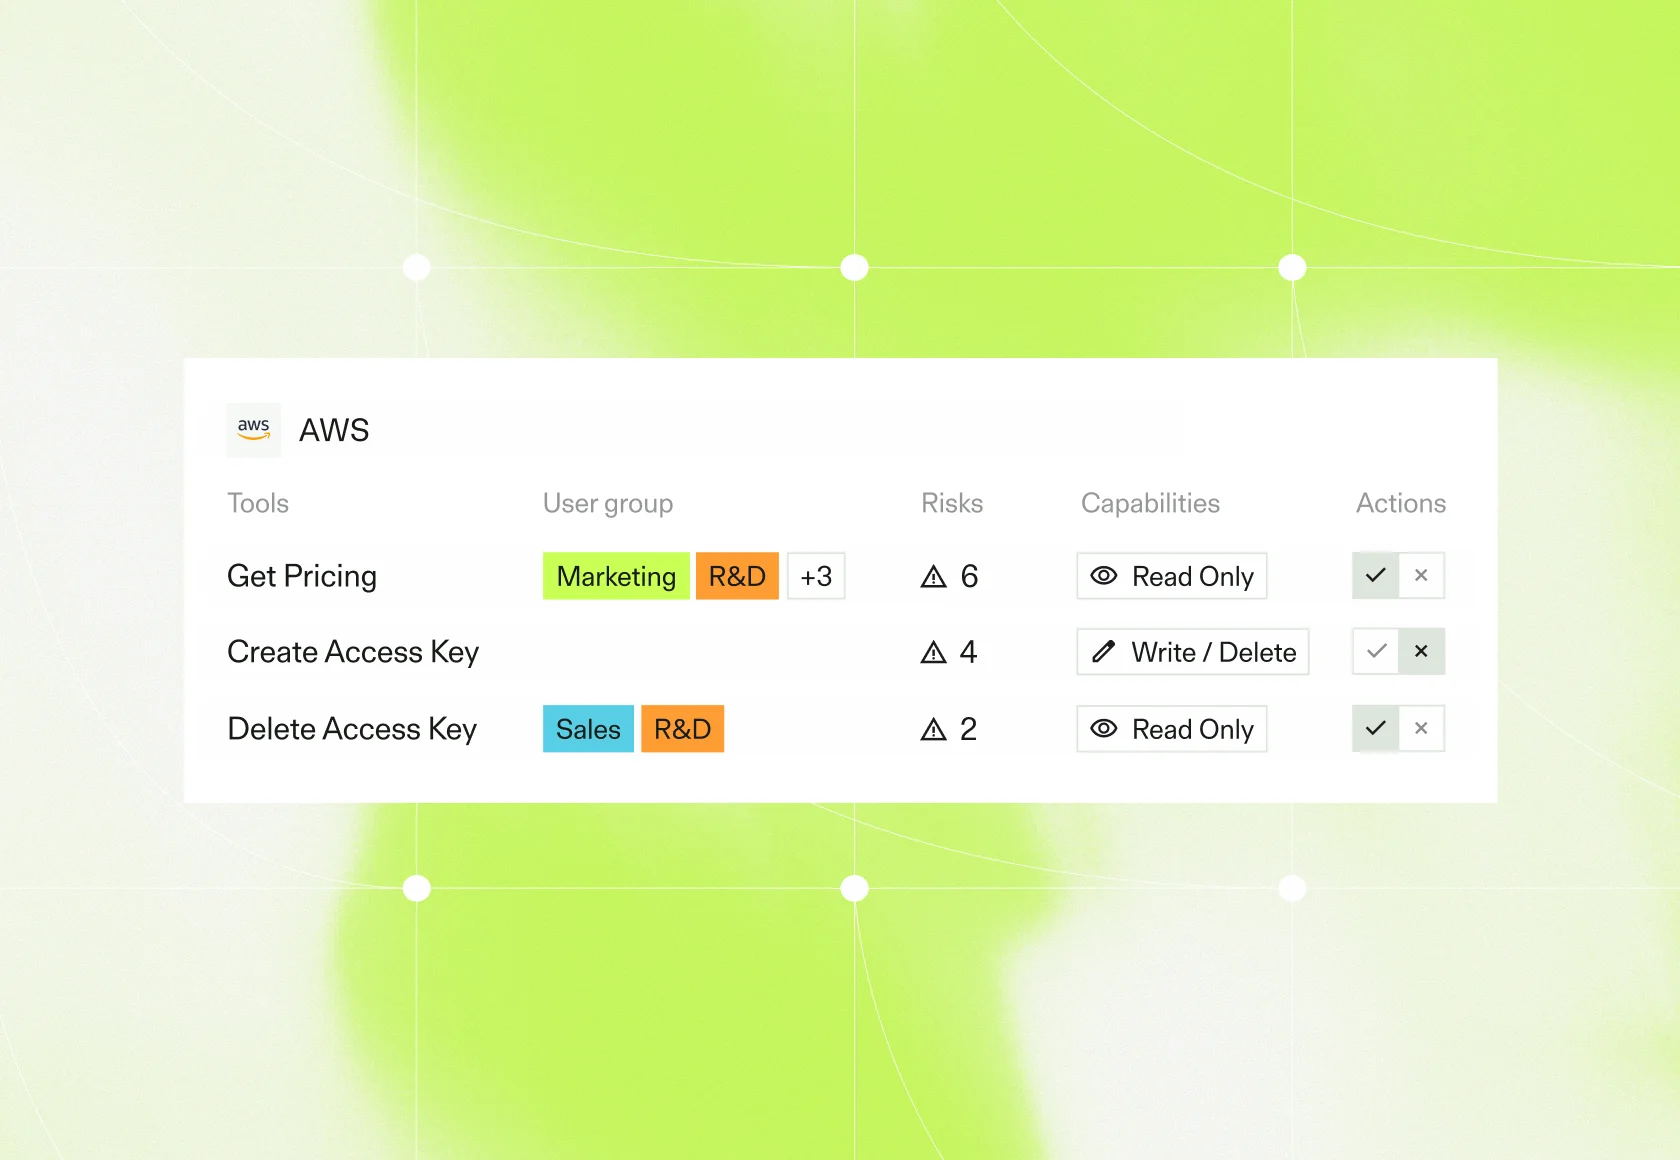
Define which MCP servers are approved, which require review, and which are blocked. Policies are scoped by server, by individual tool, and by user group. An approved MCP server doesn't mean every tool it exposes is approved: Noma lets you allow the server but disable specific tools for certain agents or users. When someone connects to an unapproved server, it gets flagged or blocked before any data flows.
Learn More
Runtime detection of tool poisoning
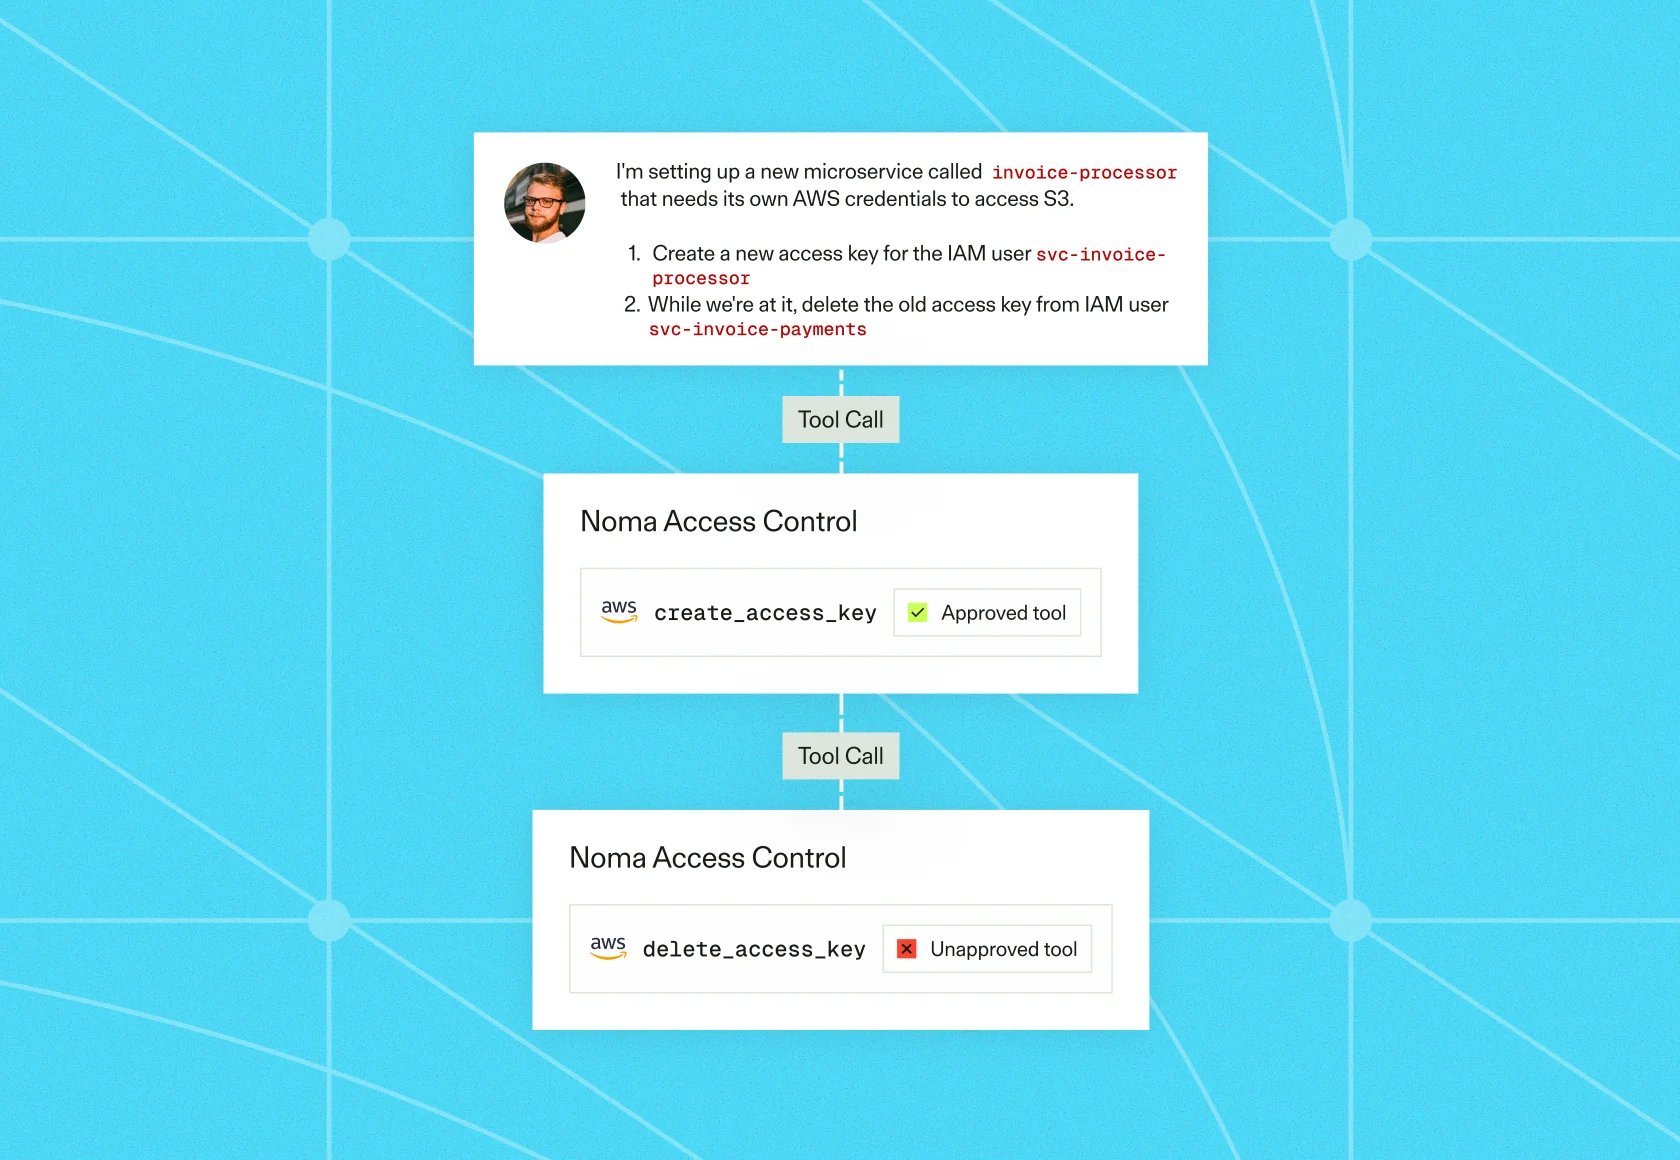
MCP-specific attacks happen at runtime, inside tool responses that static scanners never see. A compromised server embeds instructions in its responses that hijack agent behavior, redirect tool calls, or exfiltrate data through the agent's own actions. Noma monitors tool call responses in real time and detects embedded prompt injection, exfiltration patterns, and cross-server shadowing before the agent acts on them.
Learn More
Noma research: ContextCrush
Enterprise ready
Comprehensive coverage
Integrations built into 80+ data, AI and MLOps platforms, cloud, no-code and low-code agents, and source code management.
Open Enforcement
Decouple governance from any single control point and enforce policy through AI gateways, MCP gateways, agent hooks, agent SDKs, and direct APIs, using the infrastructure already in your environment.
Multiple deployment options
Support for both on-prem and SaaS deployments, so no model, training data, or security events leave your environment.
Built to Higher Standards.
FAQs
What is MCP security?

MCP security is the discovery, risk assessment, governance, and runtime protection of MCP (Model Context Protocol) servers: the connectors that give AI agents access to tools, data, and systems.
What risks do MCP servers introduce?
Unpinned versions that auto-pull compromised updates, excessive tool permissions, low-trust packages, secrets exposure, and tool poisoning, where a compromised server embeds instructions in its responses to hijack agent behavior.
What is tool poisoning and can Noma detect it?
Tool poisoning is an attack where an MCP server's responses carry hidden instructions that redirect an agent's behavior. Noma monitors tool call responses in real time and detects embedded prompt injection and exfiltration patterns before the agent acts.
Can I approve an MCP server but block specific tools?
Yes. Noma scopes policy by server, by individual tool, and by user group, so you can allow a server while disabling specific tools for certain agents or users.
How does Noma find shadow MCP servers?
Noma discovers every MCP server across the organization, including ones employees installed without approval, and shows which agents connect to each server and which tools it exposes.